

On this page
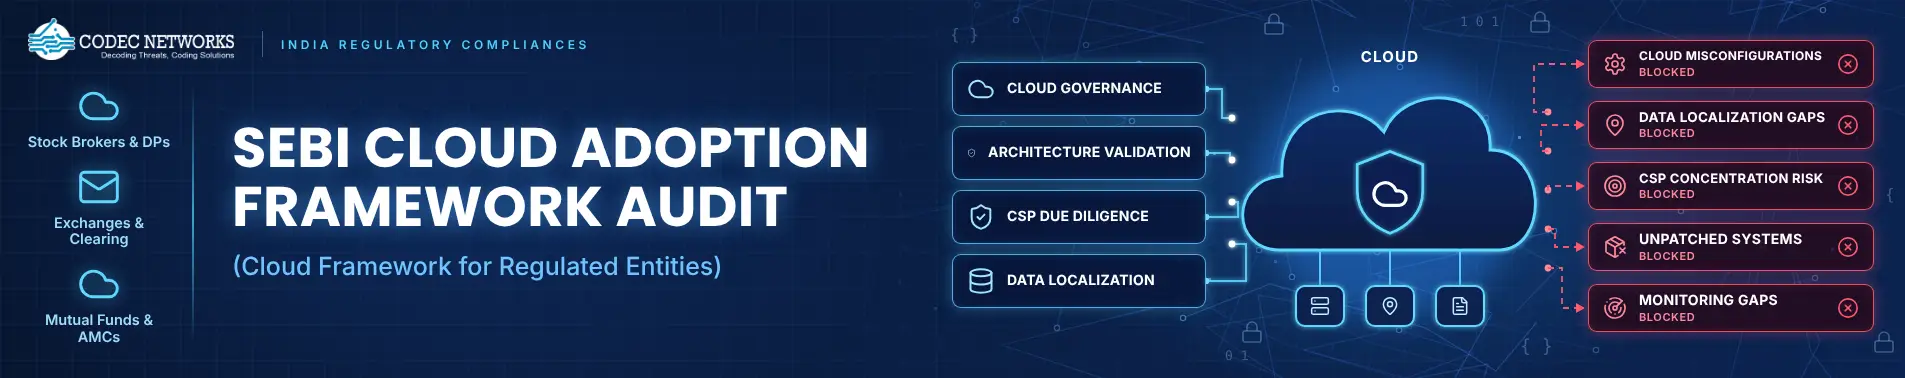

SEBI Cloud Adoption Framework Audit Service
Codec Networks is an Information Security Auditing Organization, providing independent, evidence-based and risk-focused audits to help SEBI-regulated entities adopting public, community or hybrid cloud services under SEBI Circular No. SEBI/HO/ITD/ITD_VAPT/P/CIR/2023/033 dtd. March 06 2023. The service evaluates cloud governance, CSP selection and due diligence, data ownership and localization, allocation of responsibilities, cybersecurity controls, contractual and regulatory audit rights, business continuity, disaster recovery, cyber resilience, and vendor lock-in or concentration risks.
Codec Networks is a CERT-In empanelled auditing organization mandated to offer this service
Following applicable CERT-In auditing guidelines, Codec Networks performs engagement scoping, asset and cloud-inventory validation, document and contract review, stakeholder interviews, cloud architecture and configuration assessment, control design and operating-effectiveness testing, and appropriately authorized vulnerability assessment or penetration testing.
The engagement may provide an executive report, detailed findings, clause-wise compliance mapping, risk ratings, responsibility-matrix validation, corrective-action recommendations and retesting or closure verification.The service provides reasonable, point-in-time assurance within the mutually agreed scope, audit period and Rules of Engagement. Responsibility for regulatory compliance, control operation, risk acceptance and remediation remains with the regulated entity and its management.
SEBI Cloud Adoption Framework Audit Service
INDUSTRY SIGNIFICANCE AND SERVICE RELEVANCE
Why this service matters to your industry, where it fits in your security
rogramme, and what your organisation gains from it.
Cloud adoption enables SEBI-regulated entities to improve scalability, availability, innovation and operational efficiency. However, migration of regulated workloads to cloud environments also introduces material risks involving investor information, data localization, privileged access, multi-tenancy, service availability, cyber incidents, third-party dependency and concentration with a limited number of Cloud Service Providers.
The SEBI Cloud Adoption Framework is therefore significant because it establishes that outsourcing cloud infrastructure does not transfer regulatory accountability. Regulated entities remain responsible for protecting their information assets, maintaining resilient securities-market operations and ensuring that SEBI and authorized auditors retain appropriate access to information and evidence.
Key industry implications include:
- Stronger Board and senior-management oversight of cloud adoption.
- Greater scrutiny of CSPs, managed service providers and subcontractors.
- Mandatory attention to data ownership, localization and cryptographic-key control.
- Contractual allocation of responsibilities, audit rights and incident obligations.
- Improved BCP, disaster recovery, portability and exit preparedness.
- Ongoing monitoring of cloud security, concentration and systemic risks.
Codec Networks’ Audit Service helps regulated entities independently evaluate whether their cloud governance, architecture, contracts, security controls and operational practices are aligned with the applicable SEBI requirements. The service is relevant at the pre-adoption, migration, pre-production, periodic assurance and major-change stages of the cloud lifecycle.
Through a risk-based and evidence-driven audit approach, Codec Networks may assess:
- Cloud inventory, deployment models, critical workloads and data flows.
- Board-approved cloud strategy, policies and risk-management arrangements.
- CSP eligibility, due diligence, assurance status and subcontractor dependencies.
- Data localization, encryption, key management and regulatory access.
- Identity, privileged access, configuration, vulnerability, logging and SOC controls.
- Contractual responsibilities, audit rights, incident cooperation and liability provisions.
- Backup, BCP/DR, cyber resilience, vendor concentration, portability and exit controls.
The service enables management to identify clause-wise compliance gaps, control weaknesses, unclear responsibilities and residual risks before they result in regulatory, operational or investor-impacting consequences. Codec Networks provides point-in-time, scope-limited independent assurance and practical remediation recommendations.
Codec Networks’ SEBI Cloud Adoption Framework Audit Service is intended for SEBI-regulated entities that use, propose to use or materially depend upon public, community or hybrid cloud services for regulated business activities, investor services, market infrastructure or supporting technology operations.
Applicable customers may include:
- Recognized Stock Exchanges.
- Clearing Corporations.
- Depositories.
- Stock Brokers, through the applicable Stock Exchanges.
- Depository Participants, through the applicable Depositories.
- Asset Management Companies and Mutual Funds.
- Qualified Registrars and Share Transfer Agents.
- KYC Registration Agencies.
- Other SEBI-regulated entities brought within scope through subsequent SEBI directions.
- Regulated entities using CSPs, SaaS/PaaS providers, MSPs, system integrators or material cloud subcontractors.
The service is particularly relevant for entities planning cloud adoption, migrating critical workloads, introducing new cloud services, conducting pre-production reviews, undertaking periodic cyber or systems audits, responding to regulatory observations, or validating remediation of previously reported findings. Final applicability and scope should be determined from the entity’s SEBI registration category, cloud deployment model, system criticality and current SEBI directions.
Codec Networks provides an independent, risk-based and evidence-driven assessment that helps regulated entities understand whether their cloud governance, contracts, configurations and operating controls are aligned with the SEBI Cloud Adoption Framework and other applicable cybersecurity requirements.
Key customer benefits include:
- Improved visibility of cloud assets, accounts, workloads, data flows and service-provider dependencies.
- Identification of clause-wise compliance gaps and unclear control responsibilities.
- Independent assessment of CSP due diligence, assurance status and subcontractor risks.
- Validation of data localization, encryption, key management and regulatory-access arrangements.
- Evaluation of IAM, privileged access, logging, monitoring, vulnerability and incident-response controls.
- Review of cloud contracts, audit rights, service levels, exit clauses and data-expunging provisions.
- Assessment of BCP/DR, recovery testing, cyber resilience and concentration risks.
- Prioritized findings supported by risk ratings, objective evidence and practical remediation recommendations.
- Management and Board-level visibility of material cloud risks and corrective-action priorities.
- Improved preparedness for applicable SEBI cyber audits, systems audits, VAPT and regulatory reporting.
The service provides reasonable, point-in-time assurance within the agreed scope and audit period.
AUDIT FEATURES AND DELIVERY FRAMEWORK
Cybersecurity at Codec Networks means comprehensive features,scalable offerings,
effective delivery methods, performance-driven
Codec Networks provides independent, risk-based and evidence-driven audit services to assess cloud governance, regulatory compliance, cybersecurity controls and operational resilience of SEBI-regulated entities. Each engagement is performed under an agreed scope, audit period, evidence protocol and Rules of Engagement, taking into account the entity’s SEBI category, cloud architecture, data sensitivity, system criticality and service-provider dependencies.
Audit Service Features
- Cloud governance and risk assessment: Review of the Board-approved cloud strategy, cloud risk-management approach, policies, accountable CISO or security resource, annual reviews, monitoring and exit preparedness.
- Cloud inventory and architecture validation: Assessment of cloud accounts, subscriptions, regions, applications, APIs, data stores, logs, backups, cryptographic services and material dependencies supporting regulated operations.
- CSP eligibility and due diligence: Verification of applicable MeitY empanelment, STQC or equivalent audit status, underlying infrastructure arrangements, PaaS/SaaS dependencies, financial and operational capability, personnel screening and periodic monitoring.
- Data ownership and localization: Evaluation of the regulated entity’s ownership and accessibility of data, logs and encryption keys; India-based storage and processing; regulatory visibility; retention; and secure expunging arrangements.
- Responsibility and contractual compliance: Verification that every cloud activity and applicable regulatory clause has an explicitly identified responsible party. Joint activities are examined at sub-task level, including responsibilities of CSPs, MSPs, system integrators and material subcontractors.
- Cloud security-control assessment: Review and testing of vulnerability and patch management, VAPT, IAM, privileged access, MFA, multi-tenancy, security monitoring, SOC integration, incident management, interfaces, network segmentation, encryption, endpoint protection, secure development, backup and recovery.
- Authorized technical assessment and VAPT: Risk-based configuration review and appropriately authorized vulnerability assessment or penetration testing of in-scope cloud infrastructure, applications, APIs and management interfaces. Testing is performed under approved targets, techniques, timelines and safety conditions.
- Audit rights and regulatory access review: Assessment of contractual provisions supporting audit, information access, supervisory review, search and seizure, forensic cooperation, provider audit reports and access to relevant subcontractor information.
- BCP, DR and cyber-resilience assessment: Evaluation of recovery arrangements, RTO/RPO, backup segregation, restoration testing, stakeholder-inclusive DR drills, cloud shutdown contingencies and unresolved resilience risks.
- Exit and concentration-risk review: Assessment of provider lock-in, portability, interoperability, concentration exposure, migration alternatives, exit triggers, termination assistance and permanent data deletion.
- Clause-wise reporting and remediation support: Delivery may include an executive report, detailed audit report, clause-wise compliance matrix, evidence index, risk-rated findings, responsibility matrix, management action plan and retest report.
Codec Networks follows an independent, risk-based and evidence-driven audit methodology aligned with applicable CERT-In auditing guidelines. Methodology is specifically tailored to SEBI’s Framework for Adoption of Cloud Services and, where applicable, the current CSCRF, related SEBI circulars and subsequent clarifications. The audit evaluates both control design and operating effectiveness across the regulated entity, CSP, PaaS/SaaS provider, MSP, system integrator and material subcontractors included within the agreed scope.
Eight-Stage Risk-Based Audit Methodology
1. Engagement Acceptance and Independence
Codec Networks evaluates auditor competence, independence, potential conflicts of interest, confidentiality requirements and engagement feasibility. The scope, audit period, responsibilities, deliverables, evidence protocol and authorized testing boundaries are documented through the engagement letter and Rules of Engagement.
2. Applicability and Scope Assessment
The applicable regulatory criteria and cloud audit universe are identified using the entity’s SEBI registration category, regulated activities, cloud deployment and service models, asset inventory, critical workloads, data flows, locations and service-provider dependencies.
3. Risk Assessment and Audit Planning
In-scope cloud services are risk-ranked considering business criticality, investor-data sensitivity, external exposure, privileged access, multi-tenancy, provider dependency, concentration, incident history and recovery requirements. Critical systems, mandatory clauses and high-risk dependencies receive greater audit depth.
4. Governance, Due-Diligence and Contract Review
The audit team reviews Board-approved cloud governance, risk assessments, policies, CSP eligibility, MeitY/STQC-related evidence, provider due diligence, responsibility matrices, contracts, audit rights, data-location arrangements, incident obligations, BCP/DR provisions and exit clauses.
5. Cloud Security-Control Assessment
Codec Networks assesses applicable controls for vulnerability and patch management, VAPT, secure configuration, IAM, privileged access, MFA, encryption, cryptographic-key management, logging, SOC integration, multi-tenancy, network security, secure development, backup, incident response and breach notification.
6. Evidence-Based Testing and Technical Validation
Control implementation and operating effectiveness are evaluated through document inspection, interviews, observation, sampling, configuration review, log analysis and reperformance. Appropriately authorized VAPT may be performed for in-scope cloud infrastructure, applications, APIs and management interfaces. Automated results are manually validated before reporting.
7. Finding Evaluation and Reporting
Findings are supported by objective evidence and evaluated according to regulatory impact, business criticality, likelihood, exploitability, control effectiveness and residual risk. Deliverables may include an executive report, detailed audit report, clause-wise compliance matrix, responsibility mapping, evidence index, risk-rated findings and management action plan.
The audit also examines whether responsibilities are clearly allocated to the RE, CSP, MSP or SI and incorporated into signed agreements.
8. Remediation and Closure Verification
Management responses, accountable owners and target dates are recorded. Closure is confirmed only after supporting evidence is reviewed and, where necessary, the affected control or vulnerability is retested. Accepted risk does not override a mandatory SEBI requirement or constitute regulatory waiver.
Audit Outcome
Codec Networks’ methodology helps the regulated entity obtain an independent view of:
- Clause-wise compliance status.
- Cloud governance and control maturity.
- Critical security and resilience gaps.
- CSP and subcontractor dependencies.
- Unclear or incomplete responsibility allocation.
- Priority remediation and residual risks.
- Readiness for applicable cyber audit, systems audit and VAPT reporting.
Please Note
The audit provides reasonable, point-in-time assurance within the agreed scope, period and evidence made available. Regulatory accountability, control operation, risk acceptance and remediation remain with the SEBI-regulated entity and its management.
Codec Networks adopts an independent, regulatory-led, risk-based and evidence-driven audit approach aligned with applicable CERT-In auditing guidelines. For the SEBI Cloud Adoption Framework, the approach evaluates whether the regulated entity has established effective governance, retained regulatory accountability and implemented proportionate controls across its complete cloud ecosystem.
The assessment is tailored to the entity’s SEBI category, regulated activities, cloud architecture, system criticality, data sensitivity and reliance on CSPs, PaaS/SaaS providers, MSPs, system integrators and material subcontractors.
Key Elements of Our Audit Approach
Regulatory-First Assessment
Mandatory requirements of the SEBI Cloud Adoption Framework, current CSCRF and applicable SEBI circulars take precedence over voluntary standards or CSP certifications. Each requirement is mapped to an accountable party, supporting evidence, audit procedure and conclusion.
Risk-Based Prioritization
Audit depth is determined by business criticality, investor-data sensitivity, internet exposure, privileged access, multi-tenancy, service-provider dependency, concentration risk, incident history and recovery requirements. Critical workloads and high-risk dependencies receive enhanced testing.
End-to-End Cloud Coverage
The audit considers the complete cloud service chain rather than reviewing the regulated entity or CSP in isolation. Applicable controls of the RE, CSP, MSP, SI and material subcontractors are assessed together with the interfaces and dependencies between them.
Accountability and Responsibility Validation
Codec Networks evaluates whether every activity and applicable regulatory clause has one clearly identified accountable party. Joint activities are broken into sub-tasks, and responsibility allocation is traced to the signed cloud agreements.
Control Design and Operating Effectiveness
The audit distinguishes between documented controls, implemented controls and controls that operated effectively during the audit period. Policies or CSP assurance reports alone are not treated as sufficient proof of compliance.
Testing may include:
- Document and contract review.
- Stakeholder interviews and walkthroughs.
- Cloud configuration and architecture review.
- Population-based sampling and evidence inspection.
- Log, ticket and incident-record analysis.
- Observation and reperformance of selected controls.
- Appropriately authorized technical testing and VAPT.
Cloud-Specific Security Validation
The assessment addresses cloud-native risks involving IAM, privileged access, MFA, multi-tenancy, APIs, management interfaces, encryption, key management, network segmentation, monitoring, SOC integration, vulnerability management, secure development, backup, recovery and breach notification.
Data Sovereignty and Regulatory Access
Codec Networks reviews actual data, log, backup and cryptographic-key paths to evaluate ownership, India localization, accessibility, retention, regulator visibility, forensic cooperation and secure expunging arrangements.
Resilience, Exit and Concentration Review
The audit examines BCP/DR readiness, restoration testing, RTO/RPO, provider shutdown contingencies, portability, interoperability, exit triggers and CSP concentration risks.
Evidence-Based and Action-Oriented Reporting
Findings are supported by objective evidence and evaluated according to regulatory impact, likelihood, business criticality and residual risk. Reports may include clause-wise status, risk-rated findings, responsibility mapping, remediation priorities, management responses and closure status.
Please Note
Codec Networks’ audit approach is intended to provide reasonable, point-in-time assurance within the mutually agreed scope, audit period and evidence made available. Responsibility for compliance, risk ownership, control operation and remediation remains with the SEBI-regulated entity and its management, consistent with Cloud Adoption Framework.
Codec Networks provides independent, risk-based and evidence-driven audit services to assess cloud governance, regulatory compliance, cybersecurity controls and operational resilience of SEBI-regulated entities. Each engagement is performed under an agreed scope, audit period, evidence protocol and Rules of Engagement, taking into account the entity’s SEBI category, cloud architecture, data sensitivity, system criticality and service-provider dependencies.
Audit Service Features
- Cloud governance and risk assessment: Review of the Board-approved cloud strategy, cloud risk-management approach, policies, accountable CISO or security resource, annual reviews, monitoring and exit preparedness.
- Cloud inventory and architecture validation: Assessment of cloud accounts, subscriptions, regions, applications, APIs, data stores, logs, backups, cryptographic services and material dependencies supporting regulated operations.
- CSP eligibility and due diligence: Verification of applicable MeitY empanelment, STQC or equivalent audit status, underlying infrastructure arrangements, PaaS/SaaS dependencies, financial and operational capability, personnel screening and periodic monitoring.
- Data ownership and localization: Evaluation of the regulated entity’s ownership and accessibility of data, logs and encryption keys; India-based storage and processing; regulatory visibility; retention; and secure expunging arrangements.
- Responsibility and contractual compliance: Verification that every cloud activity and applicable regulatory clause has an explicitly identified responsible party. Joint activities are examined at sub-task level, including responsibilities of CSPs, MSPs, system integrators and material subcontractors.
- Cloud security-control assessment: Review and testing of vulnerability and patch management, VAPT, IAM, privileged access, MFA, multi-tenancy, security monitoring, SOC integration, incident management, interfaces, network segmentation, encryption, endpoint protection, secure development, backup and recovery.
- Authorized technical assessment and VAPT: Risk-based configuration review and appropriately authorized vulnerability assessment or penetration testing of in-scope cloud infrastructure, applications, APIs and management interfaces. Testing is performed under approved targets, techniques, timelines and safety conditions.
- Audit rights and regulatory access review: Assessment of contractual provisions supporting audit, information access, supervisory review, search and seizure, forensic cooperation, provider audit reports and access to relevant subcontractor information.
- BCP, DR and cyber-resilience assessment: Evaluation of recovery arrangements, RTO/RPO, backup segregation, restoration testing, stakeholder-inclusive DR drills, cloud shutdown contingencies and unresolved resilience risks.
- Exit and concentration-risk review: Assessment of provider lock-in, portability, interoperability, concentration exposure, migration alternatives, exit triggers, termination assistance and permanent data deletion.
- Clause-wise reporting and remediation support: Delivery may include an executive report, detailed audit report, clause-wise compliance matrix, evidence index, risk-rated findings, responsibility matrix, management action plan and retest report.
CODEC NETWORKS VALUE PROPOSITION
Beyond protection, Codec Networks delivers value additions that strengthen compliance,
build digital trust, and empower business innovation.
RBI, SEBI, IRDAI, NPCI, UIDAI and Other Regulatory Audits
Codec Networks, a CERT-In empanelled Information Security Auditing Organisation, delivers independent, risk-based cybersecurity and compliance audits for regulated entities across banking, NBFC, FinTech, securities, insurance, payments, Aadhaar-enabled services, government, healthcare and critical infrastructure sectors.
Our value proposition combines regulatory understanding, cybersecurity expertise, structured audit methodology and evidence-driven assurance to help organizations identify compliance gaps, strengthen controls and demonstrate regulatory readiness.
1. Regulatory and Framework-Aligned Audit Assurance
- Audits applicable requirements issued by RBI, SEBI, IRDAI, NPCI, UIDAI, CERT-In and other relevant authorities.
- Maps regulatory obligations with ISO/IEC 27001:2022, ISO 27002, ISO 27005, ISO 22301, NIST CSF, COBIT, CIS Controls and applicable data-protection requirements.
- Converts complex regulatory provisions into practical audit criteria, control requirements, evidence expectations and accountable actions.
- Supports consistent compliance across applications, infrastructure, cloud, networks, data centres, branches, third parties and digital ecosystems.
2. CERT-In Empanelled and Risk-Based Audit Approach
- Applies a structured methodology aligned with applicable CERT-In requirements and recognized auditing principles.
- Evaluates both control design—Test of Design—and operating effectiveness—Test of Effectiveness.
- Prioritizes observations according to regulatory significance, threat exposure, business criticality, likelihood and potential impact.
- Maintains professional independence, confidentiality, evidence integrity and appropriate segregation between audit and remediation activities.
3. Multidisciplinary Regulatory and Cybersecurity Expertise
- Deploys auditors and specialists with experience in information security, IT governance, VAPT, cloud security, application security, SOC, incident response, privacy and business continuity.
- Brings relevant professional competencies such as CISA, CISSP, CISM, ISO 27001 Lead Auditor/Implementer, CEH and cloud-security certifications, subject to engagement requirements.
- Understands sector-specific technology, operating models, outsourcing arrangements, payment environments, digital channels and sensitive-data ecosystems.
- Integrates governance, process and technical testing to provide a complete view of regulatory cyber risk.
4. Comprehensive Audit Coverage
- Covers cybersecurity governance, IT risk management, asset management, identity and access management, secure configuration, vulnerability management and security monitoring.
- Reviews application, API, mobile, network, cloud, database, endpoint, data-protection and third-party security controls, as applicable.
- Assesses incident response, regulatory reporting, business continuity, disaster recovery, cyber resilience, log management and forensic readiness.
- Validates policies, procedures, contracts, configurations, records, system-generated evidence, samples and stakeholder practices.
5. Evidence-Driven Findings and Actionable Remediation
- Links each finding to the applicable regulatory clause, audit criterion, supporting evidence and affected system or process.
- Clearly distinguishes compliant, partially compliant, non-compliant and not-applicable requirements.
- Provides risk-rated observations with business impact, root-cause considerations, recommended corrective actions, ownership and target timelines.
- Supports structured management responses, corrective-action tracking and re-testing of remediated observations within the agreed scope.
6. Management Visibility and Regulatory Readiness
- Delivers executive summaries, detailed audit reports, compliance matrices, risk heat maps and prioritized remediation roadmaps.
- Provides traceability from regulatory requirements to controls, audit procedures, evidence reviewed and audit conclusions.
- Helps boards, senior management, CISOs, compliance officers and technology teams understand material exposures and required decisions.
- Strengthens readiness for regulatory inspections, supervisory reviews, internal audits, certification audits and customer assurance requirements.
7. Independent, Scalable and Business-Focused Delivery
- Adapts the audit approach to the organization’s size, complexity, risk profile, technology architecture and regulatory classification.
- Supports single-entity, multi-location, group-wide and ecosystem-based audits through onsite, remote or hybrid delivery models.
- Coordinates audit activities to reduce operational disruption while preserving audit independence and testing sufficiency.
- Enables organizations to transform regulatory compliance from a periodic exercise into a sustainable governance and cyber-resilience capability.
Why Customers Should Choose Codec Networks
Customers should consider Codec Networks for the combination of CERT-In empanelment, regulatory-domain understanding, multidisciplinary technical capability, risk-based testing and practical reporting. Our audits are designed not merely to identify documentary gaps, but to determine whether critical cybersecurity controls are appropriately designed, consistently implemented and demonstrably effective.
The result is greater regulatory confidence, stronger cyber resilience, improved management accountability and a clearly prioritized path toward sustained compliance.
Disclaimer: Audit scope, procedures and conclusions depend on the applicable regulation, agreed terms of reference, systems and locations included, sampling methodology, evidence provided and conditions existing during the audit period. An audit provides reasonable assurance within its defined scope and does not constitute a guarantee against cyber incidents, regulatory action or future control failure. CERT-In empanelment should be represented strictly in accordance with applicable CERT-In conditions and should not be construed as an endorsement of any commercial claim or as certification by CERT-In.
Founded in 2008 with 17+ Years of Industry Experience in Information and Cyber Security domain
Codec Networks Full-Spectrum Cybersecurity Expertise across all Industry Domains:
- Security Vulnerability Assessment & Penetration Testing (VAPT): Covering Web, Mobile, API, IoT, Blockchain, Cloud-Native, and smart infrastructure environments, with a focus on OWASP, MITRE ATT&CK, and real-world exploit simulation.
- Offensive Security & Deep Level Security Assessments: Advanced Red Team, Blue Team and Purple Team Exercises, Threat Simulations, Social Engineering Campaigns, and Secure Code Review.
- IT Security Audit & Compliance Services: Implementation and audit support for ISO/IEC 27001, ISO 27701, NIST CSF, RBI-CSF, SEBI, IRDAI, PCI DSS, HIPAA, SOC 2, GDPR, and India’s DPDPA 2023.
- Data Privacy & Strategic Risk Advisory: ISO 27701, GDPR, DPDPA, Cross-border compliance, DPIA, DPO-as-a-service, supply chain risk management, and digital transformation risk consulting.
- Emerging Technology Security (Web3.0 | AI | Blockchain): Specialized testing for smart contracts, DeFi platforms, Metaverse applications, AI/ML models, quantum readiness, and blockchain nodes.
- Managed SOC & Threat Monitoring Services: End-to-end SOC operations, SIEM/EDR/XDR/SOAR integration, threat intelligence, cloud security monitoring, and 24/7 incident response.
- Cyber Forensics & Threat Analysis: Investigation services including Device forensics, Malware Analysis, Cloud and Mobile forensics, insider threat detection, and Forensic support.
- Board-Level Cybersecurity Advisory Services to build governance, quantify risks, and align with enterprise-wide digital priorities : Codec Networks enables this transformation by offering Integrated Cyber Risk Management, GRC Program Advisory, Reputation Management, Crisis Communication Readiness, and CISO Support, tailored for CXOs and board members seeking to integrate cybersecurity into strategic decision-making.
- Cyber Security Education & Global Certifications - Through the Codec Centre for Professional Excellence, we deliver Post Graduate Certification in Advanced Cybersecurity (PGCAC), Graduate Certification in Advanced Cybersecurity (GCAC), Accredited Trainings & Certifications from EC Council, PECB, TUV, Quality Austria, ISACA and ISC2 - building the next generation of cybersecurity leaders.
- CERT-IN empaneled Information Security Auditing Organization
- NICSI empaneled for providing Application Audit and Compliance Services under Start-Up Category


- An ISO/IEC 27001:2022 certified company, has established Information Security Management System (ISMS), demonstrating a structured approach to manage and protect sensitive information from cyber threats.
- An ISO 20000 IT Service Management (ITSM) company, ensure high-quality and reliable service delivery to clients on our products and services offered.
- An ISO 9001 certified company, has established and maintains a certified Quality Management System (QMS) that meets international standards for quality and consistency
At Codec Networks, our foundation is built on deep technical mastery, certified expertise, and an unrelenting pursuit of cyber excellence. With a team of globally accredited professionals, advanced methodologies, and next-generation tools, we deliver measurable security outcomes across assessment, compliance, monitoring, and forensic domains. Our competency-driven approach ensures every engagement is governed by precision, accountability, and alignment with international standards — empowering enterprises to stay secure, compliant, and resilient.
Governance, Risk & Compliance (GRC) Competency
Codec Networks’ dedicated Governance, Risk & Compliance (GRC) group specializes in security assessments, risk management, regulatory compliance, and audit readiness. The team partners with organizations to strengthen governance frameworks and ensure end-to-end compliance in a complex regulatory landscape.
Key Attributes:
- Team of certified auditors and consultants with credentials including ISO 27001 LA/LI, ISO 31000 Risk Specialist, ISO 27701 PIMS, GDPR, SOC 2, HIPAA, CCPA, DPO, CISA, CISM, CRISC, CISSP and other advanced industry certifications.
- Expertise in enterprise risk quantification, privacy impact assessment (PIA/DPIA), audit automation, and supply chain risk mapping.
- Proven track record in implementing ISO-based ISMS/PIMS frameworks, RBI/SEBI/IRDAI audits, and cross-border data compliance projects.
Vulnerability Assessment & Penetration Testing (VAPT) Expertise
Our VAPT teams bring extensive technical depth across Web, Mobile, API, Cloud, Network, Database, Infrastructure, IoT, and People & Process domains. Every engagement is mapped to OWASP, NIST, MITRE ATT&CK, ISO 27001, PCI DSS, HIPAA, RBI, and GDPR frameworks — ensuring real-world relevance and compliance alignment.
Core Strengths:
- Certified professionals with CEH, C-PENT, LPT, OSCP, OSWE, OSEE, and CREST credentials, averaging 7–10 years of offensive security experience.
- Proven expertise in Red/Blue/Purple Teaming, DevSecOps, secure SDLC, and threat emulation.
- Continuous skill enhancement through CTFs, hackathons, and product certifications (on case to case basis) such as CCNA, CCNP etc.
Managed SOC & Threat Intelligence Operations
Codec Networks operates a 24/7 Managed Security Operations Center (SOC) delivering continuous visibility, detection, and response across hybrid environments. Our SOC integrates SIEM, SOAR, EDR/XDR, and Cloud-Native Analytics to ensure rapid threat detection, incident containment, and business continuity.
Key Capabilities:
- Certified SOC analysts with credentials such as CHFI, CEH, CompTIA CySA+, GCIA, GCFA, and Splunk Certified Architect.
- Integration with platforms like Splunk, QRadar, SentinelOne, CrowdStrike, Elastic, Microsoft Sentinel, and Cortex XSOAR.
- Advanced use cases include cloud posture management, insider threat analytics, MITRE ATT&CK–aligned detections, and threat hunting automation.
- Comprehensive SOC Maturity Assessments and Threat Intelligence Fusion through integration with global feeds and dark web monitoring.
Cyber Forensics & Threat Analysis Expertise
Our Cyber Forensic Division delivers end-to-end investigation, evidence preservation, and digital analysis services — designed to support law enforcement, corporate forensics, and internal response teams. We combine forensic science with cyber intelligence to identify root causes, trace adversaries, and restore operational integrity.
Core Expertise Areas:
- Device, Network, Cloud, and Mobile Forensics – leveraging latest forensic tools (wherever applicable) such as Autopsy, Cyber Triage, Kape, EnCase, FTK, Magnet AXIOM, and Cellebrite.
- Malware Reverse Engineering and Memory Forensics for incident containment and threat attribution.
- Blockchain & Crypto Forensics – tracing DeFi fraud, NFT manipulation, and crypto laundering activities using Chainalysis, TRM Labs, and Elliptic (wherever applicable).
- Incident Response Support – forensic readiness, eDiscovery, evidence preservation, aligned with ISO/IEC 27037 & 27043.
- Certified experts including CHFI, eCIR, eCDFP, GCFE, GCFA, EnCE, CFCE and ECIH, ensuring investigations meet both technical and legal standards.
Advanced Tools, Frameworks & Continuous Innovation
Codec Networks leverages industry-leading tools and platforms such as Burp Suite Pro, Nessus, Prisma Cloud, Splunk, QRadar, CrowdStrike, SentinelOne, Autopsy, Chainalysis, MythX, and Prowler (wherever applicable) ensuring accuracy, scalability, and efficiency.
Our methodologies align with globally recognized frameworks including:
- MITRE ATT&CK & D3FEND
- OWASP Top 10 / MASVS / ASVS
- NIST Cybersecurity Framework & SP 800-115
- ISO/IEC 27001, 27701, 31000, 22301
Through ongoing research, Codec Networks continually evolves to address modern threats — from Generative AI prompt attacks and smart contract exploits to IoT zero-days, metaverse impersonation, and quantum-era vulnerabilities.
Compliance-Driven Deliverables
All technical engagements and reports are mapped to major global and Indian compliance frameworks — including ISO 27001, PCI DSS, HIPAA, GDPR, RBI-CSF, SEBI, IRDAI, and DPDPA 2023. Our structured technical and executive reports support board-level visibility, audit evidence, and certification readiness, ensuring that every engagement drives both technical assurance and regulatory confidence.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience. Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
At Codec Networks, we believe that cybersecurity excellence is not achieved through tools alone — it is built through methodical delivery, risk-based insight, and measurable outcomes. Our Agile and Modular 8-Stage Delivery Methodology ensures that every engagement — from rapid risk assessments to full-scale ISMS implementations — is structured, standards-aligned, and business-focused.
Agile & Modular Methodology
Our delivery framework integrates global best practices with localized regulatory insight, ensuring each engagement is executed with clarity, accountability, and precision. Clients benefit from seamless onboarding, milestone-driven execution, and transparent reporting throughout the lifecycle.
- Discovery & Scoping: Collaborative workshops to understand business context, IT landscape, compliance obligations, and risk appetite, forming the foundation of a well-defined project scope.
- Risk Profiling & Gap Assessment: Comprehensive evaluation of people, process, and technology controls aligned with ISO 27001, NIST CSF, GDPR, HIPAA, DPDPA 2023, RBI, and PCI DSS.
- Regulatory Mapping & Framework Alignment: Mapping organizational obligations against applicable standards and laws — from ISO & NIST to RBI, SEBI, IRDAI, UIDAI, and DPDPA — including new-age frameworks like ISO 42001 (AI) and FATF for emerging technologies.
- Security Architecture & Control Design: Designing or refining network, cloud, and data security architectures with controls tailored for cloud, AI, OT/ICS, and Web3.0 environments.
- Documentation & Policy Development: Creation and refinement of Policies, SOPs, Risk Registers, DPIAs, Incident Response Plans, and Governance Documents, ensuring audit readiness and legal compliance.
- Implementation & Risk Treatment: Execution of remediation roadmaps, vendor risk management, privacy engineering, and workforce training to mitigate gaps and operationalize security controls.
- Validation, Testing & Audit Readiness: Conducting mock audits, VAPT, forensic readiness, and compliance testing to validate effectiveness and prepare for certifications.
- Governance Reporting & Continual Improvement: Delivering executive dashboards, compliance scorecards, and board-level insights with ongoing advisory through vCISO and DPO-as-a-Service models.
Risk-Based & Business-Oriented Audit Approach
Our methodology goes beyond testing systems — it focuses on how vulnerabilities translate into business, reputational, and compliance risks.
- Deliver Deep Insight: Actionable intelligence into vulnerabilities, attack paths, business impact, and remediation priorities.
- Extend Beyond Tools: Manual and contextual assessments combining automation with human expertise across government, financial, and commercial sectors.
- Actionable Reporting: Executive-friendly reports that translate complex findings into strategic, risk-aware recommendations.
- Efficient Execution: Critical assets prioritized for testing to deliver maximum value within tight engagement windows.
Outcome-Driven Engagements for Security Maturity
Each stage is modular yet interconnected, adaptable to enterprises of any scale or industry. Whether it’s a cloud-native fintech pursuing SOC 2, a healthcare provider ensuring HIPAA alignment, or a bank meeting RBI-CSF requirements, Codec Networks ensures consistency, compliance, and measurable improvement.
Beyond certification checklists, our Post-Audit Support and Continuous Risk Monitoring provide remediation guidance, breach response playbooks, staff training, and ongoing compliance tracking — building sustainable security posture and resilient business continuity.
Codec Networks – Turning Compliance into a Competitive Advantage. Structured. Measurable. Secure. Always Aligned with Your Business Goals.
At Codec Networks, our clients are not just audit subjects — they are long-term partners in a shared cybersecurity journey. Every engagement is designed around the client’s business priorities, security maturity, and risk appetite, ensuring solutions that are relevant, practical, and results-driven.
With a legacy of 650+ successful engagements across industries such as Banking, Fintech, Healthcare, Telecom, Energy, Aviation, Manufacturing, E-commerce, and Government, Codec Networks has attempted to become a trusted advisor for organizations seeking to transform compliance into resilience.
Our engagement philosophy extends beyond conventional audits. We integrate strategic advisory, technical assurance, remediation support, and continuous compliance monitoring, creating a full lifecycle relationship rather than a one-time service. Clients benefit from:
- Personalized advisory frameworks tailored to their business model and operational scale.
- Collaborative engagement models featuring joint workshops, stakeholder training, and compliance awareness sessions.
- Board-level guidance and reporting that translates complex technical findings into actionable business intelligence.
- Transparent communication channels with dedicated project managers, secure digital workspaces, and real-time status dashboards.
By combining the objectivity of an auditor with the empathy of an advisor, Codec Networks builds trust, accountability, and measurable security growth. Our commitment is simple — to deliver cybersecurity as a continuous partnership, not a periodic project.
Codec Networks – Where Advisory Meets Assurance. Empowering Clients Through Partnership, Transparency, and Trust.
At Codec Networks, integrity, professionalism, and ethical responsibility form the cornerstone of every engagement. As a trusted strategic partner in cybersecurity, we operate within the highest standards of ethical conduct, legal compliance, and regulatory governance, ensuring our services strengthen both our clients’ defenses and their reputations.
We adhere to a strict ethical code of conduct, driven by transparency, independence, and accountability. Every consultant, auditor, and engineer within Codec Networks upholds the core security triad of Confidentiality, Integrity, and Availability (CIA) — ensuring data protection, operational reliability, and business continuity at all times.
Our professional ethos blends technical excellence with moral responsibility, following structured processes, defined service standards, and adherence to international and national regulatory frameworks.
Our Ethical & Professional Commitments
- Zero-Compromise Consulting: We maintain independence, neutrality, and confidentiality across all audits and advisory engagements.
- Legal & Regulatory Conformance: We assist clients to conform strictly within the boundaries of applicable cyber laws, privacy regulations, and data protection statutes.
- Client-First Philosophy: Every recommendation is designed to safeguard stakeholder interests, minimize legal exposure, and build sustainable resilience.
- Outcome-Driven Security Maturity: Our modular yet integrated delivery approach supports organizations of all sizes in achieving measurable improvements in security posture.
- Global Delivery, Local Integrity: Our Global Network Delivery Model integrates international best practices with local regulatory expertise — ensuring value-driven, compliant outcomes.
Industry-Specific Security Advisory
Recognizing that every sector faces distinct threats and compliance challenges, Codec Networks provides customized, industry-aligned security advisory across BFSI, Fintech, Telecom, Healthcare, Energy, Aviation, E-commerce, Government, and Critical Infrastructure domains.
Our sector-specific consulting translates regulatory complexity into practical, business-aware strategies, ensuring risk mitigation plans are compliant, auditable, and operationally feasible.
Our Commitment
With a zero-tolerance approach to ethical compromise, Codec Networks stands for trust, transparency, and truth in cybersecurity. We are more than consultants — we are custodians of digital integrity, committed to helping organizations navigate risk, maintain compliance, and enable secure business growth.
Codec Networks – Where Integrity Meets Innovation. Trusted. Ethical. Future-Ready.
At Codec Networks, we combine the strength of a global delivery ecosystem with the precision of local regulatory insight to deliver cybersecurity solutions that are both internationally benchmarked and regionally compliant.
Our Global Delivery Capability enables clients across continents to access specialized cybersecurity expertise, advanced technologies, and globally aligned methodologies. Through a distributed network of certified professionals, partner alliances, and intelligence centers, Codec Networks ensures consistent service quality and rapid response across time zones and geographies.
What truly differentiates us is our Local Expertise — a deep understanding of national regulations, industry frameworks, and operational nuances that shape cybersecurity implementation in each region.
Our hybrid delivery model blends remote and on-site collaboration, combining the agility of digital operations with the contextual understanding of local consultants. This ensures culturally aligned communication, faster problem resolution, and seamless coordination with client teams.
With a presence across India, Codec Networks empowers global enterprises to manage cybersecurity uniformly while adapting to local risks, regulations, and realities.
Codec Networks – Global Vision. Local Precision. Consistent Cyber Resilience.
“With Codec Networks, you’re not just buying a service — you’re investing in a cybersecurity ally who understands your business, defends your reputation, and strengthens your future.”
At Codec Networks, we believe cybersecurity is not a project — it’s a partnership. Our approach is built on trust, transparency, and transformation, helping clients evolve from compliance readiness to cyber resilience.
Your Strategic Security Partner
Codec Networks acts as a strategic security partner, providing continuous roadmap development, architecture reviews, and improvement programs that evolve with your business and the threat landscape.
“We don’t just secure businesses — we empower them to lead with confidence in a digital-first world.”
Our strength lies in the fusion of technical depth, regulatory insight, industry specialization, and future readiness — providing unmatched cybersecurity value to enterprises across India and beyond.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience. Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Every engagement reflects our belief that advisory must meet assurance — a promise we deliver through partnership, integrity, and measurable impact.
Codec Networks – Where Advisory Meets Assurance. Empowering Clients Through Partnership, Transparency, and Trust.
And above all —
“Decoding Threats. Coding Solutions.” That’s the Codec Networks Advantage.
RBI, SEBI, IRDAI, NPCI, UIDAI and Other Regulatory Audits
Codec Networks, a CERT-In empanelled Information Security Auditing Organisation, delivers independent, risk-based cybersecurity and compliance audits for regulated entities across banking, NBFC, FinTech, securities, insurance, payments, Aadhaar-enabled services, government, healthcare and critical infrastructure sectors.
Our value proposition combines regulatory understanding, cybersecurity expertise, structured audit methodology and evidence-driven assurance to help organizations identify compliance gaps, strengthen controls and demonstrate regulatory readiness.
1. Regulatory and Framework-Aligned Audit Assurance
- Audits applicable requirements issued by RBI, SEBI, IRDAI, NPCI, UIDAI, CERT-In and other relevant authorities.
- Maps regulatory obligations with ISO/IEC 27001:2022, ISO 27002, ISO 27005, ISO 22301, NIST CSF, COBIT, CIS Controls and applicable data-protection requirements.
- Converts complex regulatory provisions into practical audit criteria, control requirements, evidence expectations and accountable actions.
- Supports consistent compliance across applications, infrastructure, cloud, networks, data centres, branches, third parties and digital ecosystems.
2. CERT-In Empanelled and Risk-Based Audit Approach
- Applies a structured methodology aligned with applicable CERT-In requirements and recognized auditing principles.
- Evaluates both control design—Test of Design—and operating effectiveness—Test of Effectiveness.
- Prioritizes observations according to regulatory significance, threat exposure, business criticality, likelihood and potential impact.
- Maintains professional independence, confidentiality, evidence integrity and appropriate segregation between audit and remediation activities.
3. Multidisciplinary Regulatory and Cybersecurity Expertise
- Deploys auditors and specialists with experience in information security, IT governance, VAPT, cloud security, application security, SOC, incident response, privacy and business continuity.
- Brings relevant professional competencies such as CISA, CISSP, CISM, ISO 27001 Lead Auditor/Implementer, CEH and cloud-security certifications, subject to engagement requirements.
- Understands sector-specific technology, operating models, outsourcing arrangements, payment environments, digital channels and sensitive-data ecosystems.
- Integrates governance, process and technical testing to provide a complete view of regulatory cyber risk.
4. Comprehensive Audit Coverage
- Covers cybersecurity governance, IT risk management, asset management, identity and access management, secure configuration, vulnerability management and security monitoring.
- Reviews application, API, mobile, network, cloud, database, endpoint, data-protection and third-party security controls, as applicable.
- Assesses incident response, regulatory reporting, business continuity, disaster recovery, cyber resilience, log management and forensic readiness.
- Validates policies, procedures, contracts, configurations, records, system-generated evidence, samples and stakeholder practices.
5. Evidence-Driven Findings and Actionable Remediation
- Links each finding to the applicable regulatory clause, audit criterion, supporting evidence and affected system or process.
- Clearly distinguishes compliant, partially compliant, non-compliant and not-applicable requirements.
- Provides risk-rated observations with business impact, root-cause considerations, recommended corrective actions, ownership and target timelines.
- Supports structured management responses, corrective-action tracking and re-testing of remediated observations within the agreed scope.
6. Management Visibility and Regulatory Readiness
- Delivers executive summaries, detailed audit reports, compliance matrices, risk heat maps and prioritized remediation roadmaps.
- Provides traceability from regulatory requirements to controls, audit procedures, evidence reviewed and audit conclusions.
- Helps boards, senior management, CISOs, compliance officers and technology teams understand material exposures and required decisions.
- Strengthens readiness for regulatory inspections, supervisory reviews, internal audits, certification audits and customer assurance requirements.
7. Independent, Scalable and Business-Focused Delivery
- Adapts the audit approach to the organization’s size, complexity, risk profile, technology architecture and regulatory classification.
- Supports single-entity, multi-location, group-wide and ecosystem-based audits through onsite, remote or hybrid delivery models.
- Coordinates audit activities to reduce operational disruption while preserving audit independence and testing sufficiency.
- Enables organizations to transform regulatory compliance from a periodic exercise into a sustainable governance and cyber-resilience capability.
Why Customers Should Choose Codec Networks
Customers should consider Codec Networks for the combination of CERT-In empanelment, regulatory-domain understanding, multidisciplinary technical capability, risk-based testing and practical reporting. Our audits are designed not merely to identify documentary gaps, but to determine whether critical cybersecurity controls are appropriately designed, consistently implemented and demonstrably effective.
The result is greater regulatory confidence, stronger cyber resilience, improved management accountability and a clearly prioritized path toward sustained compliance.
Disclaimer: Audit scope, procedures and conclusions depend on the applicable regulation, agreed terms of reference, systems and locations included, sampling methodology, evidence provided and conditions existing during the audit period. An audit provides reasonable assurance within its defined scope and does not constitute a guarantee against cyber incidents, regulatory action or future control failure. CERT-In empanelment should be represented strictly in accordance with applicable CERT-In conditions and should not be construed as an endorsement of any commercial claim or as certification by CERT-In.
Founded in 2008 with 17+ Years of Industry Experience in Information and Cyber Security domain
Codec Networks Full-Spectrum Cybersecurity Expertise across all Industry Domains:
- Security Vulnerability Assessment & Penetration Testing (VAPT): Covering Web, Mobile, API, IoT, Blockchain, Cloud-Native, and smart infrastructure environments, with a focus on OWASP, MITRE ATT&CK, and real-world exploit simulation.
- Offensive Security & Deep Level Security Assessments: Advanced Red Team, Blue Team and Purple Team Exercises, Threat Simulations, Social Engineering Campaigns, and Secure Code Review.
- IT Security Audit & Compliance Services: Implementation and audit support for ISO/IEC 27001, ISO 27701, NIST CSF, RBI-CSF, SEBI, IRDAI, PCI DSS, HIPAA, SOC 2, GDPR, and India’s DPDPA 2023.
- Data Privacy & Strategic Risk Advisory: ISO 27701, GDPR, DPDPA, Cross-border compliance, DPIA, DPO-as-a-service, supply chain risk management, and digital transformation risk consulting.
- Emerging Technology Security (Web3.0 | AI | Blockchain): Specialized testing for smart contracts, DeFi platforms, Metaverse applications, AI/ML models, quantum readiness, and blockchain nodes.
- Managed SOC & Threat Monitoring Services: End-to-end SOC operations, SIEM/EDR/XDR/SOAR integration, threat intelligence, cloud security monitoring, and 24/7 incident response.
- Cyber Forensics & Threat Analysis: Investigation services including Device forensics, Malware Analysis, Cloud and Mobile forensics, insider threat detection, and Forensic support.
- Board-Level Cybersecurity Advisory Services to build governance, quantify risks, and align with enterprise-wide digital priorities : Codec Networks enables this transformation by offering Integrated Cyber Risk Management, GRC Program Advisory, Reputation Management, Crisis Communication Readiness, and CISO Support, tailored for CXOs and board members seeking to integrate cybersecurity into strategic decision-making.
- Cyber Security Education & Global Certifications - Through the Codec Centre for Professional Excellence, we deliver Post Graduate Certification in Advanced Cybersecurity (PGCAC), Graduate Certification in Advanced Cybersecurity (GCAC), Accredited Trainings & Certifications from EC Council, PECB, TUV, Quality Austria, ISACA and ISC2 - building the next generation of cybersecurity leaders.
- CERT-IN empaneled Information Security Auditing Organization
- NICSI empaneled for providing Application Audit and Compliance Services under Start-Up Category
- An ISO/IEC 27001:2022 certified company, has established Information Security Management System (ISMS), demonstrating a structured approach to manage and protect sensitive information from cyber threats.
- An ISO 20000 IT Service Management (ITSM) company, ensure high-quality and reliable service delivery to clients on our products and services offered.
- An ISO 9001 certified company, has established and maintains a certified Quality Management System (QMS) that meets international standards for quality and consistency
At Codec Networks, our foundation is built on deep technical mastery, certified expertise, and an unrelenting pursuit of cyber excellence. With a team of globally accredited professionals, advanced methodologies, and next-generation tools, we deliver measurable security outcomes across assessment, compliance, monitoring, and forensic domains. Our competency-driven approach ensures every engagement is governed by precision, accountability, and alignment with international standards — empowering enterprises to stay secure, compliant, and resilient.
Governance, Risk & Compliance (GRC) Competency
Codec Networks’ dedicated Governance, Risk & Compliance (GRC) group specializes in security assessments, risk management, regulatory compliance, and audit readiness. The team partners with organizations to strengthen governance frameworks and ensure end-to-end compliance in a complex regulatory landscape.
Key Attributes:
- Team of certified auditors and consultants with credentials including ISO 27001 LA/LI, ISO 31000 Risk Specialist, ISO 27701 PIMS, GDPR, SOC 2, HIPAA, CCPA, DPO, CISA, CISM, CRISC, CISSP and other advanced industry certifications.
- Expertise in enterprise risk quantification, privacy impact assessment (PIA/DPIA), audit automation, and supply chain risk mapping.
- Proven track record in implementing ISO-based ISMS/PIMS frameworks, RBI/SEBI/IRDAI audits, and cross-border data compliance projects.
Vulnerability Assessment & Penetration Testing (VAPT) Expertise
Our VAPT teams bring extensive technical depth across Web, Mobile, API, Cloud, Network, Database, Infrastructure, IoT, and People & Process domains. Every engagement is mapped to OWASP, NIST, MITRE ATT&CK, ISO 27001, PCI DSS, HIPAA, RBI, and GDPR frameworks — ensuring real-world relevance and compliance alignment.
Core Strengths:
- Certified professionals with CEH, C-PENT, LPT, OSCP, OSWE, OSEE, and CREST credentials, averaging 7–10 years of offensive security experience.
- Proven expertise in Red/Blue/Purple Teaming, DevSecOps, secure SDLC, and threat emulation.
- Continuous skill enhancement through CTFs, hackathons, and product certifications (on case to case basis) such as CCNA, CCNP etc.
Managed SOC & Threat Intelligence Operations
Codec Networks operates a 24/7 Managed Security Operations Center (SOC) delivering continuous visibility, detection, and response across hybrid environments. Our SOC integrates SIEM, SOAR, EDR/XDR, and Cloud-Native Analytics to ensure rapid threat detection, incident containment, and business continuity.
Key Capabilities:
- Certified SOC analysts with credentials such as CHFI, CEH, CompTIA CySA+, GCIA, GCFA, and Splunk Certified Architect.
- Integration with platforms like Splunk, QRadar, SentinelOne, CrowdStrike, Elastic, Microsoft Sentinel, and Cortex XSOAR.
- Advanced use cases include cloud posture management, insider threat analytics, MITRE ATT&CK–aligned detections, and threat hunting automation.
- Comprehensive SOC Maturity Assessments and Threat Intelligence Fusion through integration with global feeds and dark web monitoring.
Cyber Forensics & Threat Analysis Expertise
Our Cyber Forensic Division delivers end-to-end investigation, evidence preservation, and digital analysis services — designed to support law enforcement, corporate forensics, and internal response teams. We combine forensic science with cyber intelligence to identify root causes, trace adversaries, and restore operational integrity.
Core Expertise Areas:
- Device, Network, Cloud, and Mobile Forensics – leveraging latest forensic tools (wherever applicable) such as Autopsy, Cyber Triage, Kape, EnCase, FTK, Magnet AXIOM, and Cellebrite.
- Malware Reverse Engineering and Memory Forensics for incident containment and threat attribution.
- Blockchain & Crypto Forensics – tracing DeFi fraud, NFT manipulation, and crypto laundering activities using Chainalysis, TRM Labs, and Elliptic (wherever applicable).
- Incident Response Support – forensic readiness, eDiscovery, evidence preservation, aligned with ISO/IEC 27037 & 27043.
- Certified experts including CHFI, eCIR, eCDFP, GCFE, GCFA, EnCE, CFCE and ECIH, ensuring investigations meet both technical and legal standards.
Advanced Tools, Frameworks & Continuous Innovation
Codec Networks leverages industry-leading tools and platforms such as Burp Suite Pro, Nessus, Prisma Cloud, Splunk, QRadar, CrowdStrike, SentinelOne, Autopsy, Chainalysis, MythX, and Prowler (wherever applicable) ensuring accuracy, scalability, and efficiency.
Our methodologies align with globally recognized frameworks including:
- MITRE ATT&CK & D3FEND
- OWASP Top 10 / MASVS / ASVS
- NIST Cybersecurity Framework & SP 800-115
- ISO/IEC 27001, 27701, 31000, 22301
Through ongoing research, Codec Networks continually evolves to address modern threats — from Generative AI prompt attacks and smart contract exploits to IoT zero-days, metaverse impersonation, and quantum-era vulnerabilities.
Compliance-Driven Deliverables
All technical engagements and reports are mapped to major global and Indian compliance frameworks — including ISO 27001, PCI DSS, HIPAA, GDPR, RBI-CSF, SEBI, IRDAI, and DPDPA 2023. Our structured technical and executive reports support board-level visibility, audit evidence, and certification readiness, ensuring that every engagement drives both technical assurance and regulatory confidence.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience. Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
At Codec Networks, we believe that cybersecurity excellence is not achieved through tools alone — it is built through methodical delivery, risk-based insight, and measurable outcomes. Our Agile and Modular 8-Stage Delivery Methodology ensures that every engagement — from rapid risk assessments to full-scale ISMS implementations — is structured, standards-aligned, and business-focused.
Agile & Modular Methodology
Our delivery framework integrates global best practices with localized regulatory insight, ensuring each engagement is executed with clarity, accountability, and precision. Clients benefit from seamless onboarding, milestone-driven execution, and transparent reporting throughout the lifecycle.
- Discovery & Scoping: Collaborative workshops to understand business context, IT landscape, compliance obligations, and risk appetite, forming the foundation of a well-defined project scope.
- Risk Profiling & Gap Assessment: Comprehensive evaluation of people, process, and technology controls aligned with ISO 27001, NIST CSF, GDPR, HIPAA, DPDPA 2023, RBI, and PCI DSS.
- Regulatory Mapping & Framework Alignment: Mapping organizational obligations against applicable standards and laws — from ISO & NIST to RBI, SEBI, IRDAI, UIDAI, and DPDPA — including new-age frameworks like ISO 42001 (AI) and FATF for emerging technologies.
- Security Architecture & Control Design: Designing or refining network, cloud, and data security architectures with controls tailored for cloud, AI, OT/ICS, and Web3.0 environments.
- Documentation & Policy Development: Creation and refinement of Policies, SOPs, Risk Registers, DPIAs, Incident Response Plans, and Governance Documents, ensuring audit readiness and legal compliance.
- Implementation & Risk Treatment: Execution of remediation roadmaps, vendor risk management, privacy engineering, and workforce training to mitigate gaps and operationalize security controls.
- Validation, Testing & Audit Readiness: Conducting mock audits, VAPT, forensic readiness, and compliance testing to validate effectiveness and prepare for certifications.
- Governance Reporting & Continual Improvement: Delivering executive dashboards, compliance scorecards, and board-level insights with ongoing advisory through vCISO and DPO-as-a-Service models.
Risk-Based & Business-Oriented Audit Approach
Our methodology goes beyond testing systems — it focuses on how vulnerabilities translate into business, reputational, and compliance risks.
- Deliver Deep Insight: Actionable intelligence into vulnerabilities, attack paths, business impact, and remediation priorities.
- Extend Beyond Tools: Manual and contextual assessments combining automation with human expertise across government, financial, and commercial sectors.
- Actionable Reporting: Executive-friendly reports that translate complex findings into strategic, risk-aware recommendations.
- Efficient Execution: Critical assets prioritized for testing to deliver maximum value within tight engagement windows.
Outcome-Driven Engagements for Security Maturity
Each stage is modular yet interconnected, adaptable to enterprises of any scale or industry. Whether it’s a cloud-native fintech pursuing SOC 2, a healthcare provider ensuring HIPAA alignment, or a bank meeting RBI-CSF requirements, Codec Networks ensures consistency, compliance, and measurable improvement.
Beyond certification checklists, our Post-Audit Support and Continuous Risk Monitoring provide remediation guidance, breach response playbooks, staff training, and ongoing compliance tracking — building sustainable security posture and resilient business continuity.
Codec Networks – Turning Compliance into a Competitive Advantage. Structured. Measurable. Secure. Always Aligned with Your Business Goals.
At Codec Networks, our clients are not just audit subjects — they are long-term partners in a shared cybersecurity journey. Every engagement is designed around the client’s business priorities, security maturity, and risk appetite, ensuring solutions that are relevant, practical, and results-driven.
With a legacy of 650+ successful engagements across industries such as Banking, Fintech, Healthcare, Telecom, Energy, Aviation, Manufacturing, E-commerce, and Government, Codec Networks has attempted to become a trusted advisor for organizations seeking to transform compliance into resilience.
Our engagement philosophy extends beyond conventional audits. We integrate strategic advisory, technical assurance, remediation support, and continuous compliance monitoring, creating a full lifecycle relationship rather than a one-time service. Clients benefit from:
- Personalized advisory frameworks tailored to their business model and operational scale.
- Collaborative engagement models featuring joint workshops, stakeholder training, and compliance awareness sessions.
- Board-level guidance and reporting that translates complex technical findings into actionable business intelligence.
- Transparent communication channels with dedicated project managers, secure digital workspaces, and real-time status dashboards.
By combining the objectivity of an auditor with the empathy of an advisor, Codec Networks builds trust, accountability, and measurable security growth. Our commitment is simple — to deliver cybersecurity as a continuous partnership, not a periodic project.
Codec Networks – Where Advisory Meets Assurance. Empowering Clients Through Partnership, Transparency, and Trust.
At Codec Networks, integrity, professionalism, and ethical responsibility form the cornerstone of every engagement. As a trusted strategic partner in cybersecurity, we operate within the highest standards of ethical conduct, legal compliance, and regulatory governance, ensuring our services strengthen both our clients’ defenses and their reputations.
We adhere to a strict ethical code of conduct, driven by transparency, independence, and accountability. Every consultant, auditor, and engineer within Codec Networks upholds the core security triad of Confidentiality, Integrity, and Availability (CIA) — ensuring data protection, operational reliability, and business continuity at all times.
Our professional ethos blends technical excellence with moral responsibility, following structured processes, defined service standards, and adherence to international and national regulatory frameworks.
Our Ethical & Professional Commitments
- Zero-Compromise Consulting: We maintain independence, neutrality, and confidentiality across all audits and advisory engagements.
- Legal & Regulatory Conformance: We assist clients to conform strictly within the boundaries of applicable cyber laws, privacy regulations, and data protection statutes.
- Client-First Philosophy: Every recommendation is designed to safeguard stakeholder interests, minimize legal exposure, and build sustainable resilience.
- Outcome-Driven Security Maturity: Our modular yet integrated delivery approach supports organizations of all sizes in achieving measurable improvements in security posture.
- Global Delivery, Local Integrity: Our Global Network Delivery Model integrates international best practices with local regulatory expertise — ensuring value-driven, compliant outcomes.
Industry-Specific Security Advisory
Recognizing that every sector faces distinct threats and compliance challenges, Codec Networks provides customized, industry-aligned security advisory across BFSI, Fintech, Telecom, Healthcare, Energy, Aviation, E-commerce, Government, and Critical Infrastructure domains.
Our sector-specific consulting translates regulatory complexity into practical, business-aware strategies, ensuring risk mitigation plans are compliant, auditable, and operationally feasible.
Our Commitment
With a zero-tolerance approach to ethical compromise, Codec Networks stands for trust, transparency, and truth in cybersecurity. We are more than consultants — we are custodians of digital integrity, committed to helping organizations navigate risk, maintain compliance, and enable secure business growth.
Codec Networks – Where Integrity Meets Innovation. Trusted. Ethical. Future-Ready.
At Codec Networks, we combine the strength of a global delivery ecosystem with the precision of local regulatory insight to deliver cybersecurity solutions that are both internationally benchmarked and regionally compliant.
Our Global Delivery Capability enables clients across continents to access specialized cybersecurity expertise, advanced technologies, and globally aligned methodologies. Through a distributed network of certified professionals, partner alliances, and intelligence centers, Codec Networks ensures consistent service quality and rapid response across time zones and geographies.
What truly differentiates us is our Local Expertise — a deep understanding of national regulations, industry frameworks, and operational nuances that shape cybersecurity implementation in each region.
Our hybrid delivery model blends remote and on-site collaboration, combining the agility of digital operations with the contextual understanding of local consultants. This ensures culturally aligned communication, faster problem resolution, and seamless coordination with client teams.
With a presence across India, Codec Networks empowers global enterprises to manage cybersecurity uniformly while adapting to local risks, regulations, and realities.
Codec Networks – Global Vision. Local Precision. Consistent Cyber Resilience.
“With Codec Networks, you’re not just buying a service — you’re investing in a cybersecurity ally who understands your business, defends your reputation, and strengthens your future.”
At Codec Networks, we believe cybersecurity is not a project — it’s a partnership. Our approach is built on trust, transparency, and transformation, helping clients evolve from compliance readiness to cyber resilience.
Your Strategic Security Partner
Codec Networks acts as a strategic security partner, providing continuous roadmap development, architecture reviews, and improvement programs that evolve with your business and the threat landscape.
“We don’t just secure businesses — we empower them to lead with confidence in a digital-first world.”
Our strength lies in the fusion of technical depth, regulatory insight, industry specialization, and future readiness — providing unmatched cybersecurity value to enterprises across India and beyond.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience. Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Every engagement reflects our belief that advisory must meet assurance — a promise we deliver through partnership, integrity, and measurable impact.
Codec Networks – Where Advisory Meets Assurance. Empowering Clients Through Partnership, Transparency, and Trust.
And above all —
“Decoding Threats. Coding Solutions.” That’s the Codec Networks Advantage.
WHAT OUR CUSTOMERS SAY
Every customer testimonial is proof of our commitment, highlighting security,
compliance, and resilience enabled by Codec Networks’ services.
-
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean”
Vijay Pratap
Developer -
“Deepak Baghel is a passionate Frontend Developer specializing in building responsive, accessible interfaces. He enjoys solving complex problems with clean”
Deepak Baghel
Frontend Developer -
“Saurav is a passionate DevOps engineer specializing in building resilient, automated delivery pipelines. He enjoys solving complex problems with clean”
Saurav
DevOps
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean”
Vijay Pratap
Developer
“Deepak Baghel is a passionate Frontend Developer specializing in building responsive, accessible interfaces. He enjoys solving complex problems with clean”
Deepak Baghel
Frontend Developer
“Saurav is a passionate DevOps engineer specializing in building resilient, automated delivery pipelines. He enjoys solving complex problems with clean”
Saurav
DevOpsFREQUENTLY ASKED QUESTION
Asking the right questions is the first step toward security; our FAQs
It is an independent assessment of whether a SEBI-regulated entity’s cloud governance, provider arrangements, security controls, data practices, resilience and reporting align with SEBI’s Cloud Adoption Framework.
The framework applies to specified SEBI-regulated entities, including Stock Exchanges, Clearing Corporations, Depositories, Stock Brokers, Depository Participants, AMCs/Mutual Funds, qualified RTAs and KYC Registration Agencies. Applicability should be confirmed according to the entity’s registration, operations and current SEBI directions.
Public and community cloud deployments are covered. Hybrid cloud is covered to the extent it incorporates public or community cloud components; its private-cloud components may remain subject to other applicable SEBI cybersecurity, systems-audit, outsourcing and BCP/DR requirements.
Yes. SaaS and PaaS services used for regulated activities should be assessed along with their underlying cloud infrastructure, data locations, security responsibilities and material subcontractors. Applicable MeitY empanelment, STQC or equivalent assurance and back-to-back contractual requirements should also be examined.
No. The regulated entity remains ultimately accountable for availability, security, data protection and regulatory compliance. Responsibilities may be allocated contractually, but accountability cannot be completely transferred to the CSP, MSP, SI or subcontractor.
The scope may include cloud governance, risk management, inventory, CSP due diligence, data ownership and localization, IAM, encryption, logging, vulnerability management, SOC integration, contracts, incident response, BCP/DR, concentration risk and exit arrangements. The final scope is agreed for each engagement.
Codec Networks considers the entity’s SEBI category, regulated services, cloud accounts, critical workloads, data flows, locations, interfaces and provider dependencies. Systems connected to or capable of affecting regulated operations may also be included.
VAPT may be included where required by the applicable SEBI criteria and agreed scope. Testing is performed only against expressly authorized targets, during approved windows and under documented Rules of Engagement and safety conditions.
Evidence may include policies, Board records, cloud inventories, architecture and data-flow diagrams, contracts, responsibility matrices, CSP assurance reports, configurations, IAM records, logs, vulnerability reports, incident records, backup tests and DR results. Evidence requirements are customized to the environment.
No. MeitY empanelment, STQC reports, ISO certifications, SOC reports and other provider assurance may support the audit, but they do not replace assessment of the regulated entity’s own configurations, responsibilities, contracts, monitoring and operating controls.
Deliverables may include an executive summary, detailed audit report, clause-wise compliance matrix, risk-rated findings, evidence index, responsibility mapping, management action plan and retest or closure report. Final deliverables depend on the engagement scope and applicable reporting mechanism.
Findings are evaluated using regulatory impact, business criticality, likelihood, exploitability, control effectiveness and residual risk. Reports distinguish non-compliance, partial compliance, limitations and advisory improvement opportunities.
Yes. The audit assesses whether responsibilities are explicitly allocated among the RE, CSP, MSP, SI and material subcontractors. Joint activities should be divided into identifiable sub-tasks and incorporated into signed agreements.
Management provides corrective actions, accountable owners and target dates. Closure is confirmed after relevant evidence is reviewed and, where necessary, the affected control or vulnerability is retested; management risk acceptance does not override a mandatory regulatory requirement.
No. The audit provides reasonable, point-in-time assurance for the agreed scope, period and evidence available.