

Resources Categories
INDUSTRY FACT FILE · AGRICULTURE & AGRITECH
Applicable Cybersecurity Services and Codec Networks Bundles for Agritech
How Codec Networks services and bundled service models help agriculture and agritech businesses resolve their threats and meet lender, buyer, scheme, CERT-In, DPDP and investor expectations.
|
In this document 1. Our approach 2. Mapping threats to services 3. Codec Networks service catalogue for the sector 4. Codec Networks bundles for the sector 5. Sector programmes built from the bundles 6. Packages: Foundation, Assurance and Continuous Resilience 7. Regulatory requirement-to-bundle mapping 8. Threat-to-bundle coverage matrix 9. Delivery methodology and deliverables 10. Why Codec Networks 11. Annex: indicative commercial ranges |
1. Our approach
Agriculture and agritech businesses need security that keeps the season running and stands up to lenders, buyers and regulators. Codec Networks works on four principles:
- Follow the farmer's data and money: every engagement traces how a farmer's identity, land and crop data and payments move from field devices, agents and apps through APIs, partners and cloud platforms to payouts, loans and receipts.
- Test safely and in season: devices, controllers, drones and payment flows are tested only with authorisation, in agreed windows and controlled conditions, so that irrigation, spraying, procurement and payouts are never put at risk.
- Watch the field, the platform and the payments together: device, cloud, API, identity and payment monitoring sit in one SOC, with heightened watch during sowing, harvest and payout windows.
- Prove it: findings mapped to the Digital Agriculture Mission and integration terms, RBI's lending rules, the WDRA framework, CERT-In's Directions and audit guidelines, input laws, the DPDP Act and lender and buyer contracts.
2. Mapping threats to services
The table maps the 18 threats identified in Document 4 of this set to the Codec Networks services that help mitigate them.
|
Threat / challenge |
Applicable Codec Networks services |
Intended outcome |
|
Farm IoT device and gateway compromise |
IoT device, firmware and gateway testing, broker review, exposure scanning |
Devices only the right systems can reach |
|
Machinery telematics and agri-drone platform abuse |
Telematics and drone fleet platform and API review, account security |
Fleets controlled only by their owners |
|
Marketplace and trading platform API flaws |
Marketplace and trading API VAPT with object-level authorisation tests |
Each user sees and changes only their own trades |
|
Payment integration and settlement fraud |
Payment integration testing, callback verification, settlement logic review |
No payout without verified payment |
|
Farmer, trader and dealer account takeover |
Account security testing, MFA and OTP flow review, fraud monitoring |
Accounts that resist takeover |
|
Farmer data exposure and consent failures |
DPDP gap assessment, data mapping, consent and notice review |
Farmer data collected and used lawfully |
|
Misuse of public platform and scheme credentials |
Integration and privileged access review, API key handling, change monitoring |
Platform access that is named and watched |
|
Agri-loan, subsidy and warehouse receipt fraud |
Loan and receipt workflow review, source data checks, fraud controls |
Fraud caught before money moves |
|
Warehouse, cold store and processing OT tampering |
Warehouse, cold store and plant OT assessment, segmentation |
Storage and plants that keep running |
|
Ransomware timed to sowing and harvest seasons |
Ransomware readiness review, EDR and backup testing, IR retainer |
Fast recovery in peak season |
|
Cloud misconfiguration and exposed data stores |
Cloud configuration and storage exposure assessment |
Cloud platforms configured securely |
|
Counterfeit input codes and dealer portal fraud |
Dealer portal VAPT, QR code and traceability system review |
Codes and incentives that cannot be forged |
|
Theft of breeding data, trait IP and R&D |
Data loss prevention review, repository and access controls, leaver process |
Breeding and trial data that stay home |
|
Phishing and payment diversion in commodity trade |
Email security review, payment change verification, awareness |
Payments that reach the right account |
|
Field agent mobile app and device risks |
Mobile app testing, device management, MFA and device binding review |
Agent devices that cannot be misused |
|
AI advisory, analytics and model data risks |
AI and analytics risk review, data handling and abuse testing |
Advisory tools that are safe and private |
|
Vendor, integrator and SaaS supplier risk |
Vendor and integrator assessments, contract security clauses |
Suppliers that meet your standard |
|
Weak logs, monitoring and 6-hour reporting |
Log architecture review, managed SOC, IR retainer |
Provable timelines, on-time reporting |
3. Codec Networks service catalogue for the sector
|
Service line |
Sector-relevant services |
|
Security Vulnerability Assessment & Penetration Testing |
Farm sensors, gateways and controllers, drone and telematics platforms, warehouse and plant networks, external attack surface, red teaming of platform and payment paths |
|
Farm IoT & drone security |
Device and firmware testing, update and signing reviews, message broker and topic access reviews, drone ground control and fleet platform reviews, safe test planning |
|
Application, API & payment security |
Marketplaces, farmer, dealer and agent apps, trading and lender APIs, payment callbacks and settlement logic, AgriStack and partner integrations, DevSecOps pipelines |
|
Cloud, identity & zero trust |
Cloud configuration and storage exposure, identity and privileged access, API key and secret handling, field agent access, MFA and device binding |
|
OT security for warehouses and plants |
Weighbridges, dryers, cold rooms, sensors and cameras, processing lines and remote access, aligned with IEC 62443 |
|
Supply chain & third-party risk |
Device makers, cloud and SaaS vendors, integrators, service centres, dealers and lending partners, contract security clauses |
|
Information security audit & compliance |
CERT-In empanelled audits, CERT-In risk-based audits including OT, support for lender, insurer and buyer security questionnaires |
|
Data privacy & protection |
Farmer, land, crop and borrower data discovery, consent and notices, minimisation and retention, DPDP programmes and breach workflows |
|
Fraud and integrity reviews |
Loan, subsidy, receipt and dealer incentive workflows, source data verification, anomaly rules and audit trails |
|
24/7 Managed SOC & incident response |
Device, platform, payment, cloud and identity monitoring, harvest-season threat watch, ransomware, fraud and data incident response, CERT-In reporting support |
4. Codec Networks bundles for the sector
Eleven of the twelve bundles in the Codec Networks Bundled Service Models apply directly to agribusinesses, agri-input companies, farm IoT providers, agritech marketplaces, warehousing and agri-credit platforms and FPOs; the Global Cyber Back-Office SPV Program (Bundle 12) is offered separately for international clients.
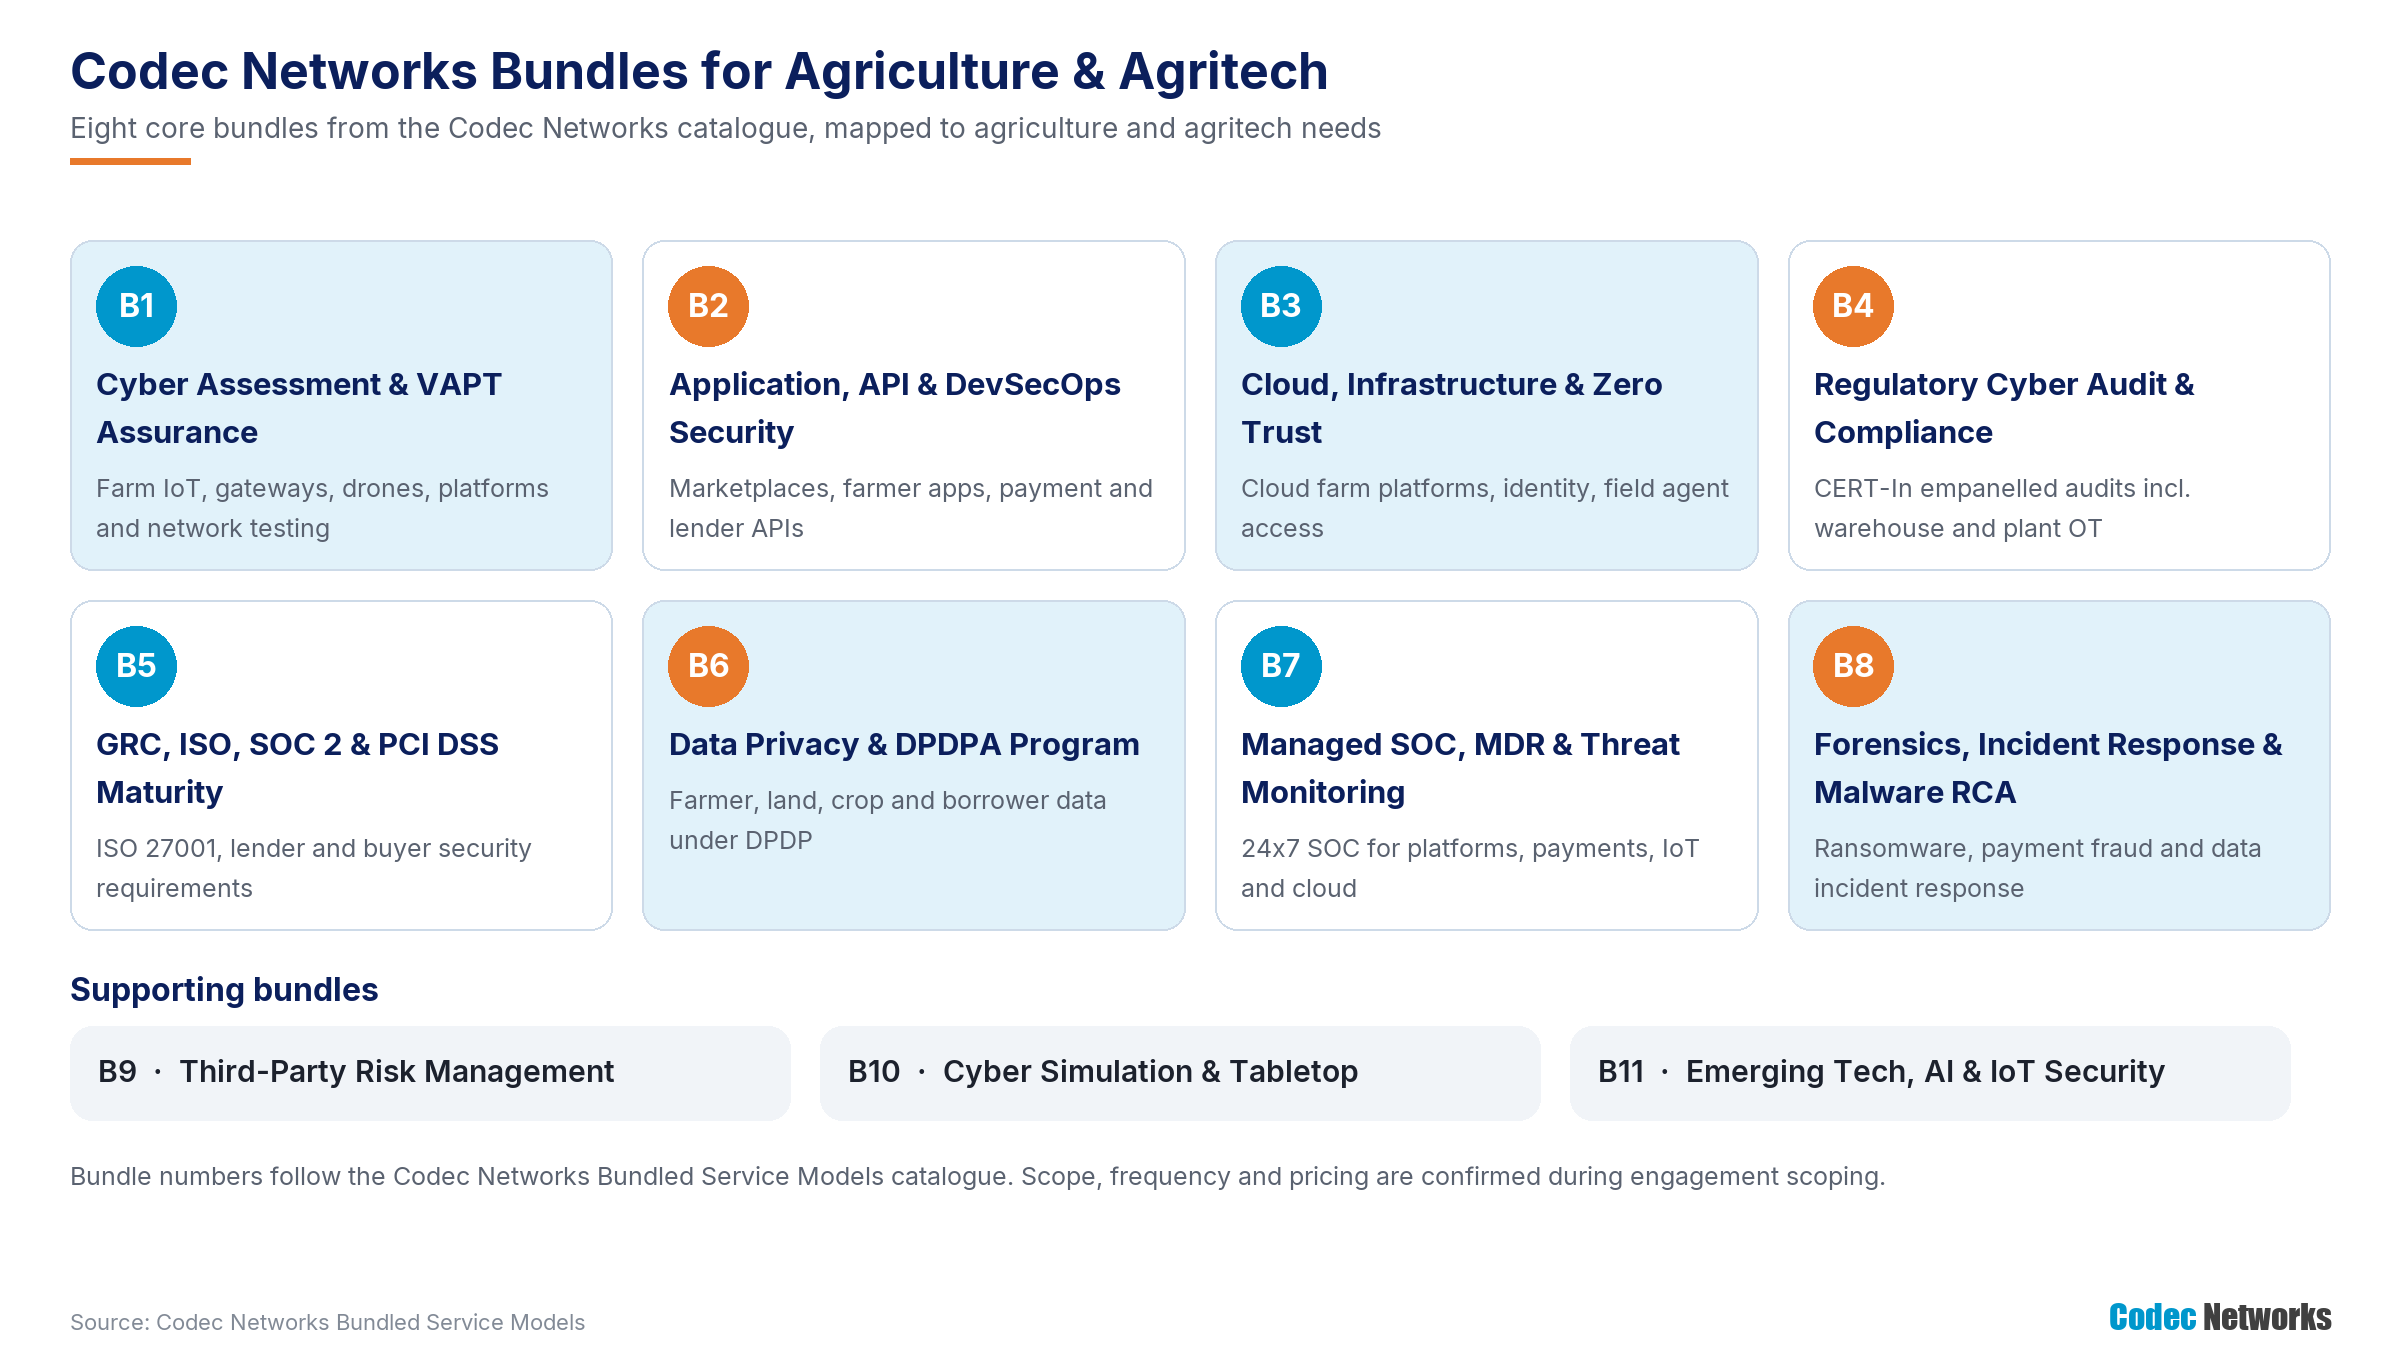
Figure 6: Codec Networks bundles applied to the sector.
|
Bundle |
Name |
Sector-relevant scope |
Best suited for |
Key deliverables |
|
B1 |
Cyber Assessment & VAPT Assurance Program |
Farm IoT, gateway, drone, warehouse network and platform testing |
Farm IoT providers, drone operators, agribusiness |
Assessment reports, retests and closure tracker |
|
B2 |
Application, API & DevSecOps Security Program |
Marketplaces, farmer and agent apps, payment, lender and AgriStack APIs |
Marketplaces, agri-credit and input platforms |
Test reports, fix verification, secure SDLC findings |
|
B3 |
Cloud, Infrastructure & Zero Trust Security Program |
Cloud platforms, identity, API keys, field agent access and segmentation |
Agritech start-ups, IoT and lending platforms |
Architecture review and remediation roadmap |
|
B4 |
Regulatory Cybersecurity Audit & Compliance Assurance Program |
CERT-In empanelled audits, including warehouse and plant OT |
Firms serving lenders, government and corporate buyers |
Audit report, gap matrix, evidence tracker |
|
B5 |
GRC, ISO, SOC 2 & Cyber Maturity Program |
ISO/IEC 27001 ISMS and lender, insurer and buyer security requirements |
Scaling agritech platforms and input groups |
Maturity scorecard, policies, ISMS documents |
|
B6 |
Data Privacy, DPDPA & Data Protection Program |
Farmer, land, crop and borrower data, DPDP readiness |
All platforms holding farmer data |
Privacy gap assessment, data map, roadmap |
|
B7 |
Managed SOC, MDR & Continuous Threat Monitoring Program |
24x7 SOC for devices, platforms, payments and cloud |
Marketplaces, IoT providers, cooperatives |
SOC reports, MTTD/MTTR, incident records |
|
B8 |
Digital Forensics, Incident Response & Malware RCA Program |
Ransomware, payment fraud and data incident response, forensics and RCA |
Any organisation facing a compromise or fraud |
Forensic report, RCA, reporting support |
|
B9 |
Third-Party Risk Management & Supply Chain Cyber Risk Program |
Device maker, cloud vendor, integrator, dealer and partner assurance |
Input firms, IoT providers, lending platforms |
Vendor risk register and assessment reports |
|
B10 |
Cyber Simulation, Awareness, Tabletop & Crisis Readiness Program |
Harvest-week ransomware, payout fraud and data leak tabletop exercises |
Leadership, operations, finance and platform teams |
Exercise reports and playbooks |
|
B11 |
Emerging Technology, AI, Web3 & Future Security Program |
IoT and drone security programmes, AI advisory and analytics risk |
Farm IoT, drone and advisory platforms |
Test report, readiness roadmap, findings |
5. Sector programmes built from the bundles
Codec Networks packages the catalogue bundles into six agriculture and agritech programmes.
|
Programme |
Built from bundles |
Challenges addressed |
|
Connected Farm Assurance |
B1, B11, B3 |
Sensors, gateways, controllers, brokers, drones and telematics |
|
Platform & Payment Integrity |
B2, B1, B7 |
Marketplaces, apps, APIs, callbacks, settlement and payouts |
|
Agri-Credit Trust |
B2, B3, B6 |
Loan apps, field agents, lender APIs, source data and borrower data |
|
Farmer Data Protection |
B6, B3, B9 |
Consent, data maps, cloud storage, vendors and DPDP readiness |
|
Harvest Resilience |
B7, B8, B10 |
Ransomware readiness, OT segmentation, recovery and exercises |
|
Trusted Inputs & Partners |
B9, B2, B5 |
Dealer portals, traceability codes, suppliers and partners |
6. Packages: Foundation, Assurance and Continuous Resilience
|
Package element |
Foundation |
Assurance |
Continuous Resilience |
|
Typical organisation |
Agritech start-ups and FPO platforms |
Marketplaces and agri-credit platforms |
Agribusiness and input groups |
|
Testing |
B2: app and API security test |
B1 + B2: platform and payment integration VAPT |
B1 + B2 + B11: IoT, OT and platform red team |
|
Audit and GRC |
B5: security policy and access rules |
B4 + B5: CERT-In empanelled audit, ISO 27001 |
B4 + B5 + B9: audits incl. OT, supplier and dealer assurance |
|
Architecture and privacy |
B3 + B6: cloud review, farmer data check |
B3 + B6: field agent access, DPDP programme |
B3 + B6 + B11: segmentation, DPDP, IoT security programme |
|
Monitoring and response |
IR retainer (B8) |
B7: managed SOC + B8 |
B7: SOC with plant and warehouse OT + B8 retainer |
|
Reporting |
Test report for partners and investors |
CTO, CISO and lender-ready reporting |
Board, buyer, lender and regulator-ready reporting |
7. Regulatory requirement-to-bundle mapping
|
Requirement (source) |
How Codec Networks helps |
Bundle |
|
Approved, consent-based use of AgriStack and scheme data (Digital Agriculture Mission; integration terms) |
Integration, consent flow and access control review |
B2, B6 |
|
Duties of lenders, lending service providers and loan apps (RBI digital lending rules) |
Loan app, API and partner security assessment |
B2, B5 |
|
Cyber incidents to CERT-In within six hours; 180-day logs in India (CERT-In Directions, 2022) |
Managed SOC, log architecture, IR retainer and reporting support |
B7, B8 |
|
Risk-based independent audits including OT and ICS (CERT-In audit guidelines, 2025) |
CERT-In empanelled audit of IT, warehouse and plant OT |
B4 |
|
Accurate warehouse records and electronic receipts (WDRA Act 2007; accreditation conditions) |
Warehouse system, access and integration review |
B1, B3 |
|
Labelling, registration and records for seeds and crop protection (Seeds Act 1966; Insecticides Act 1968) |
Traceability, dealer portal and record integrity review |
B2, B9 |
|
Reasonable security safeguards and breach intimation (DPDP Act 2023 and Rules 2025) |
DPDP gap assessment for farmer, land and borrower data |
B6, B8 |
|
Registration and permissions for drones (Drone Rules 2021; Digital Sky) |
Drone fleet platform and data handling review |
B11, B3 |
|
Auditor eligibility and independence Where a lender, buyer, scheme integration or CERT-In's audit guidelines call for independent or CERT-In empanelled auditors, Codec Networks—CERT-In empanelled for information security auditing services and empanelled with NICSI for application audit and compliance services (start-up category)—confirms eligibility and independence in each proposal and does not audit systems it has designed or operates. Codec Networks does not provide agronomic, scheme eligibility or lending advice, and device, drone and payment testing is performed only with authorisation, in agreed windows and controlled conditions. |
8. Threat-to-bundle coverage matrix
|
Threat / challenge |
Primary bundle |
Supporting bundles |
|
Farm IoT device and gateway compromise |
B1 |
B11, B7 |
|
Machinery telematics and agri-drone platform abuse |
B11 |
B2, B3 |
|
Marketplace and trading platform API flaws |
B2 |
B1, B7 |
|
Payment integration and settlement fraud |
B2 |
B7, B8 |
|
Farmer, trader and dealer account takeover |
B2 |
B3, B7 |
|
Farmer data exposure and consent failures |
B6 |
B3, B9 |
|
Misuse of public platform and scheme credentials |
B3 |
B5, B7 |
|
Agri-loan, subsidy and warehouse receipt fraud |
B2 |
B5, B8 |
|
Warehouse, cold store and processing OT tampering |
B1 |
B4, B7 |
|
Ransomware timed to sowing and harvest seasons |
B8 |
B3, B7, B10 |
|
Cloud misconfiguration and exposed data stores |
B3 |
B1, B7 |
|
Counterfeit input codes and dealer portal fraud |
B2 |
B9, B1 |
|
Theft of breeding data, trait IP and R&D |
B3 |
B5, B7 |
|
Phishing and payment diversion in commodity trade |
B10 |
B7, B8 |
|
Field agent mobile app and device risks |
B2 |
B3, B6 |
|
AI advisory, analytics and model data risks |
B11 |
B2, B6 |
|
Vendor, integrator and SaaS supplier risk |
B9 |
B5, B4 |
|
Weak logs, monitoring and 6-hour reporting |
B7 |
B4, B8 |
“Primary” and “supporting” indicate suggested combinations, not guaranteed mitigation or complete coverage.
9. Delivery methodology and deliverables
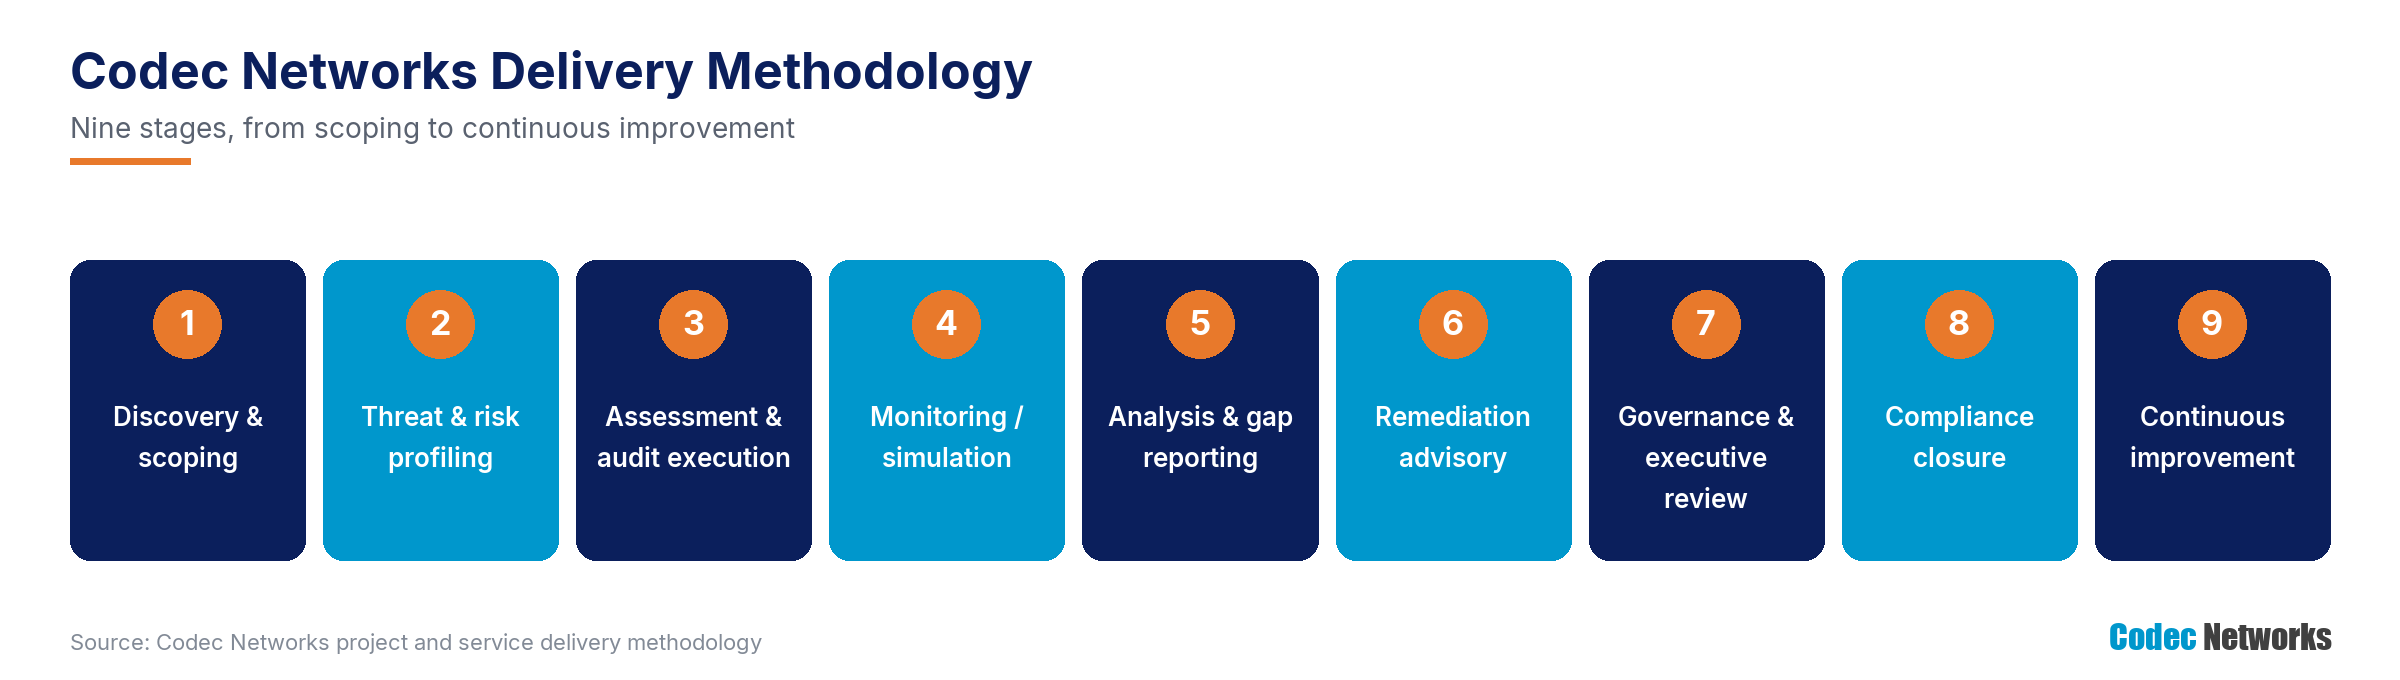
Figure 7: The Codec Networks delivery methodology.
Typical deliverables include farm IoT device, firmware and gateway test reports with message broker and cloud findings, drone fleet and telematics platform reviews, marketplace, farmer, dealer and agent app and API VAPT reports with retests, payment integration test reports covering callback verification, replay protection, settlement and payout logic and reconciliation, AgriStack, lender and partner integration and consent flow reviews, cloud configuration and storage exposure assessments, identity, API key and field agent access reviews, warehouse, cold store and plant OT assessments, dealer portal and traceability code reviews, loan, subsidy and receipt workflow fraud control reviews, supplier and partner assurance reports, CERT-In empanelled audit reports with gap matrices and closure trackers, ISO 27001 readiness reports and lender and buyer questionnaire support, a DPDP gap assessment for farmer, land and borrower data, managed SOC reports with harvest-season monitoring, forensic and root cause reports with CERT-In reporting support, and exercise reports.
10. Why Codec Networks
- CERT-In empanelled for information security auditing services, and empanelled with NICSI for application audit and compliance services (start-up category).
- Certified to ISO 9001:2015, ISO/IEC 27001:2022 and ISO/IEC 20000-1:2018.
- Full stack: VAPT, regulatory audit, managed SOC, forensics, privacy and Board advisory from one partner, so findings, monitoring and closure stay connected.
- Agriculture and agritech depth: farm IoT, drone and telematics testing, marketplace, lender and AgriStack integration testing, payment integration and settlement reviews, cloud and field agent access assessments and farmer data privacy programmes, combined with CERT-In empanelled audits, CERT-In's Directions, RBI's lending rules and the DPDP Act.
- Recognised frameworks and tools: OWASP ASVS/MASVS and API Top 10, MITRE ATT&CK, NIST CSF, ISO 27001 and PCI DSS; tools such as Burp Suite, Nessus, Metasploit, Prowler and leading SIEM/EDR platforms.
- Certified people: CEH, OSCP, CPENT, CISA, ISO 27001 LA/LI, CHFI, CTIA and ECIH professionals.
Annex: Indicative commercial ranges
For internal sales reference only—remove this annex before sharing externally. Ranges are taken from the Codec Networks Bundled Service Models and are subject to scoping, asset counts, frequency and service levels.
|
Bundle |
Package examples and indicative ranges |
|
B1 VAPT Assurance |
Essential ₹1.5–5 lakh; Professional ₹5–15 lakh; Enterprise ₹15–40 lakh; Annual retainer ₹25 lakh–₹1.5 crore |
|
B2 AppSec & DevSecOps |
API Quick Check ₹2–6 lakh; AppSec Professional ₹8–20 lakh; DevSecOps Maturity ₹12–35 lakh; Secure SDLC retainer ₹3–15 lakh/month |
|
B3 Cloud & Zero Trust |
Cloud Essential ₹3–8 lakh; Professional ₹8–25 lakh; Enterprise ₹25–75 lakh; Continuous assurance ₹2–10 lakh/month |
|
B4 Regulatory Audit |
Gap review ₹5–15 lakh; Full regulatory audit ₹15–50 lakh; Multi-framework audit ₹30 lakh–₹1.25 crore; Annual retainer ₹3–20 lakh/month |
|
B5 GRC, ISO, SOC 2 |
ISO readiness ₹5–15 lakh; ISO implementation ₹15–45 lakh; SOC 2 readiness ₹15–60 lakh; GRC retainer ₹2–12 lakh/month |
|
B6 Privacy & DPDPA |
Quick assessment ₹3–10 lakh; Implementation ₹10–40 lakh; DPO-as-a-Service ₹2–8 lakh/month; Privacy retainer ₹3–15 lakh/month |
|
B7 Managed SOC |
Starter ₹2–5 lakh/month; Professional ₹5–15 lakh/month; Enterprise ₹15–50 lakh/month; co-managed per FTE/shift |
|
B8 Forensics & IR |
Triage ₹3–15 lakh; Full investigation ₹15–75 lakh; Ransomware response ₹25 lakh–₹1.5 crore; IR retainer ₹5–50 lakh/year |
|
B9 TPRM |
₹25,000–₹2 lakh per vendor; batch pricing for 50–500 vendors; retainer ₹3–25 lakh/month |
|
B10 Simulation & Tabletop |
Awareness ₹1–5 lakh; Phishing simulation ₹2–10 lakh; Tabletop ₹5–20 lakh; Cyber war-game ₹15–75 lakh; Annual retainer ₹10 lakh–₹1 crore/year |
|
B11 Emerging Tech |
AI/LLM risk review ₹5–25 lakh; Smart contract audit ₹5–50 lakh; Emerging tech retainer ₹5–25 lakh/month |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: Service scope, deliverables, monitoring coverage and service levels are confirmed during engagement scoping. Services support risk reduction and assurance but do not guarantee prevention of all cyber incidents or regulatory compliance. Regulatory references are summaries; confirm against the official instruments applicable to each entity.