

Resources Categories
INDUSTRY FACT FILE · AVIATION & AEROSPACE
Market Landscape and the Drivers of Cybersecurity Demand in Aviation and Aerospace
The business, technology, regulatory, legal and partner forces that create cybersecurity, audit and assurance work for airlines, airports, handlers, MRO firms and aerospace manufacturers.
|
In this document 1. Market landscape 2. Business drivers 3. Technology drivers 4. Regulatory drivers: CERT-In, ICAO Annex 17, BCAS, NCIIPC, DPDP, SEBI and EASA Part-IS 5. Legal and statutory drivers 6. How the drivers differ by organisation type 7. What this means for buyers and for Codec Networks |
1. Market landscape
Indian aviation is growing on every axis. Domestic passenger traffic reached about 16.54 crore in 2024-25, airports handled about 3.7 million tonnes of cargo, UDAN had operationalised more than 600 regional routes by August 2025, large airline groups have ordered aircraft in record numbers, new greenfield airports and terminals are opening, and defence and aerospace exports reached a record ₹23,622 crore in 2024-25 as Indian suppliers move deeper into global OEM programmes. A small number of airline and airport groups dominate, surrounded by handlers, MROs, cargo operators, technology providers and a growing aerospace supply base.
Cybersecurity demand follows the coupling of the system. One provider's outage stops many airports; one processor's breach exposes millions of passports; one supplier's ransomware stops an OEM's line. CERT-In expects six-hour reporting and independent audits that include OT, NCIIPC protects notified transport systems, ICAO Annex 17 asks States to protect critical aviation ICT, listed companies disclose incidents, EASA Part-IS reaches EU-approved organisations and the DPDP Act will regulate passenger data. Spending is shifting from perimeter IT towards airport OT assessment, provider and supplier assurance, passenger data protection, resilience engineering and monitoring that covers airline, airport and OT estates.
|
16.5 crore Domestic air passengers in FY25 |
3.7 m tonnes Air cargo handled at Indian airports in FY25 |
₹23,622 crore Record defence and aerospace exports in FY25 |
May 2027 Most DPDP obligations take effect |
|
Market segment |
Landscape and buying behaviour |
Cybersecurity opportunity |
|
Airline groups |
Large fleets, loyalty programmes, listed parents, global alliances and providers |
App and API testing, provider assurance, passenger data programmes, SOC, Board reporting |
|
Metro airport operators |
PPP hubs with complex OT, retail and many tenants; new terminals |
Airport IT/OT assessments, segmentation, fallback rehearsal, SOC |
|
AAI and regional airports |
Many sites, shared platforms, UDAN growth, constrained teams |
Baseline IT/OT assessments, common controls, managed monitoring |
|
Handlers, MROs and cargo operators |
Service providers with access to airline and airport systems; DGCA and EASA approvals |
Baseline assessments, access controls, ISMS and Part-IS readiness |
|
Aerospace manufacturers and suppliers |
Public-sector majors and private suppliers to global OEMs and defence |
Design data protection, production OT, OEM assurance, SOC |
2. Business drivers
|
Business driver |
Buying trigger |
Relevant services |
|
Operational continuity |
Platform, baggage or dispatch outages cascade across the network |
Resilience programmes, segmentation, fallback rehearsal, SOC |
|
Passenger trust and brand |
Passport-grade data breaches and loyalty fraud erode trust |
Provider assurance, privacy programmes, ATO testing |
|
Partner, alliance and lessor requirements |
Codeshare, alliance, lessor and insurer questionnaires |
ISO 27001, questionnaire readiness, independent audits |
|
OEM contracts and export controls |
Aerospace OEMs audit supplier security and data handling |
Data classification, OEM assurance, segmentation |
|
Board accountability and disclosure |
Listed companies disclose incidents; Boards own risk |
Board advisory, incident records, audit programmes |
|
Fraud losses |
Loyalty, refund and BEC fraud |
ATO testing, payment controls, fraud-aware monitoring |
|
Cyber insurance |
Insurers require OT controls, backups and MFA evidence |
Control validation, ransomware readiness reviews |
3. Technology drivers
|
Technology driver |
Exposure created |
Codec Networks opportunity |
|
Shared platforms and cloud services |
PSS, departure control and common-use systems concentrate risk |
Provider assurance, fallback rehearsal, integration monitoring |
|
Airport OT |
Baggage, BMS, access control, CCTV and screening on flat networks |
OT assessments, segmentation, vendor access brokering, OT monitoring |
|
Biometrics and kiosks |
DigiYatra gates and self-service devices on campus networks |
Biometric data protection, device and network testing |
|
Apps, APIs and loyalty platforms |
Business logic and stored value exposed at scale |
App and API testing, ATO testing, fraud controls |
|
Connected aircraft and EFBs |
Data links and devices depending on ground systems |
Device management, data integrity, vendor assessment |
|
AI in operations and customer service |
Chatbots, disruption management and predictive maintenance models |
AI risk reviews and data governance |
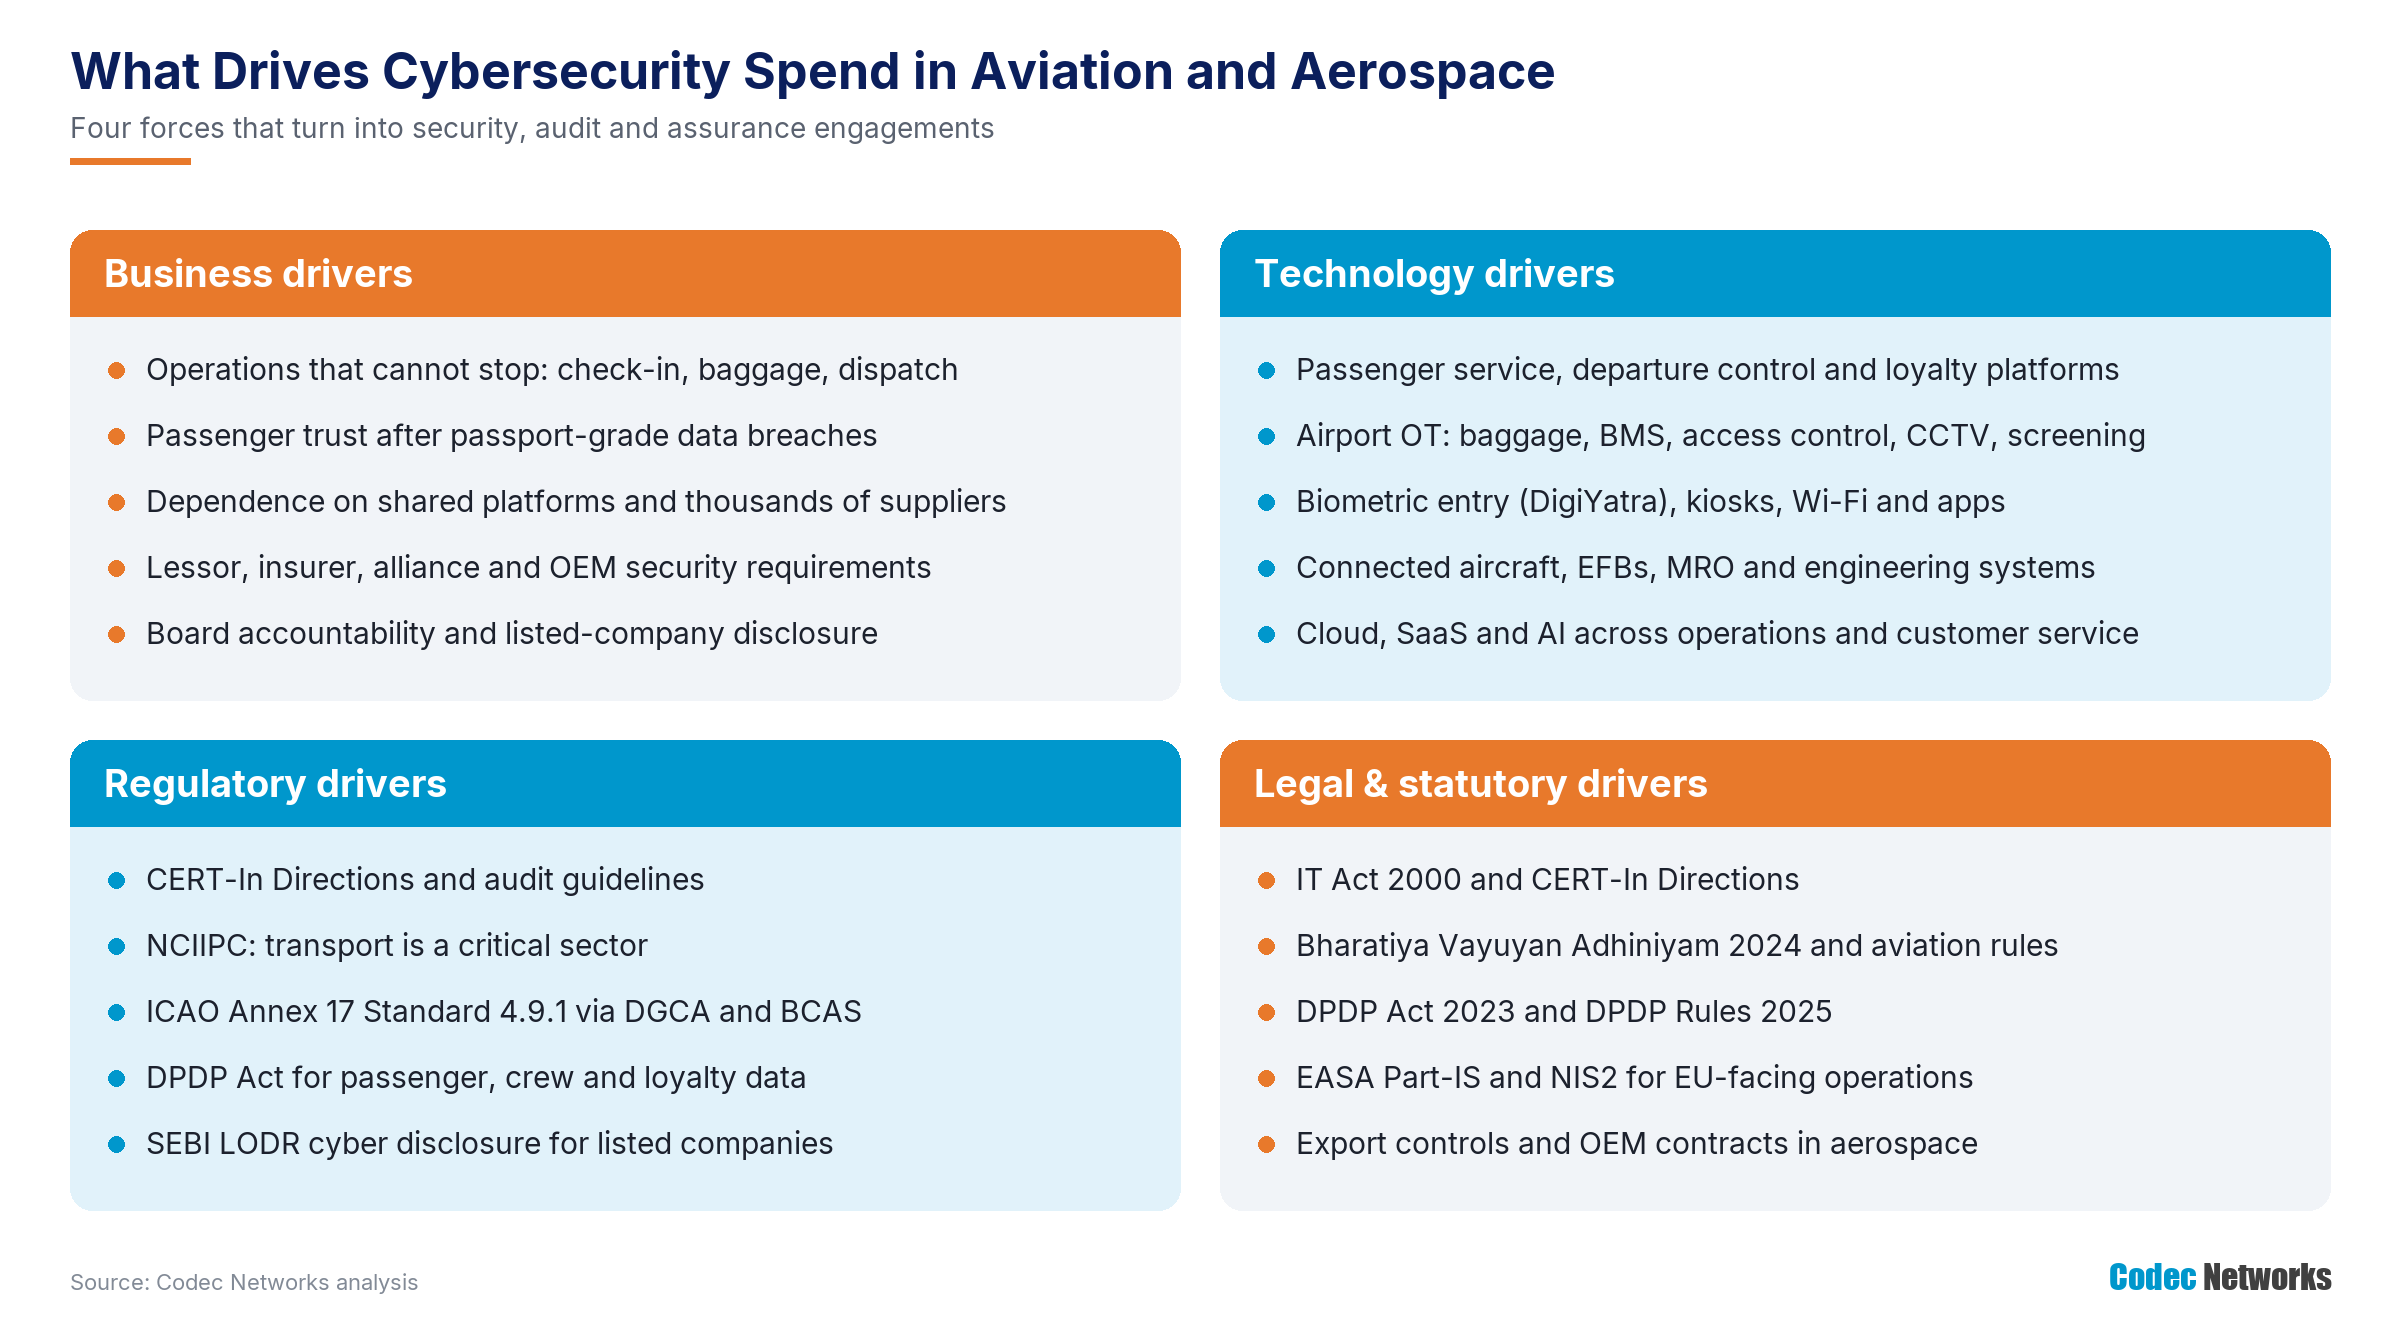
Figure 3: The four groups of drivers behind cybersecurity spending in aviation and aerospace.
4. Regulatory drivers: CERT-In, ICAO Annex 17, BCAS, NCIIPC, DPDP, SEBI and EASA Part-IS
|
Instrument |
Key requirements |
|
CERT-In Directions (2022) |
Six-hour incident reporting; 180-day ICT logs in India; applies to bodies corporate including airlines, airports and suppliers |
|
CERT-In audit policy guidelines (July 2025) |
Risk-based, independent cyber audits covering IT, OT/ICS, cloud and applications |
|
NCIIPC (IT Act Section 70A) |
Transport is a critical sector; notified protected systems carry additional duties |
|
ICAO Annex 17 (4.9.1, 4.9.2) via DGCA and BCAS |
Identification and protection of critical aviation ICT systems; security by design, supply-chain and remote-access protection recommended |
|
SEBI LODR Regulations (listed companies) |
Quarterly disclosure of cyber incidents in the corporate governance report |
|
DPDP Act 2023 and Rules 2025 |
Passenger, crew, loyalty, biometric and employee data; most obligations from May 2027 |
|
EASA Part-IS (EU 2022/1645 and 2023/203) |
Information security management systems for EU-approved aerodromes, design and production organisations (from October 2025) and air operators and maintenance organisations (from February 2026) |
|
Confirm applicability Obligations depend on licences and approvals, listing status, any NCIIPC notifications and where you operate and with whom. Confirm against the official instruments and your contracts. |
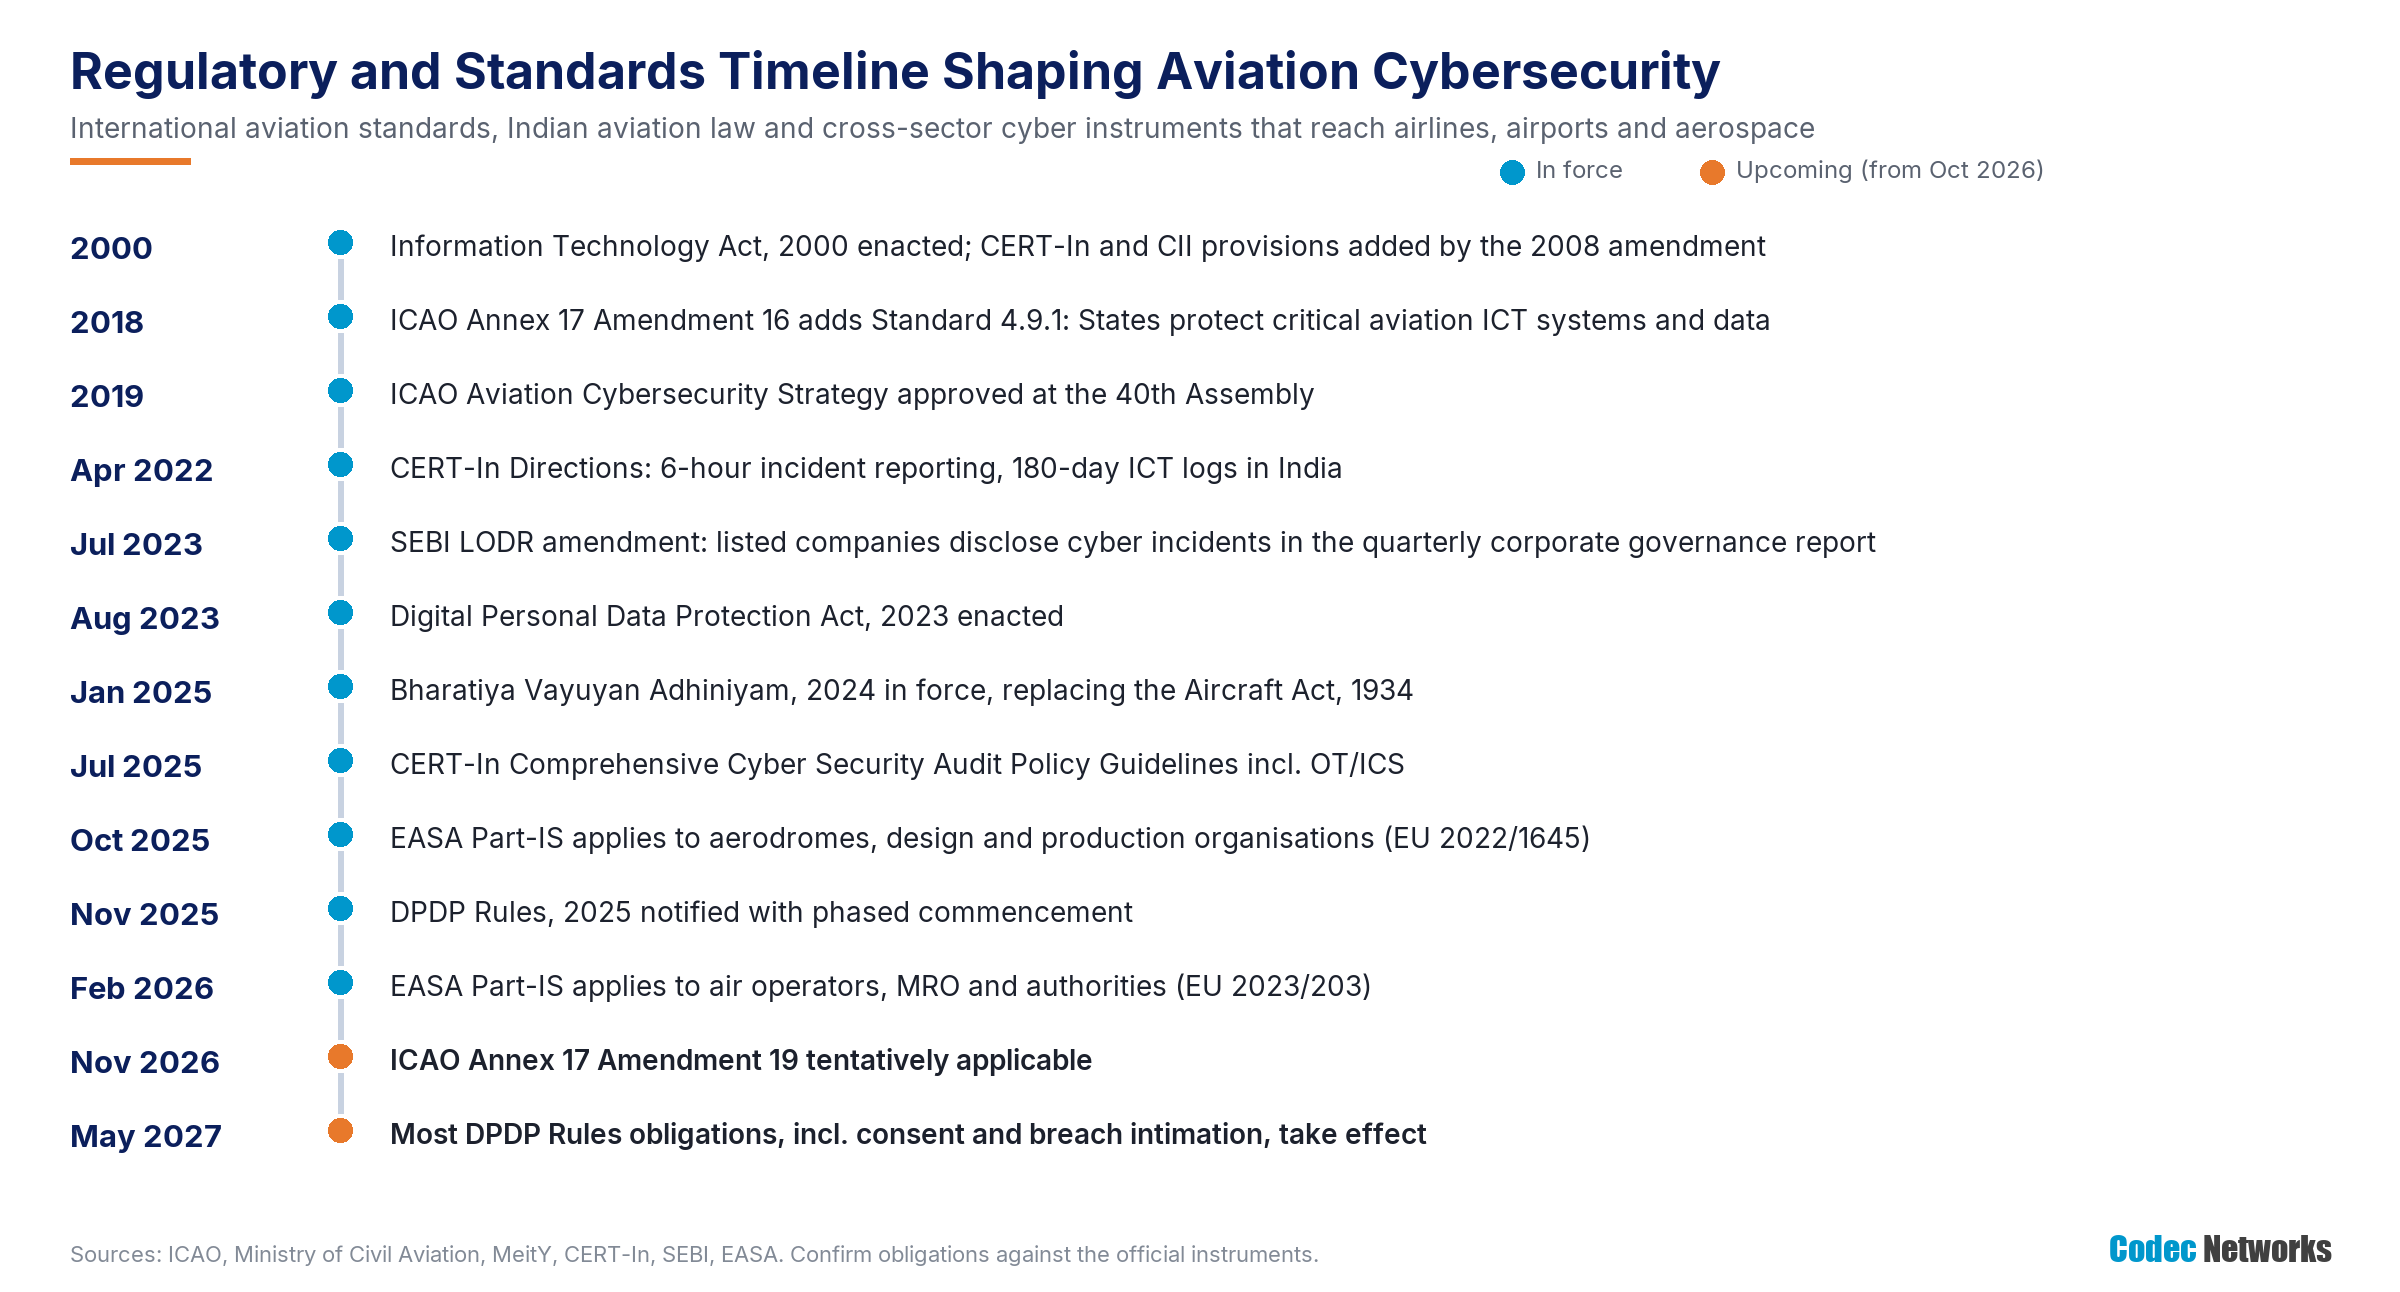
Figure 4: Regulatory and standards timeline shaping aviation cybersecurity, as of October 2026.
5. Legal and statutory drivers
|
Law or obligation |
Relevance |
Demand created |
|
IT Act, 2000 and CERT-In Directions |
Incident reporting, logging and protected systems |
SOC, logging, audits and incident response |
|
Bharatiya Vayuyan Adhiniyam, 2024 and rules |
Civil aviation safety, security and operations law |
Security programme alignment, system assurance |
|
Companies Act, 2013 and SEBI LODR |
Board risk management; listed-company disclosure |
Board reporting, incident records |
|
DPDP Act, 2023 and Rules, 2025 |
Personal data of passengers, crew, members and employees |
Privacy programmes and breach workflows |
|
Customs Act and cargo security regimes |
Cargo filing, regulated agents, customs integrations |
Credential and filing controls |
|
Export-control and defence procurement rules |
Controlled technical data at aerospace suppliers |
Data classification, access control, evidence |
|
Partner, lessor, insurer and OEM contracts |
Security clauses, audits, notification duties, warranties |
Independent testing, certifications, questionnaire evidence |
6. How the drivers differ by organisation type
|
Organisation type |
Dominant business drivers |
Dominant technology drivers |
Principal regulatory drivers |
|
Airlines |
Continuity, passenger trust, disclosure |
PSS, apps, loyalty, providers |
CERT-In, DGCA/BCAS, SEBI LODR, DPDP |
|
Airport operators |
Terminal and airside continuity, tenants |
Baggage, BMS, access control, common-use |
CERT-In incl. OT, BCAS, NCIIPC, Annex 17 |
|
Handlers and MROs |
Keeping airline and airport contracts |
Shared systems, records, OEM links |
CERT-In, DGCA approvals, Part-IS |
|
Aerospace suppliers |
OEM contracts, export compliance |
PLM, ERP, production OT |
CERT-In, export controls, OEM audits |
|
Platform providers |
Customer trust, concentration risk |
Multi-tenant platforms |
CERT-In, customer contracts, NCIIPC where notified |
7. What this means for buyers and for Codec Networks
|
Customer buying need |
Recommended offering |
Natural recurring engagement |
|
“Would ransomware stop our check-in, baggage or dispatch?” |
Resilience review: dependency mapping, segmentation, backups, fallback rehearsal |
Annual resilience testing and exercises |
|
“Our provider was breached—what passenger data did we lose?” |
Processor and data mapping, DPDP programme, breach workflow |
Annual provider assessments |
|
“Our alliance partner or lessor sent a security questionnaire.” |
Questionnaire readiness and ISO 27001 gap assessment |
Annual recertification support |
|
“Are our baggage system and BMS reachable from the office?” |
Airport IT/OT assessment and segmentation review |
Vendor access recertification |
|
“Members say their miles were stolen.” |
ATO testing, loyalty platform and redemption control review |
Continuous fraud-aware monitoring |
|
“We need 24x7 monitoring across airline, airport and OT.” |
Aviation SOC |
Continuous monitoring |
|
“We need an independent audit that includes OT.” |
CERT-In-aligned IT/OT audit |
Annual audits |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: This document is general industry guidance based on public information available as of October 2026. It is not legal, safety or regulatory advice. Obligations differ by licence, approval, listing status, operations and partners; confirm them against the official CERT-In, MeitY, Ministry of Civil Aviation, DGCA, BCAS, NCIIPC, SEBI, ICAO and EASA instruments and your partner and lessor contracts.