

Resources Categories
INDUSTRY FACT FILE · CLOUD, DATA CENTRES & HOSTING
Market Landscape and the Drivers of Cybersecurity Demand in Cloud and Data Centres
The business, technology, regulatory, legal and statutory forces that create cybersecurity, audit and assurance work for cloud, data centre and hosting providers.
|
In this document 1. Market landscape 2. Business drivers 3. Technology drivers 4. Regulatory drivers: CERT-In, MeitY and customer regulators 5. Legal and statutory drivers 6. How the drivers differ by provider type 7. What this means for buyers and for Codec Networks |
1. Market landscape
India's data centre and cloud market is growing quickly, driven by digital public infrastructure, data-localisation expectations, BFSI and government cloud adoption and AI workloads. Global hyperscalers, Indian data centre operators, telecom-led clouds and specialist hosting providers compete for regulated customers who demand demonstrable security and resilience.
|
6 hours Incident reporting to CERT-In |
5 years Subscriber record retention for cloud and VPS providers |
180 days ICT log retention in India |
May 2027 Most DPDP obligations take effect |
|
Market segment |
Landscape and buying behaviour |
Cybersecurity opportunity |
|
Hyperscale and large clouds |
Global platforms with Indian regions |
Assurance for regulated customers, red teaming |
|
Indian data centre operators |
Colocation and growing cloud services |
Facility OT, physical security, ISO and SOC 2 |
|
Hosting and VPS providers |
Price-competitive, high customer volumes |
Virtualisation hardening, abuse and record-keeping |
|
Sovereign and government clouds |
Empanelled services for public sector |
Empanelment audits, SOC, red teaming |
2. Business drivers
|
Business driver |
Buying trigger |
Relevant services |
|
Regulated-customer demand |
BFSI and government need assured cloud |
Empanelment and audit support |
|
SLAs and penalties |
Outages trigger credits and claims |
Resilience and DR testing |
|
Customer audits |
Right-to-audit clauses |
Evidence packs and certifications |
|
Competition |
Security as a differentiator |
ISO 27017/27018, SOC 2 |
|
Reputation |
Platform incidents affect many customers |
SOC and incident readiness |
3. Technology drivers
|
Technology driver |
Exposure created |
Codec Networks opportunity |
|
Hypervisors |
Ransomware at the virtualisation layer |
Virtualisation security reviews |
|
Out-of-band management |
Below-OS compromise |
BMC and IPMI testing |
|
Control planes and APIs |
Console takeover |
Control-plane testing |
|
Facility OT |
Cooling and power manipulation |
OT segmentation reviews |
|
GPU infrastructure |
Firmware and abuse risks |
Hardware and supply-chain reviews |
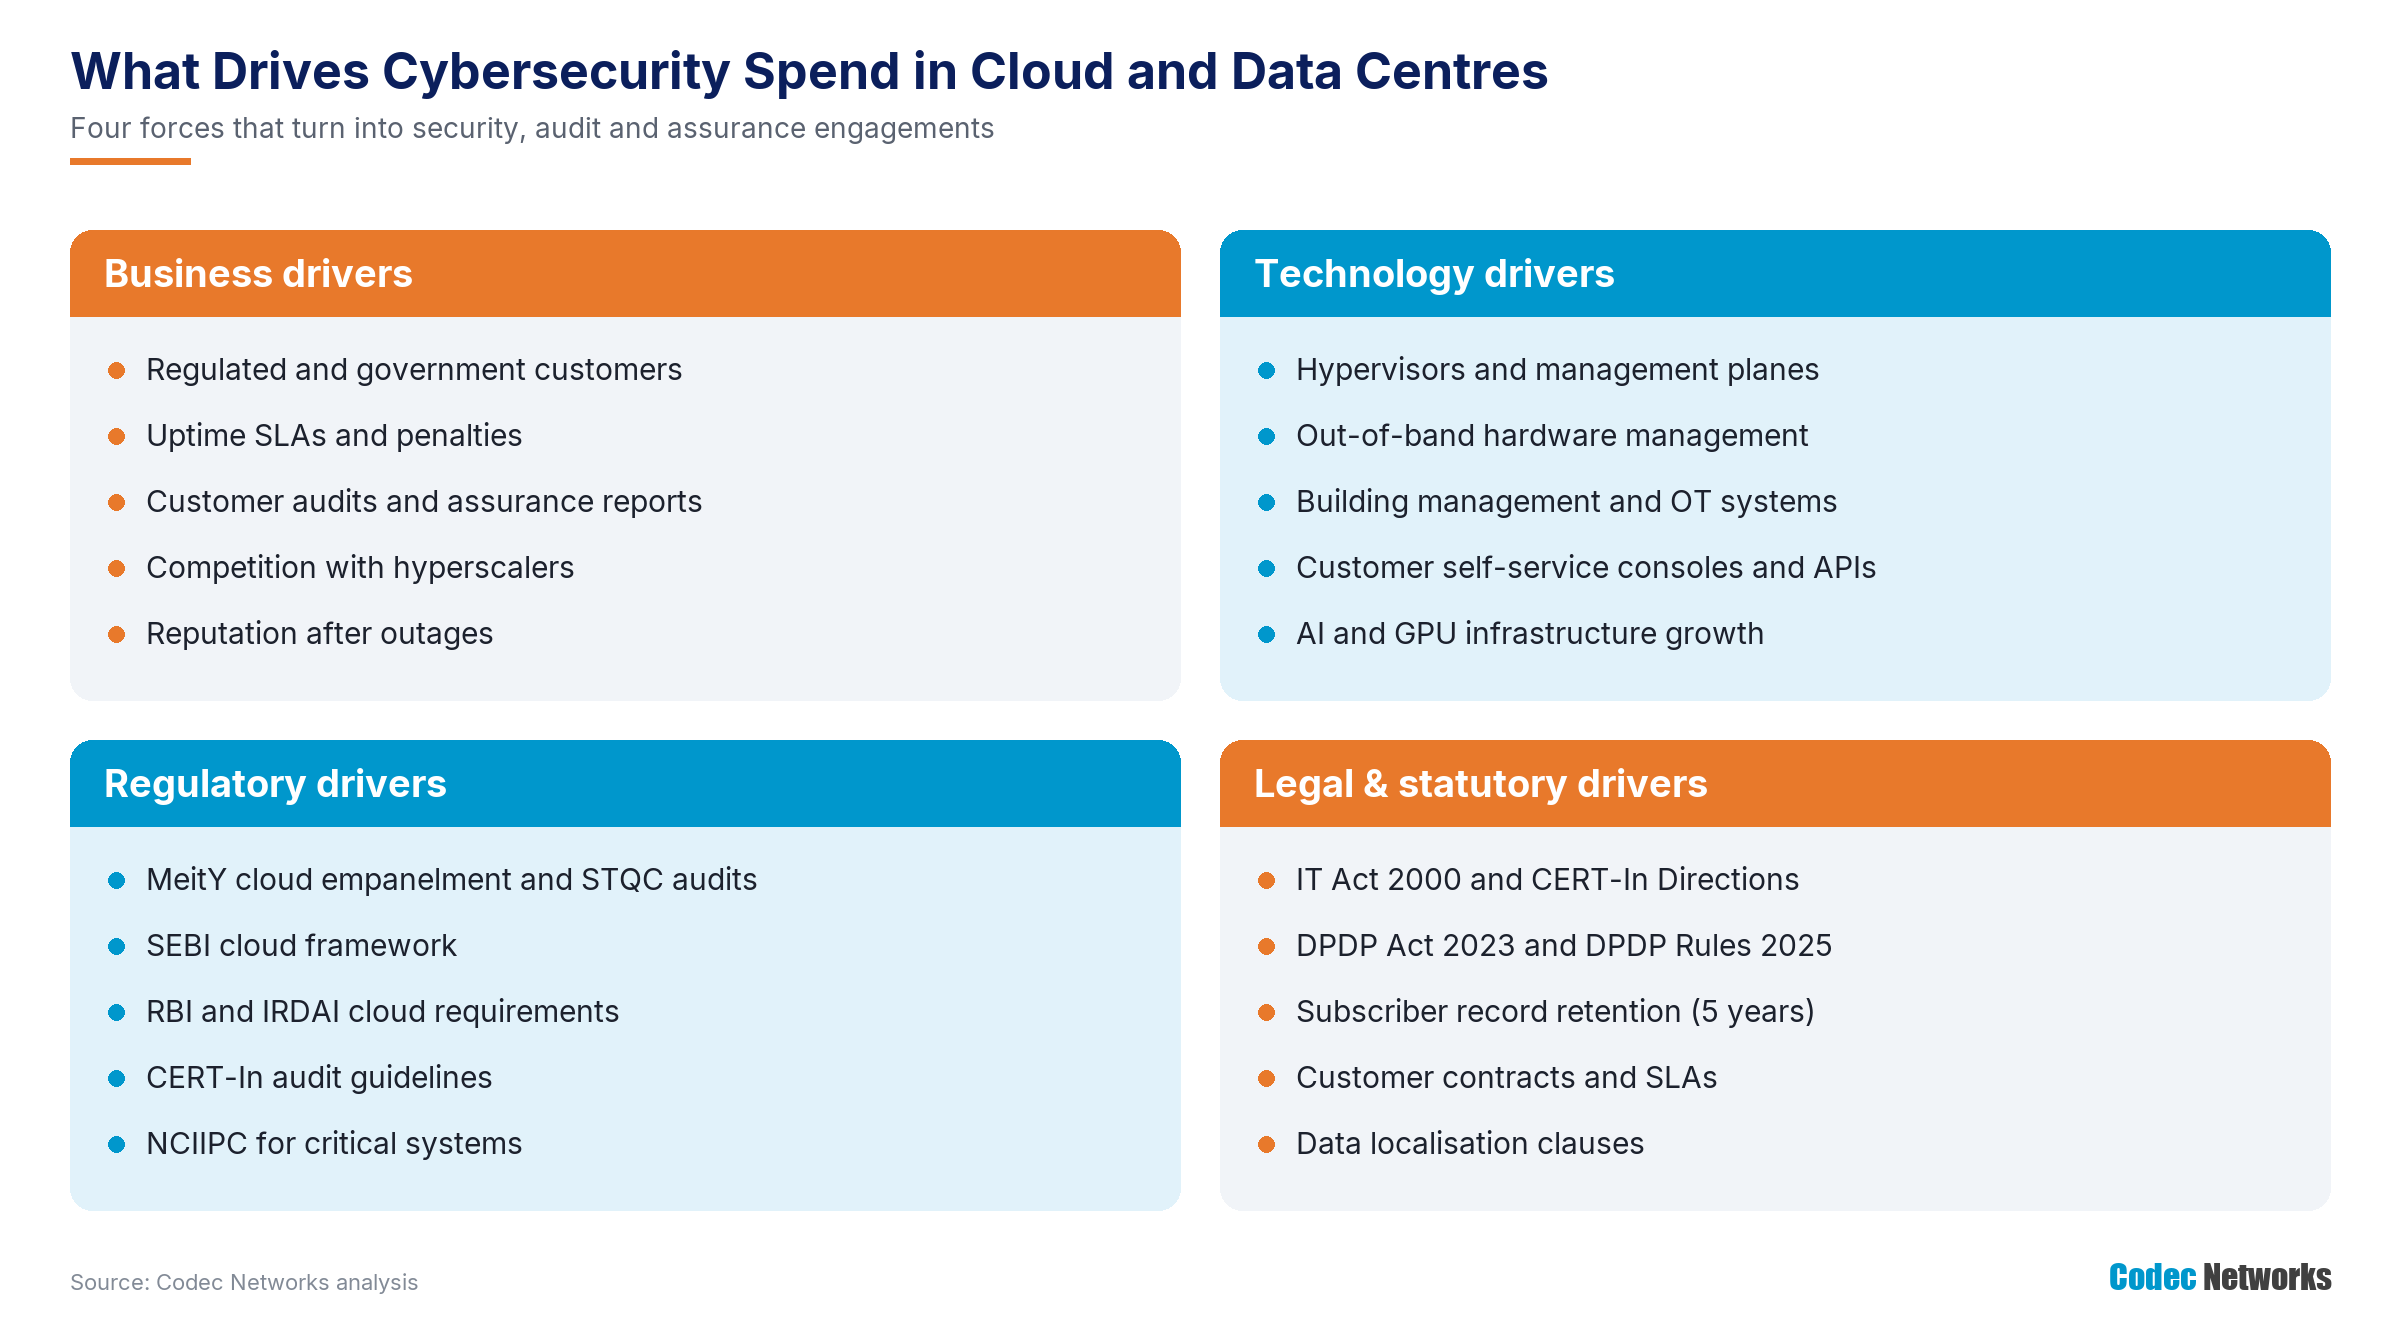
Figure 3: The four groups of drivers behind cybersecurity spending in cloud and data centres.
4. Regulatory drivers: CERT-In, MeitY and customer regulators
|
Instrument |
Key requirements |
|
CERT-In Directions (2022) |
Six-hour reporting; 180-day logs; clock synchronisation; five-year subscriber records for data centres, cloud and VPS providers |
|
MeitY empanelment |
Empanelment of cloud services for government, with STQC audits |
|
SEBI cloud framework (2023) |
Governance, security, localisation and audit requirements for SEBI-regulated entities' cloud use |
|
RBI and IRDAI |
Cloud as outsourcing for banks and NBFCs; IRDAI 2026 requires MeitY-empanelled CSPs with STQC audit status |
|
DPDP Act 2023 and Rules 2025 |
Safeguards for personal data; most obligations from May 2027 |
|
Direct and flow-down duties CERT-In's provider duties apply directly; customer regulator rules usually apply through empanelment and contracts. Confirm against the official instruments. |
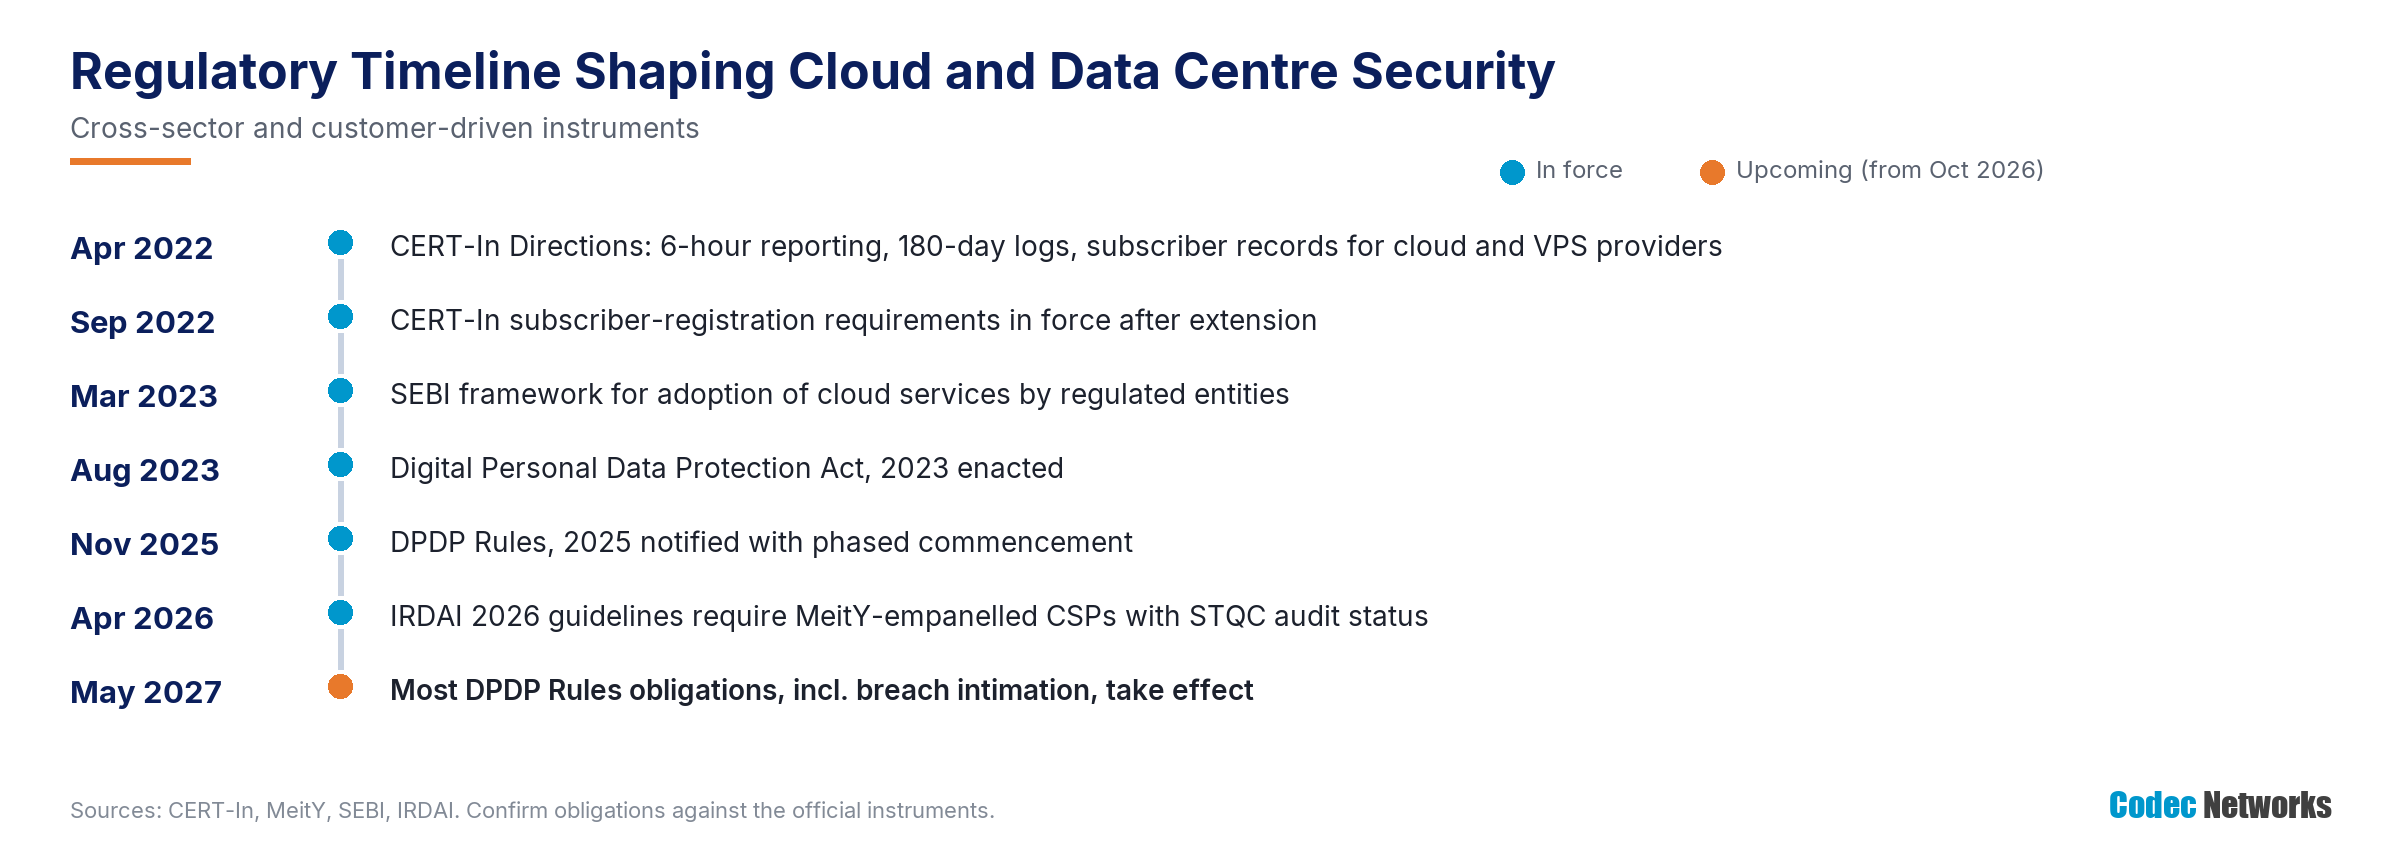
Figure 4: Regulatory timeline shaping cloud and data centre security, as of October 2026.
5. Legal and statutory drivers
|
Law or obligation |
Relevance |
Demand created |
|
IT Act, 2000 and CERT-In Directions |
Provider duties for reporting, logs and records |
Logging, SOC and records management |
|
DPDP Act, 2023 and Rules, 2025 |
Customer personal data on the platform |
Privacy and data handling controls |
|
IT Act Section 70 and NCIIPC |
Protected systems and CII |
Enhanced controls and audits |
|
Law-enforcement requests |
Lawful access to subscriber information |
Request-handling processes |
|
Contracts and SLAs |
Availability, security and audit rights |
Assurance evidence and resilience testing |
6. How the drivers differ by provider type
|
Provider type |
Dominant business drivers |
Dominant technology drivers |
Principal regulatory drivers |
|
Cloud providers |
Regulated-customer trust |
Control plane, hypervisors |
CERT-In, MeitY, SEBI, RBI, IRDAI |
|
Colocation |
Uptime, facility trust |
BMS, power, cooling |
CERT-In, facility and safety rules |
|
Managed hosting |
SLAs, customer retention |
Hypervisors, backups |
CERT-In, DPDP, contracts |
|
VPS providers |
Volume growth, abuse control |
Provisioning and abuse desks |
CERT-In subscriber records |
7. What this means for buyers and for Codec Networks
|
Customer buying need |
Recommended offering |
Natural recurring engagement |
|
“Could ransomware hit every customer?” |
Virtualisation and backup review |
Annual resilience testing |
|
“We need MeitY empanelment.” |
Empanelment readiness and audit support |
Periodic STQC audit support |
|
“Are we meeting CERT-In's provider duties?” |
Record-keeping and logging gap assessment |
Annual compliance review |
|
“Customers want ISO 27017 and SOC 2.” |
Readiness and implementation |
Annual audit support |
|
“Our facility systems are networked.” |
Facility OT assessment |
Continuous OT monitoring |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: This document is general industry guidance based on public information available as of October 2026. Customer regulator requirements apply through contracts and empanelment. Confirm obligations against the official CERT-In, MeitY, SEBI, RBI and IRDAI instruments before making compliance decisions.