

Resources Categories
INDUSTRY FACT FILE · FMCG, FOOD & BEVERAGES
Market Landscape and the Drivers of Cybersecurity Demand in FMCG, Food and Beverages
The business, technology, regulatory, legal, statutory and retailer forces that create cybersecurity, audit and assurance work for consumer goods groups, food processors, beverage companies, dairies, cold-chain operators and distributors.
|
In this document 1. Market landscape 2. Business drivers 3. Technology drivers 4. Regulatory drivers: CERT-In, SEBI, DPDP, FSSAI, Legal Metrology and GST 5. Legal and statutory drivers 6. How the drivers differ by company type 7. What this means for buyers and for Codec Networks |
1. Market landscape
India's FMCG, food and beverage sector is large, fragmented and digitising fast. Listed consumer goods groups and multinational subsidiaries dominate branded categories; regional food and beverage companies, PLI-backed processors and dairy cooperatives compete in staples, snacks, dairy and drinks; cold-chain and warehouse operators serve all of them; and tens of thousands of distributors, now on company-run apps and distributor management systems, carry products to millions of outlets. Quick commerce, e-commerce and D2C add integrated channels and first-party consumer data on top of general trade.
Cybersecurity demand follows that structure. Companies have seen ransomware stop order processing and empty shelves, scheme fraud leak through distributor portals, cold-chain and logistics partners go offline and consumer apps leak data; listed groups must disclose incidents; CERT-In expects independent audits that include OT; retailers and insurers ask for control evidence; and DPDP turns loyalty data into an obligation. Spending is shifting from basic IT security to plant OT assessments, distributor platform testing, partner assurance, consumer data protection and monitoring that covers plants, depots and channels.
|
₹10,900 cr PLI outlay for food processing, 2021-22 to 2026-27 |
171 Companies approved under the food processing PLI by early 2025 |
₹5 crore Turnover above which GST e-invoicing applies since August 2023 |
May 2027 Most DPDP obligations take effect |
|
Market segment |
Landscape and buying behaviour |
Cybersecurity opportunity |
|
Listed consumer goods groups and multinationals |
Many plants and brands, group ERP, DMS at scale, SEBI disclosure, global security standards |
Programme-level OT security, DMS and app testing, SOC, Board reporting, DPDP |
|
Regional food and beverage companies |
Growing plants and distribution, lean security teams, retailer and PLI scrutiny |
IEC 62443 assessments, segmentation, DMS testing, managed SOC |
|
Dairies and cooperatives |
Milk collection and payments, cold chains, member and consumer data |
IoT and plant assessment, payment controls, DPDP |
|
Cold-chain and warehouse operators |
Customer stock at risk, WMS and telematics, thin margins |
Baseline assessment, backups, customer evidence, monitoring |
|
Distributor networks and channel platforms |
Thousands of small businesses on company platforms |
Portal and app testing, onboarding controls, fraud analytics |
2. Business drivers
|
Business driver |
Buying trigger |
Relevant services |
|
Shelf availability and service levels |
Order processing or dispatch stops and distributors run dry |
Ransomware resilience, segmentation, dispatch recovery |
|
Food safety and recalls |
Tampered or unavailable batch and temperature records |
Record integrity, OT assessments, recall system reviews |
|
Trade scheme and claims integrity |
Portals and apps abused to inflate claims |
DMS and API testing, analytics, access controls |
|
Consumer trust and brand reputation |
App breaches, scams quoting consumer data, counterfeits |
App and API testing, DPDP programme, brand monitoring |
|
Partner dependence |
Co-packers, 3PLs and cold storage can stop supply |
Supply chain assurance programmes |
|
Board accountability and disclosure |
Listed companies disclose incidents; Boards own risk |
Board advisory, incident records, audit programmes |
|
Fraud and financial loss |
BEC against supplier, farmer and distributor payments |
Payment controls, BEC simulation, SOC |
3. Technology drivers
|
Technology driver |
Exposure created |
Codec Networks opportunity |
|
Plant PLCs, SCADA and packaging lines |
Legacy controllers and flat networks connected to MES and ERP |
IEC 62443 assessments, segmentation, OT monitoring |
|
Distributor management systems and sales apps |
Thousands of external users and scheme logic exposed through APIs |
Portal, app and API testing, access and claims controls |
|
Cold-chain IoT and telematics |
Internet-connected gateways in cold rooms and trucks |
IoT security assessment, DMZ design, tamper-evident logs |
|
Cloud ERP, OMS and trade-promotion platforms |
Business stops when the platform or identity fails |
Cloud posture, identity review, backup validation |
|
Retailer EDI, marketplace and quick-commerce APIs |
Deep integration with partners' systems |
Integration testing, access controls, monitoring |
|
Loyalty apps, D2C and CRM |
First-party consumer data built by agencies |
Mobile and API testing, vendor reviews, DPDP |
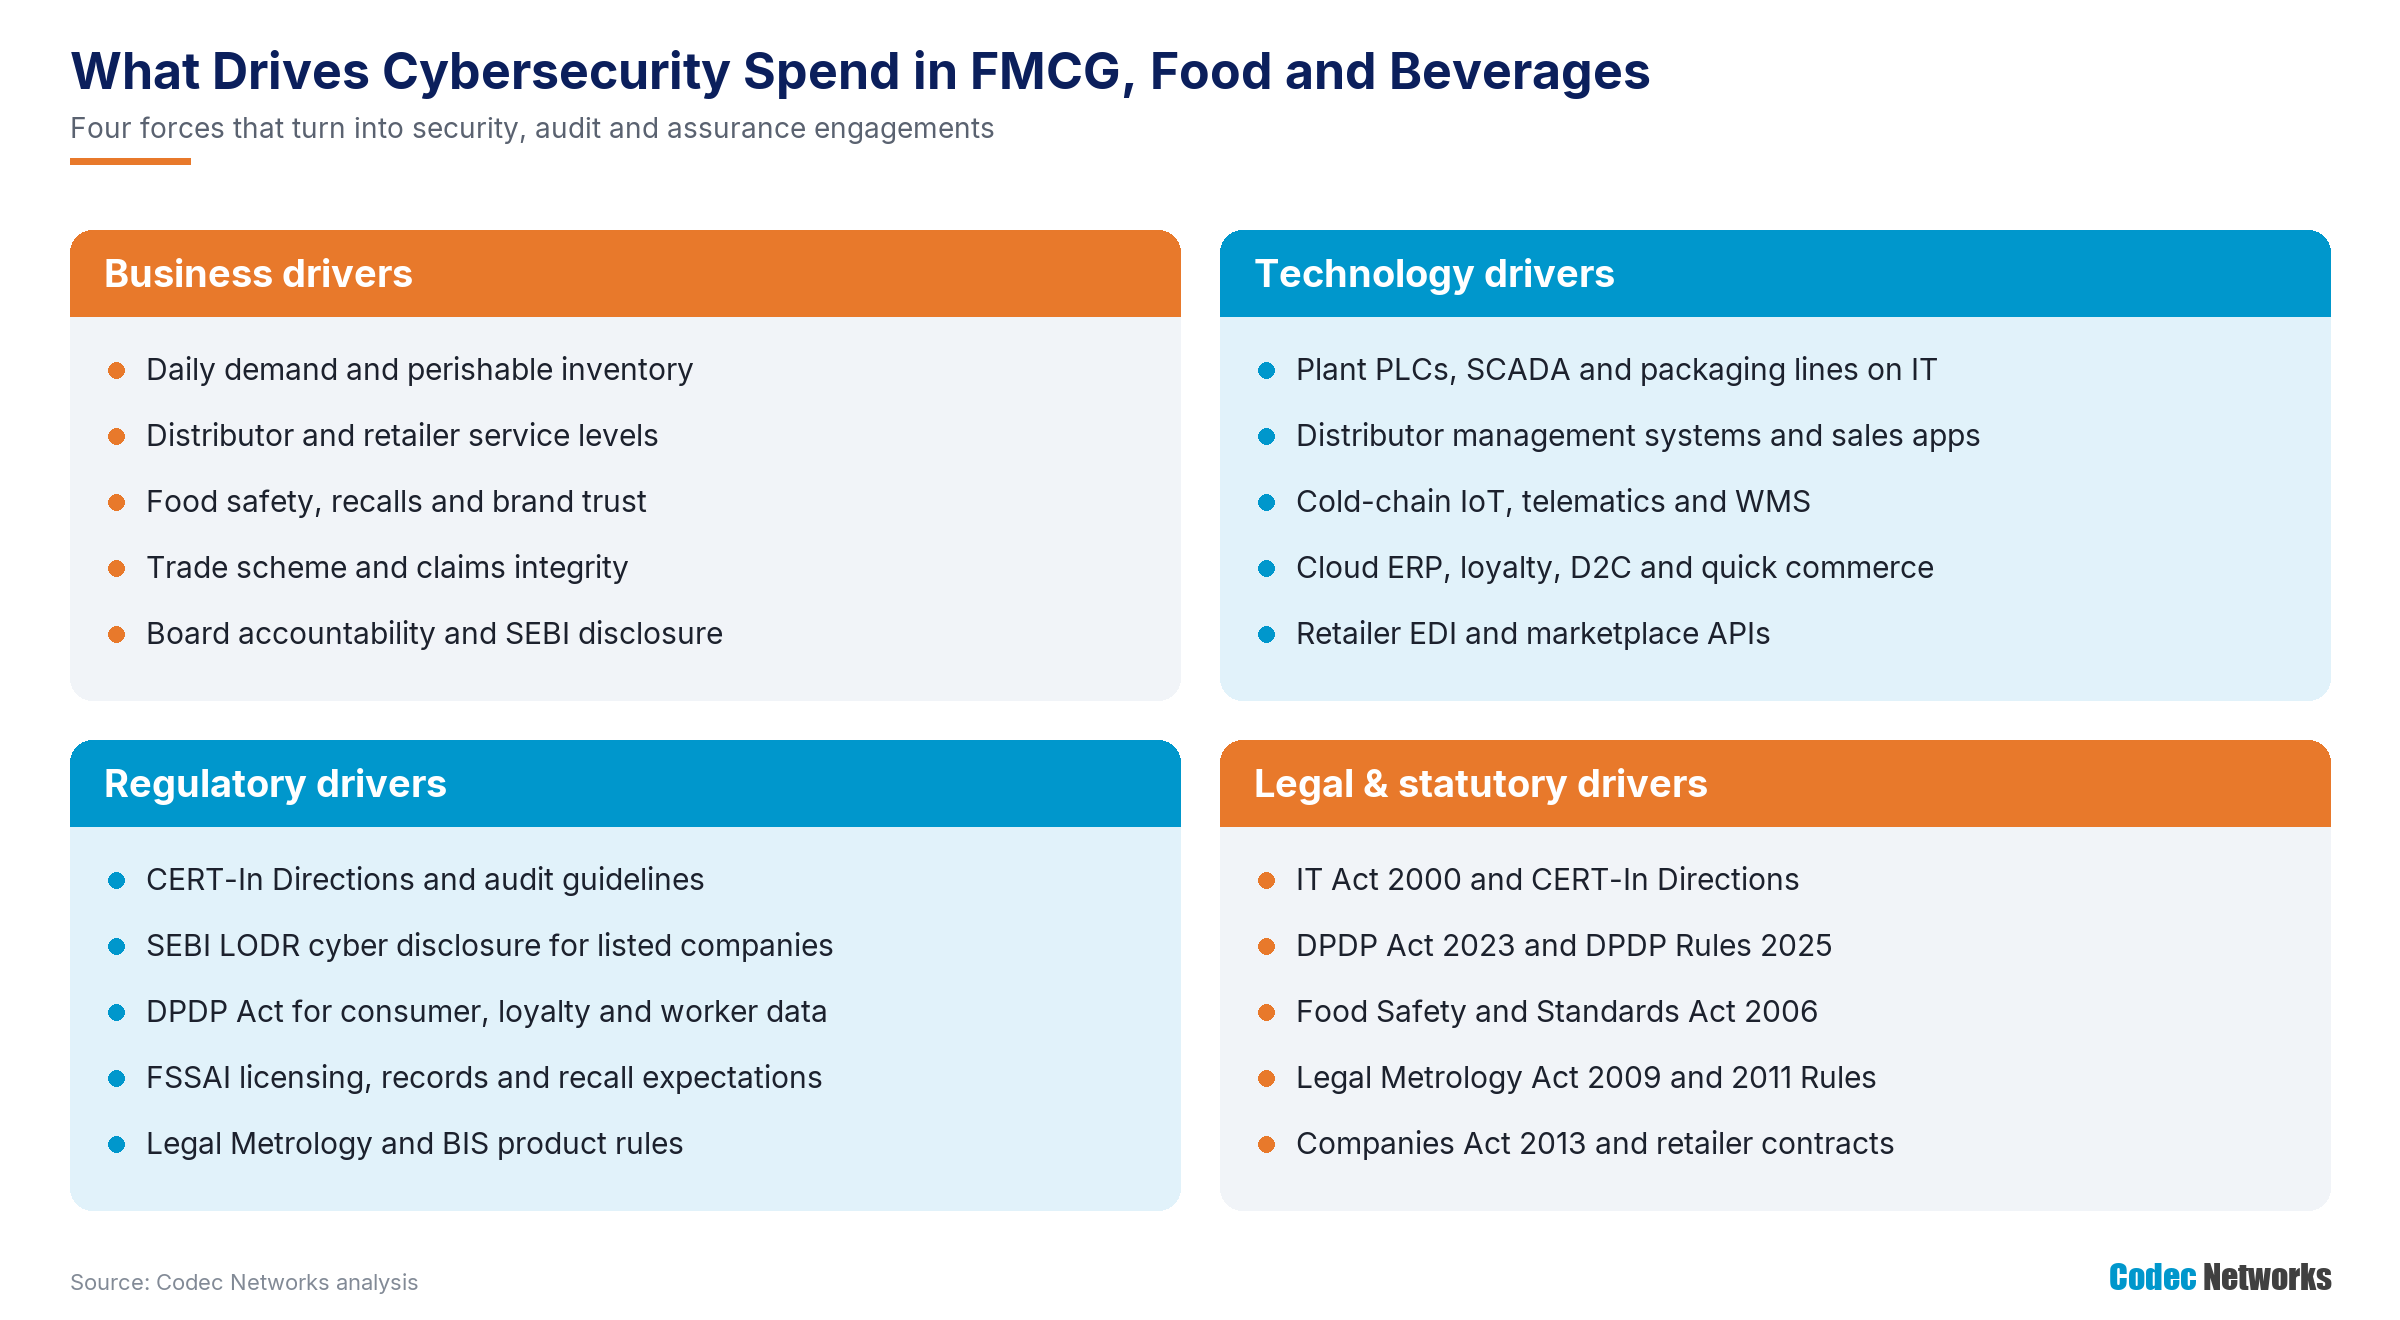
Figure 3: The four groups of drivers behind cybersecurity spending in FMCG, food and beverages.
4. Regulatory drivers: CERT-In, SEBI, DPDP, FSSAI, Legal Metrology and GST
|
Instrument |
Key requirements |
|
CERT-In Directions (2022) |
Six-hour incident reporting; 180-day ICT logs in India; applies to bodies corporate including manufacturers, distributors and platforms |
|
CERT-In audit policy guidelines (July 2025) |
Risk-based, independent cyber audits covering IT, OT/ICS, cloud and applications, with closure of findings |
|
SEBI LODR Regulations (listed companies) |
Quarterly disclosure of cyber incidents in the corporate governance report; Board oversight of risk |
|
DPDP Act 2023 and Rules 2025 |
Consumer, loyalty, distributor, farmer and worker data safeguards; most obligations from May 2027 |
|
Food Safety and Standards Act 2006 and FSSAI |
Licensing through FoSCoS, records, traceability and recalls—systems holding this evidence must be available and trustworthy |
|
Legal Metrology and GST |
Packaged Commodities Rules 2011 declarations; e-invoicing above ₹5 crore since August 2023; e-way bills |
|
Retailer, partner and payment requirements |
Modern trade and e-commerce security questionnaires and integration standards; PCI DSS v4.0.1 for D2C card payments; insurer conditions |
|
Confirm applicability Obligations depend on listing status, licences, products, channels and contracts. Confirm against the official instruments and your retailer and partner agreements. |
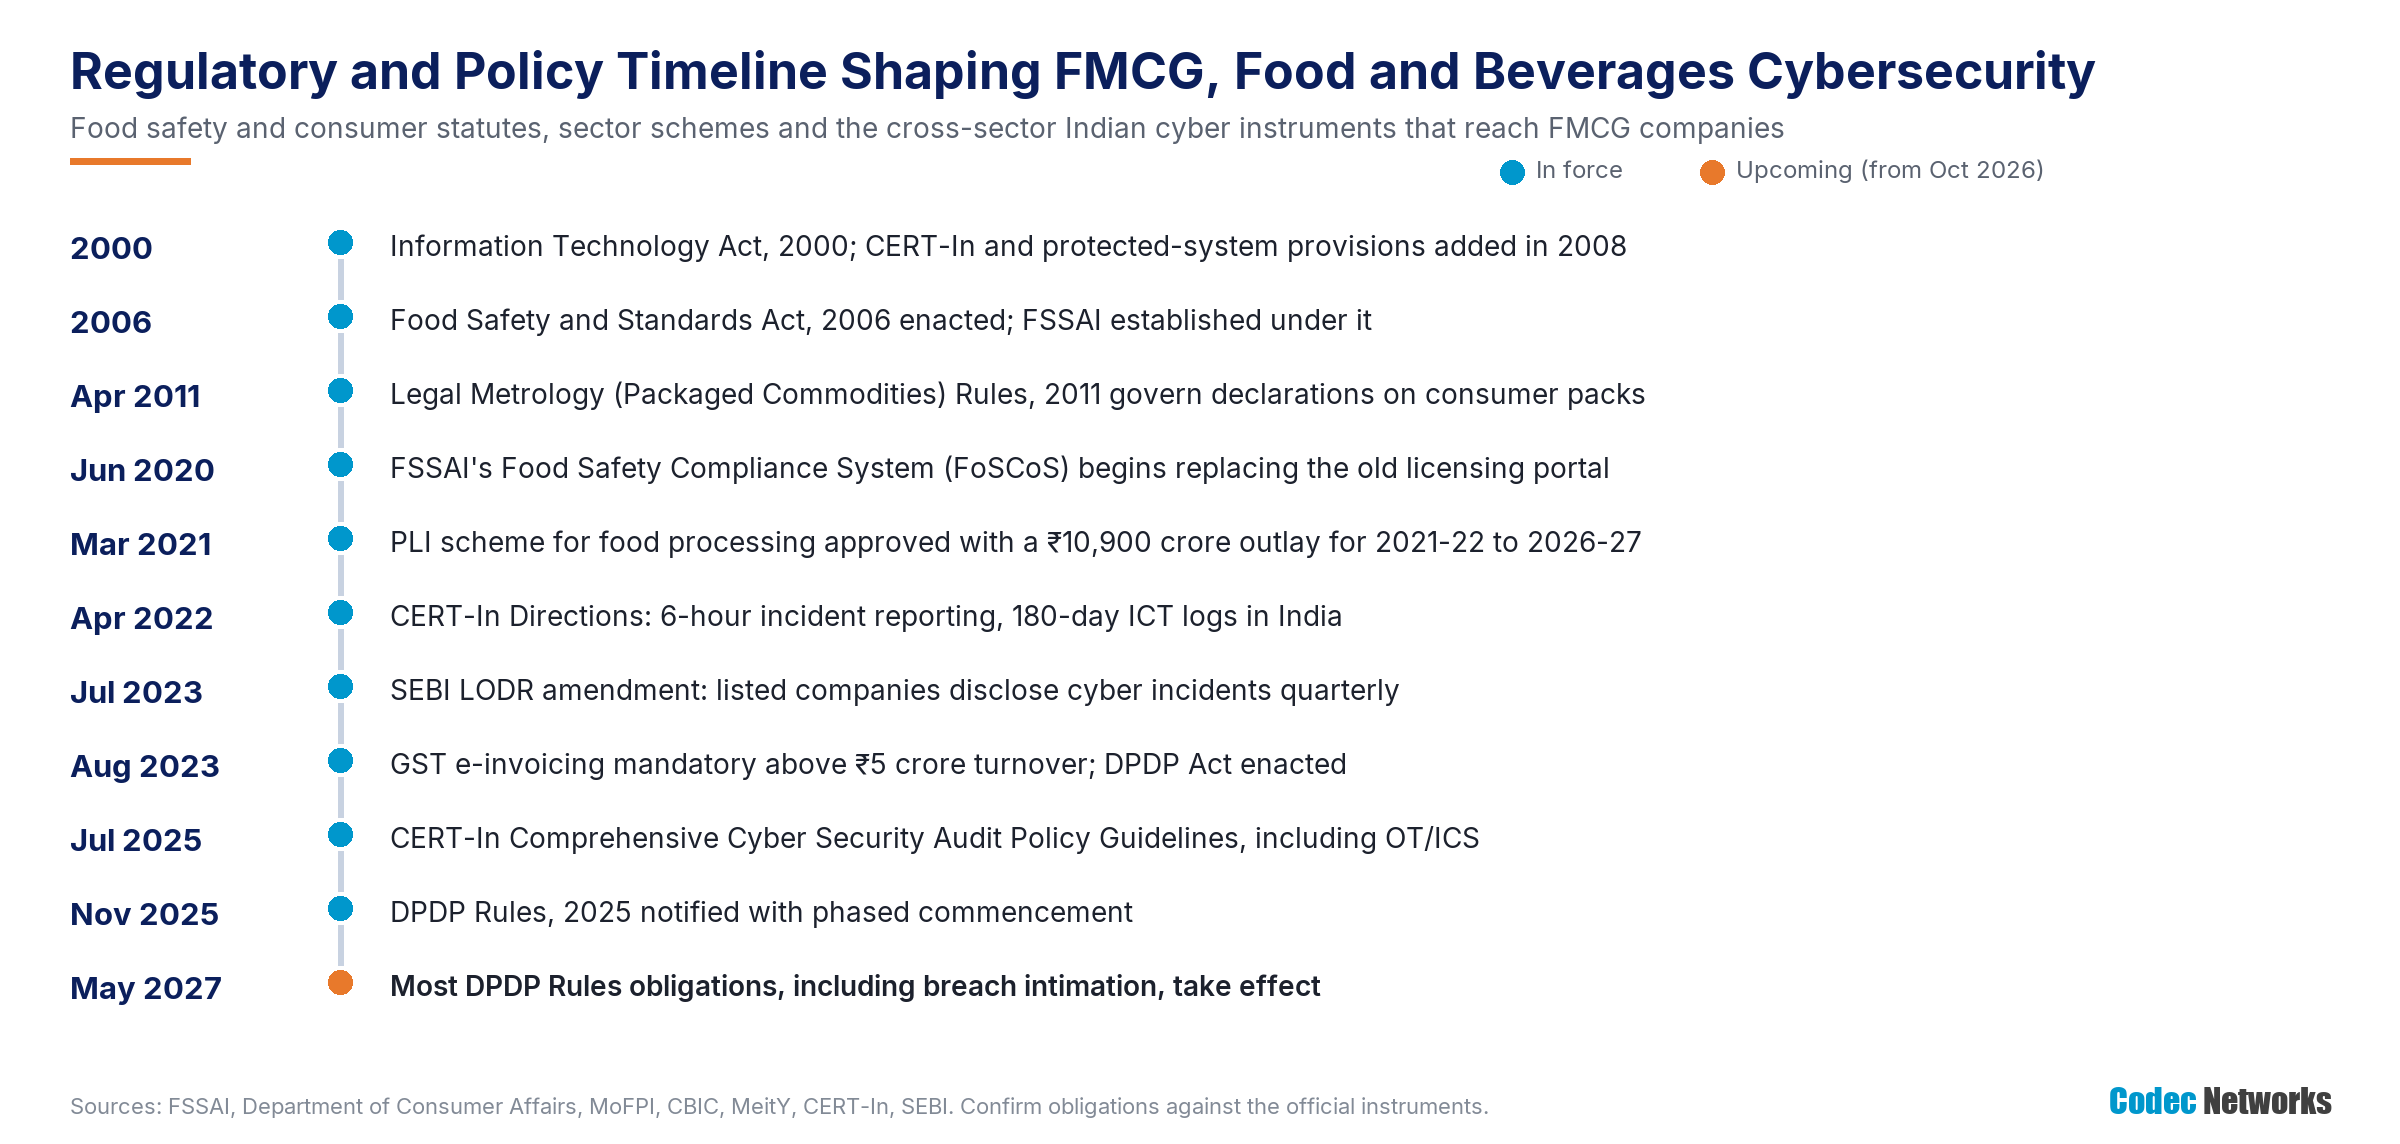
Figure 4: Regulatory and policy timeline shaping FMCG, food and beverages cybersecurity, as of October 2026.
5. Legal and statutory drivers
|
Law or obligation |
Relevance |
Demand created |
|
IT Act, 2000 and CERT-In Directions |
Incident reporting and logging |
SOC, logging, audits and incident response |
|
Companies Act, 2013 |
Board responsibility for risk management and internal controls |
Board risk reporting, audit programmes |
|
SEBI LODR Regulations |
Quarterly cyber incident disclosure for listed entities |
Incident records and disclosure support |
|
DPDP Act, 2023 and Rules, 2025 |
Personal data of consumers, distributors, farmers and workers |
Privacy programmes and breach workflows |
|
Food Safety and Standards Act, 2006 |
Licences, records, traceability and recalls |
Integrity of plant, lab and distribution records |
|
Legal Metrology Act, 2009 and GST law |
Pack declarations, e-invoicing and e-way bills |
Compliance system integrity and availability |
|
Retailer, partner and insurer contracts |
Security clauses, questionnaires, PCI DSS, warranties |
Independent testing, certifications, evidence packs |
6. How the drivers differ by company type
|
Company type |
Dominant business drivers |
Dominant technology drivers |
Principal regulatory drivers |
|
Consumer goods groups |
Shelf availability, disclosure, brand trust |
Group ERP, MES, DMS, loyalty |
CERT-In, SEBI LODR, DPDP, FSSAI |
|
Food processors |
Food safety, PLI growth, retailer programmes |
Process control, LIMS, co-packer links |
CERT-In, FSSAI, retailer requirements |
|
Beverage companies |
Route-to-market efficiency, scheme integrity |
Filling lines, bottler systems, DMS |
CERT-In, FSSAI, SEBI LODR (listed) |
|
Dairies and cooperatives |
Member payments, cold chain, trust |
Collection systems, pasteurisers, IoT |
CERT-In, FSSAI, DPDP |
|
Cold chain and distributors |
Customer service, cost control |
WMS, telematics, DMS, billing |
CERT-In, GST, principal contracts |
7. What this means for buyers and for Codec Networks
|
Customer buying need |
Recommended offering |
Natural recurring engagement |
|
“Would ransomware stop our dispatch to distributors?” |
Ransomware resilience review: dependency mapping, segmentation, backups, playbooks |
Annual resilience testing and exercises |
|
“Could someone game our trade schemes through the portal?” |
DMS, app and API testing with claims analytics |
Per-release testing and continuous analytics |
|
“Who can reach our plant lines and cold rooms from outside?” |
Plant OT and IoT assessment, remote access and segmentation review |
Vendor access recertification |
|
“Which co-packer or 3PL could stop our supply?” |
Supply chain assurance programme |
Per-partner assessments and renewals |
|
“Our loyalty app holds millions of consumers' data.” |
Mobile and API testing, DPDP programme |
Per-release testing and privacy reviews |
|
“We need 24x7 monitoring across plants and depots.” |
IT/OT SOC with fraud analytics |
Continuous monitoring |
|
“We need an independent cyber audit including OT.” |
CERT-In-aligned IT/OT audit |
Annual audits |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: This document is general industry guidance based on public information available as of October 2026. It is not legal, food safety or regulatory advice. Obligations differ by company size, listing status, products, licences, channels and markets; confirm them against the official CERT-In, MeitY, SEBI, FSSAI, Consumer Affairs and CBIC instruments and your retailer and partner contracts.