

Resources Categories
INDUSTRY FACT FILE · GOVERNMENT, PSUS & PUBLIC DIGITAL SERVICES
Applicable Cybersecurity Services and Codec Networks Bundles for Government and PSUs
How Codec Networks services and bundled service models help ministries, state governments, PSUs, data centres and government technology providers resolve their threats and meet CERT-In, NCIIPC, GIGW and DPDP expectations.
|
In this document 1. Our approach 2. Mapping threats to services 3. Codec Networks service catalogue for the sector 4. Codec Networks bundles for the sector 5. Sector programmes built from the bundles 6. Packages: Foundation, Assurance and Continuous Resilience 7. Regulatory requirement-to-bundle mapping 8. Threat-to-bundle coverage matrix 9. Delivery methodology and deliverables 10. Why Codec Networks 11. Annex: indicative commercial ranges |
1. Our approach
Public organisations need security that keeps services running and stands up to audit. Codec Networks works on four principles:
- Citizen first: every control is judged by what it does for the continuity of public services and the citizens whose data the organisation holds.
- Audit-ready by design: engagements follow CERT-In's guidelines and tender requirements, with evidence, closure tracking and reports that officials, auditors and legislators can rely on.
- Assume compromise: segment networks, protect backups, monitor around the clock and rehearse response so incidents stay contained and are reported on time.
- Prove it: findings mapped to CERT-In's guidelines and Directions, NCIIPC controls, GIGW 3.0, DPDP and ISO/IEC 27001.
2. Mapping threats to services
The table maps the 18 threats identified in Document 4 of this set to the Codec Networks services that help mitigate them.
|
Threat / challenge |
Applicable Codec Networks services |
Intended outcome |
|
Ransomware on hospital, ERP and e-governance servers |
Infrastructure VAPT, segmentation review, backup testing, managed SOC |
Services that keep running |
|
Spear-phishing and email compromise of officials |
Email security review, MFA, phishing simulation, mailbox monitoring |
Officials who are hard to fool |
|
State-linked espionage and APT intrusion |
Threat hunting, compromise assessment, EDR, forensics |
Intruders found and removed |
|
Website defacement and hacktivist campaigns |
External exposure scans, CMS hardening, defacement monitoring |
Public websites that stay intact |
|
DDoS against citizen portals |
DDoS readiness review, architecture and CDN guidance, monitoring |
Portals available at peak |
|
Citizen data exposure through portals and APIs |
Web, mobile and API VAPT, rate limiting, DPDP minimisation |
Citizen records that stay private |
|
Vendor and system integrator compromise |
Vendor audits, privileged access review, contract clauses |
Accountable vendors |
|
Unpatched legacy systems and orphan websites |
Asset inventory, exposure scans, decommissioning plans |
No forgotten front doors |
|
Cloud and data-centre misconfiguration |
Cloud and data-centre configuration reviews, tenant isolation |
No accidental exposure |
|
Flat networks and weak segmentation |
Network architecture review, zoning and access control |
Contained incidents |
|
Insider misuse of privileged access |
PAM review, activity monitoring, insider investigations |
Privileged access under control |
|
OT and plant network intrusion at PSUs |
OT assessment, IT–OT segmentation, remote-access review |
Safe and running plants |
|
Procurement, tender and payment fraud |
Process and control reviews, fraud investigations |
Clean tenders and payments |
|
Fake apps, websites and official impersonation |
Brand, domain and app-store monitoring, takedown support |
Fakes removed fast |
|
Remote access and VPN compromise |
Remote-access assessment, MFA, patch assurance |
A closed front door |
|
Insecure development and skipped audits |
Secure SDLC, code review, pre-hosting audits and retests |
Secure releases, not one-time audits |
|
Backup and recovery failure |
Backup review, offline copies, restore drills |
Proven recovery |
|
Weak detection and 6-hour reporting |
Managed SOC, playbooks, IR retainer |
Reliable 6-hour reporting |
3. Codec Networks service catalogue for the sector
|
Service line |
Sector-relevant services |
|
Security Vulnerability Assessment & Penetration Testing |
Department, PSU, data-centre and SWAN infrastructure assessments; external attack surface and orphan-website discovery; red teaming |
|
Application & platform security |
Citizen portal, mobile app and API security audits before hosting and after change; GIGW cybersecurity checks; secure SDLC for integrators |
|
Cloud & data-centre security |
MeitY-empanelled cloud configuration reviews, state data centre architecture, segmentation, privileged access and backup design |
|
Information security audit & compliance |
Audits against CERT-In's guidelines for government entities and 2025 audit policy; comprehensive and NCIIPC-aligned audits; closure tracking |
|
OT & plant security |
OT and SCADA assessments for PSU plants and utilities, IT–OT segmentation, remote-access review, IEC 62443 gap analysis |
|
Data privacy & protection |
DPDP programmes for citizen, beneficiary and employee data; data mapping; vendor and processor clauses; breach workflows |
|
GRC & ISO/IEC 27001 |
ISMS implementation and readiness, security policies, cyber crisis management plans, CISO support |
|
24/7 Managed SOC & threat monitoring |
Server, portal, email, cloud and vendor monitoring; defacement and DDoS alerts; threat hunting; 180-day log architecture |
|
Cyber forensics & incident response |
Ransomware response, compromise assessment, insider and fraud investigations, six-hour reporting and DPDP intimation support |
|
Awareness & simulation |
Phishing simulation for officials, awareness for staff, tabletop exercises for senior officials and crisis teams |
4. Codec Networks bundles for the sector
Eleven of the twelve bundles in the Codec Networks Bundled Service Models apply directly to government departments, PSUs and public digital service providers; the Global Cyber Back-Office SPV Program (Bundle 12) is offered separately for international clients.
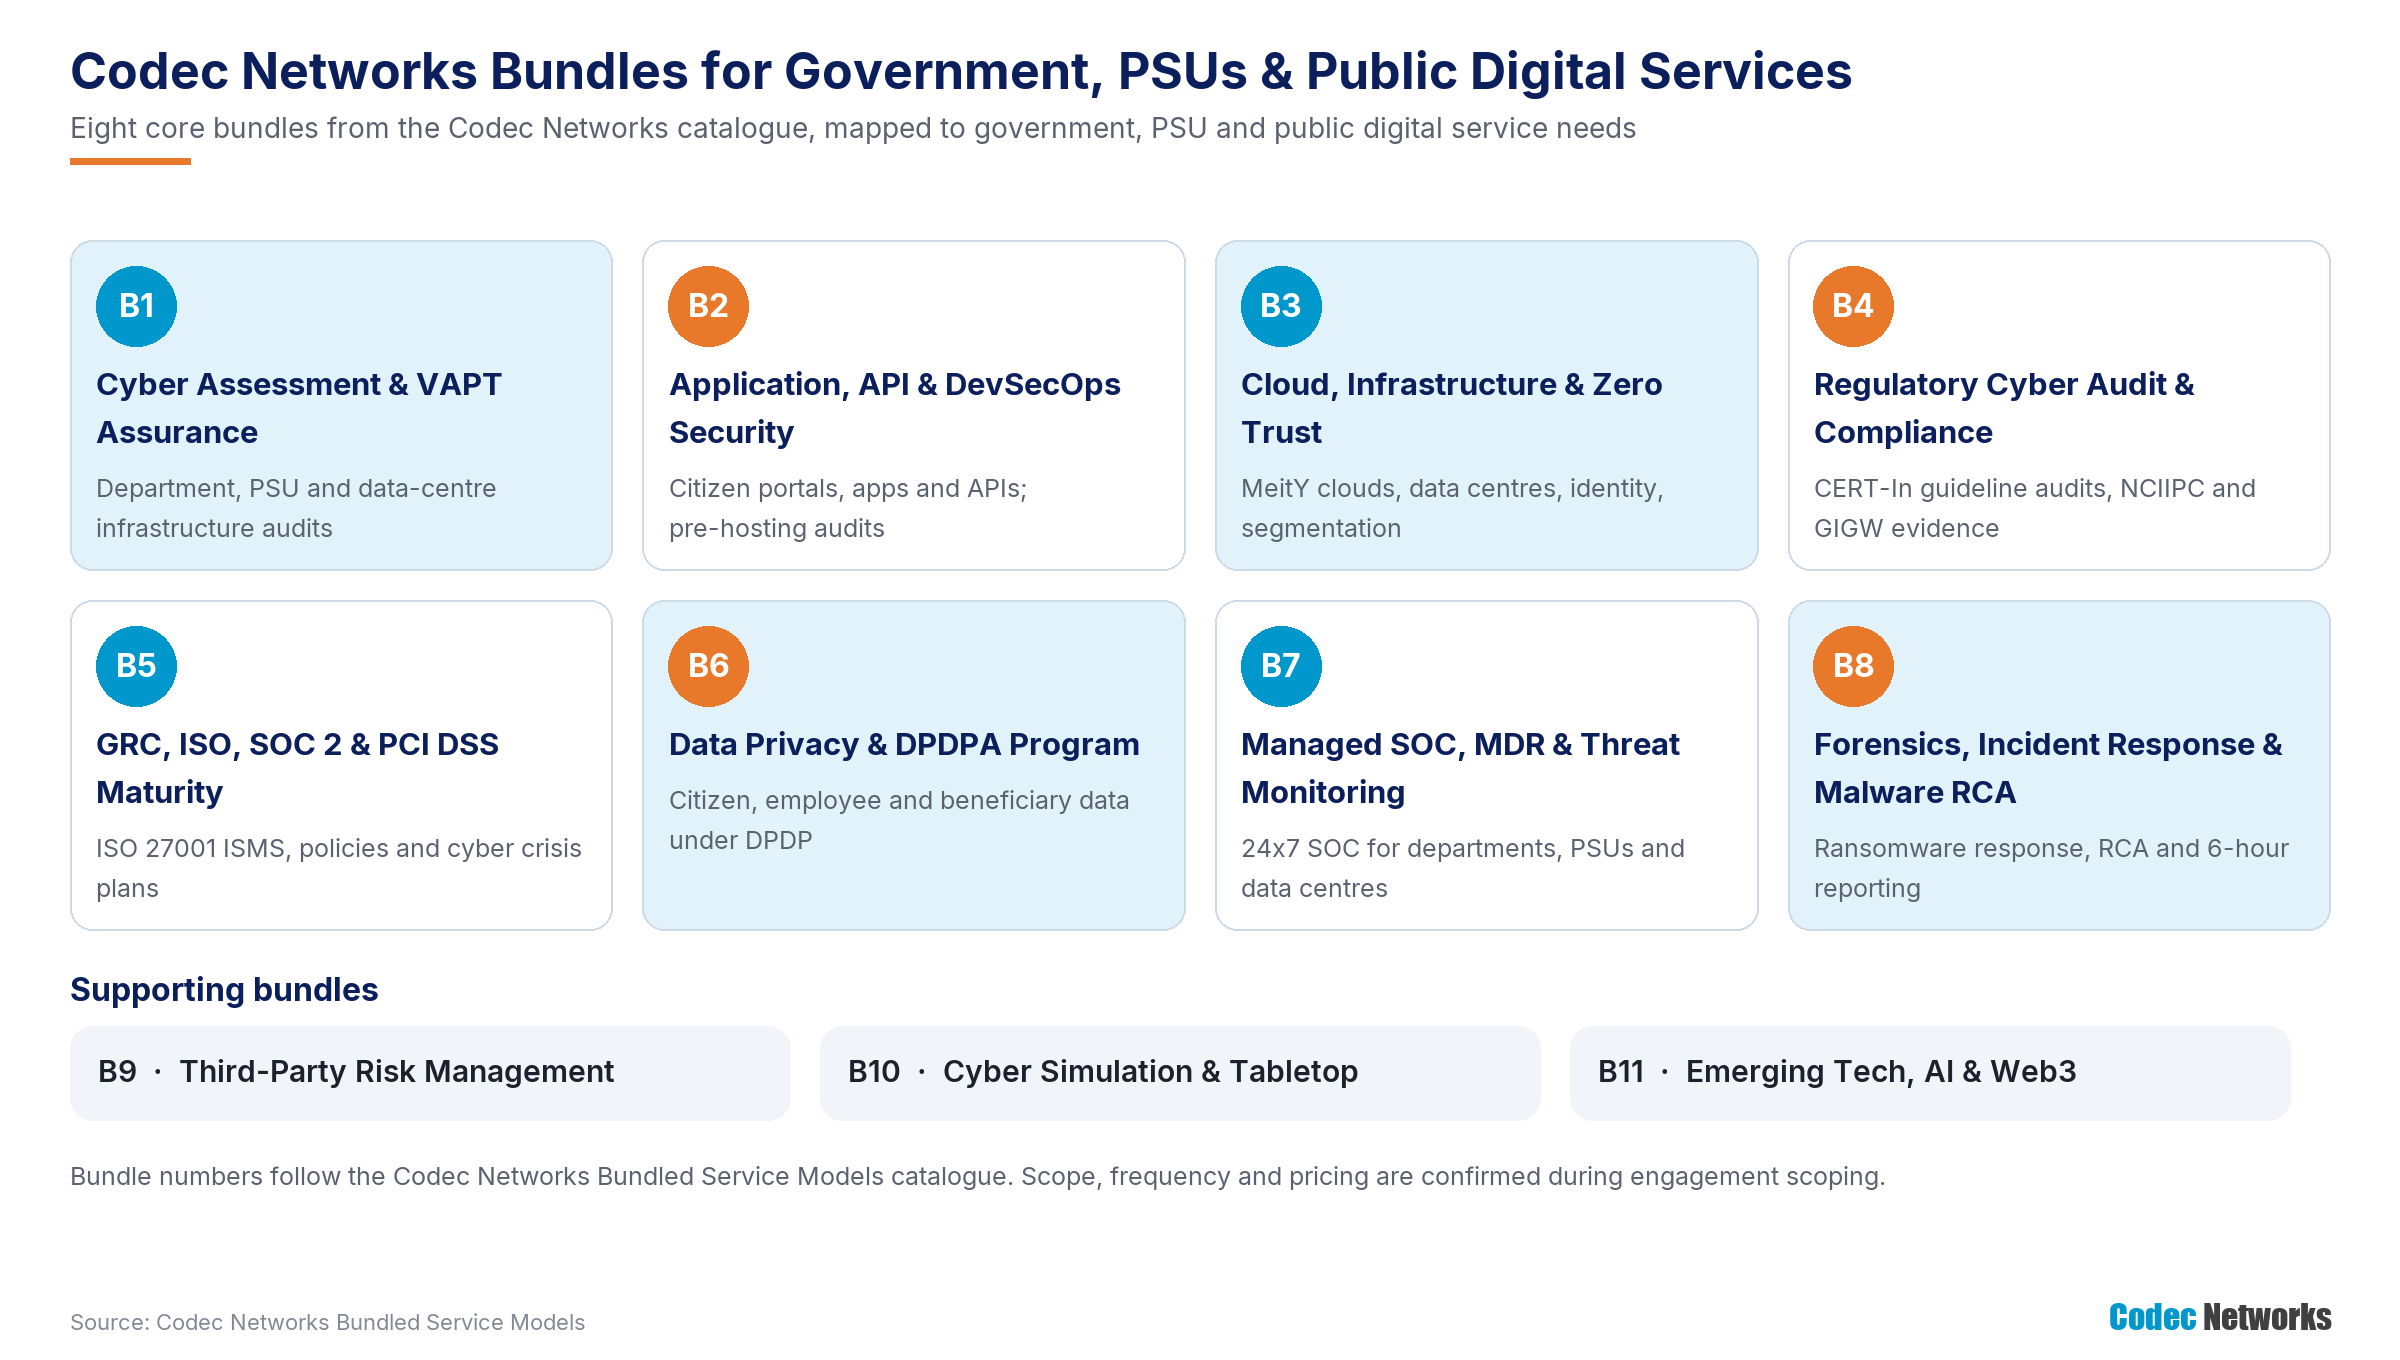
Figure 6: Codec Networks bundles applied to the sector.
|
Bundle |
Name |
Sector-relevant scope |
Best suited for |
Key deliverables |
|
B1 |
Cyber Assessment & VAPT Assurance Program |
Department, PSU, data-centre and network assessments; external surface and orphan sites |
All ministries, departments, PSUs and data centres |
Assessment reports, retests and closure tracker |
|
B2 |
Application, API & DevSecOps Security Program |
Citizen portals, mobile apps and APIs; pre-hosting audits; secure SDLC |
Citizen platforms, scheme departments, GovTech providers |
Application and API audit reports, retest certificates |
|
B3 |
Cloud, Infrastructure & Zero Trust Security Program |
MeitY clouds, state data centres, segmentation, identity and backup architecture |
Data centres, cloud-hosted departments, large PSUs |
Architecture review and remediation roadmap |
|
B4 |
Regulatory Cybersecurity Audit & Compliance Assurance Program |
Audits against CERT-In's 2023 guidelines and 2025 audit policy; NCIIPC-aligned and OT audits |
Every government entity and PSU on the audit cycle |
Audit report, gap matrix, evidence tracker |
|
B5 |
GRC, ISO, SOC 2 & Cyber Maturity Program |
ISO/IEC 27001 ISMS, policies, cyber crisis management plans, CISO support |
PSUs, data centres and departments seeking certification |
Maturity scorecard, policies, crisis plan |
|
B6 |
Data Privacy, DPDPA & Data Protection Program |
Citizen, beneficiary and employee data; State processing standards; vendor clauses |
Departments and PSUs ahead of May 2027 |
Privacy gap assessment, data map, roadmap |
|
B7 |
Managed SOC, MDR & Continuous Threat Monitoring Program |
24x7 SOC for servers, portals, email and cloud; defacement, DDoS and threat hunting |
Departments, PSUs and data centres of every size |
SOC reports, MTTD/MTTR, incident records |
|
B8 |
Digital Forensics, Incident Response & Malware RCA Program |
Ransomware response, compromise assessment, insider and fraud investigations |
Any entity facing an incident or CERT-In alert |
Forensic report, RCA, reporting support |
|
B9 |
Third-Party Risk Management & Supply Chain Cyber Risk Program |
System integrator, developer, AMC, hosting and cloud vendor assessments |
Departments and PSUs relying on outsourced IT |
Vendor risk register and audit reports |
|
B10 |
Cyber Simulation, Awareness, Tabletop & Crisis Readiness Program |
Phishing simulation for officials, tabletop and crisis exercises |
Senior officials, CISOs, IT and communication teams |
Exercise reports and playbooks |
|
B11 |
Emerging Technology, AI, Web3 & Future Security Program |
AI and analytics risk reviews for public data platforms |
Departments adopting AI and large data platforms |
Risk assessment and controls |
5. Sector programmes built from the bundles
Codec Networks packages the catalogue bundles into six government and PSU programmes.
|
Programme |
Built from bundles |
Challenges addressed |
|
Government Audit Cycle Programme |
B4, B1, B5 |
Six-monthly and annual audits, closure tracking, CISO support |
|
Citizen Platform Assurance Programme |
B2, B1, B6 |
Pre-hosting audits, API testing, retests, data minimisation |
|
Data Centre & Cloud Resilience |
B3, B1, B7 |
Segmentation, inventory, patching, backups, monitoring |
|
PSU Plant & OT Security |
B4, B3, B7 |
OT audits, IT–OT segmentation, remote access, monitoring |
|
Vendor & Integrator Assurance |
B9, B2, B4 |
Vendor audits, privileged access, contract clauses |
|
Managed SOC & Incident Readiness |
B7, B8, B10 |
Detection, response, six-hour reporting, exercises |
6. Packages: Foundation, Assurance and Continuous Resilience
|
Package element |
Foundation |
Assurance |
Continuous Resilience |
|
Typical organisation |
Departments, autonomous bodies and smaller PSUs |
State governments, large departments and PSUs |
Data centres, citizen platforms and strategic PSUs |
|
Testing |
B1 + B2: infrastructure VAPT and website and application audits |
B1 + B2: audit programme with portal, app and API testing |
B1 + B2 + B10: continuous testing and red teaming |
|
Audit and GRC |
B4: CERT-In guideline gap review |
B4: six-monthly and annual audits + B5 crisis plan |
B4 + B5 + B9: NCIIPC-aligned, OT and vendor audits, ISO 27001 |
|
Cloud, data and privacy |
B6: privacy quick assessment |
B3 + B6: data centre review and DPDP programme |
B3 + B6 + B11: architecture, DPDP and AI risk reviews |
|
Monitoring and response |
IR retainer (B8) |
B7: managed SOC + B8 |
B7: SOC with threat hunting and defacement monitoring + B8 |
|
Reporting |
Compliance checklist and audit responses |
CISO and senior management reporting |
Board, ministry, auditor and NCIIPC-ready reporting |
7. Regulatory requirement-to-bundle mapping
|
Requirement (source) |
How Codec Networks helps |
Bundle |
|
Cyber incidents to CERT-In within six hours; 180-day logs in India (CERT-In Directions, 2022) |
Managed SOC, log architecture, IR retainer and reporting support |
B7, B8 |
|
Nominated CISO and dedicated security team (CERT-In guidelines for government entities, 2023) |
CISO support, policies and crisis management plans |
B5, B4 |
|
Internal audits every six months and third-party audits at least yearly (CERT-In guidelines, 2023) |
Recurring audit programme by a CERT-In empanelled auditor |
B4, B1 |
|
Risk-based independent audits including OT (CERT-In audit guidelines, 2025) |
Comprehensive infrastructure, application and OT audits |
B4, B1 |
|
Controls for notified protected systems (IT Act Sections 70 and 70A; NCIIPC) |
NCIIPC-aligned control reviews, segmentation and monitoring |
B4, B3, B7 |
|
Cybersecurity of government websites and apps (GIGW 3.0) |
Pre-hosting application and mobile audits and retests |
B2, B1 |
|
Standards for processing of personal data by the State (DPDP Act and Rules) |
DPDPA programme, data maps, safeguards and breach workflows |
B6 |
|
Third-party access and outsourcing controls (CERT-In guidelines, 2023; contracts) |
Vendor audits, privileged access review and contract clauses |
B9, B3 |
|
Auditor eligibility and independence Government and PSU tenders for security audits commonly require bidders to hold current CERT-In empanelment, and CERT-In's 2023 guidelines for government entities note that CERT-In empanelled auditors may be used for third-party audits. Codec Networks is CERT-In empanelled for information security auditing services and empanelled with NICSI for application audit and compliance services (start-up category); it confirms eligibility and independence in each proposal. |
8. Threat-to-bundle coverage matrix
|
Threat / challenge |
Primary bundle |
Supporting bundles |
|
Ransomware on hospital, ERP and e-governance servers |
B3 |
B1, B7, B8 |
|
Spear-phishing and email compromise of officials |
B10 |
B3, B7 |
|
State-linked espionage and APT intrusion |
B7 |
B8, B1 |
|
Website defacement and hacktivist campaigns |
B1 |
B7, B2 |
|
DDoS against citizen portals |
B3 |
B7, B10 |
|
Citizen data exposure through portals and APIs |
B2 |
B6, B7 |
|
Vendor and system integrator compromise |
B9 |
B3, B7 |
|
Unpatched legacy systems and orphan websites |
B1 |
B7 |
|
Cloud and data-centre misconfiguration |
B3 |
B1, B4 |
|
Flat networks and weak segmentation |
B3 |
B1 |
|
Insider misuse of privileged access |
B7 |
B3, B8 |
|
OT and plant network intrusion at PSUs |
B4 |
B3, B7 |
|
Procurement, tender and payment fraud |
B8 |
B4, B10 |
|
Fake apps, websites and official impersonation |
B7 |
B2 |
|
Remote access and VPN compromise |
B1 |
B3, B7 |
|
Insecure development and skipped audits |
B2 |
B9 |
|
Backup and recovery failure |
B3 |
B10 |
|
Weak detection and 6-hour reporting |
B7 |
B8 |
“Primary” and “supporting” indicate suggested combinations, not guaranteed mitigation or complete coverage.
9. Delivery methodology and deliverables
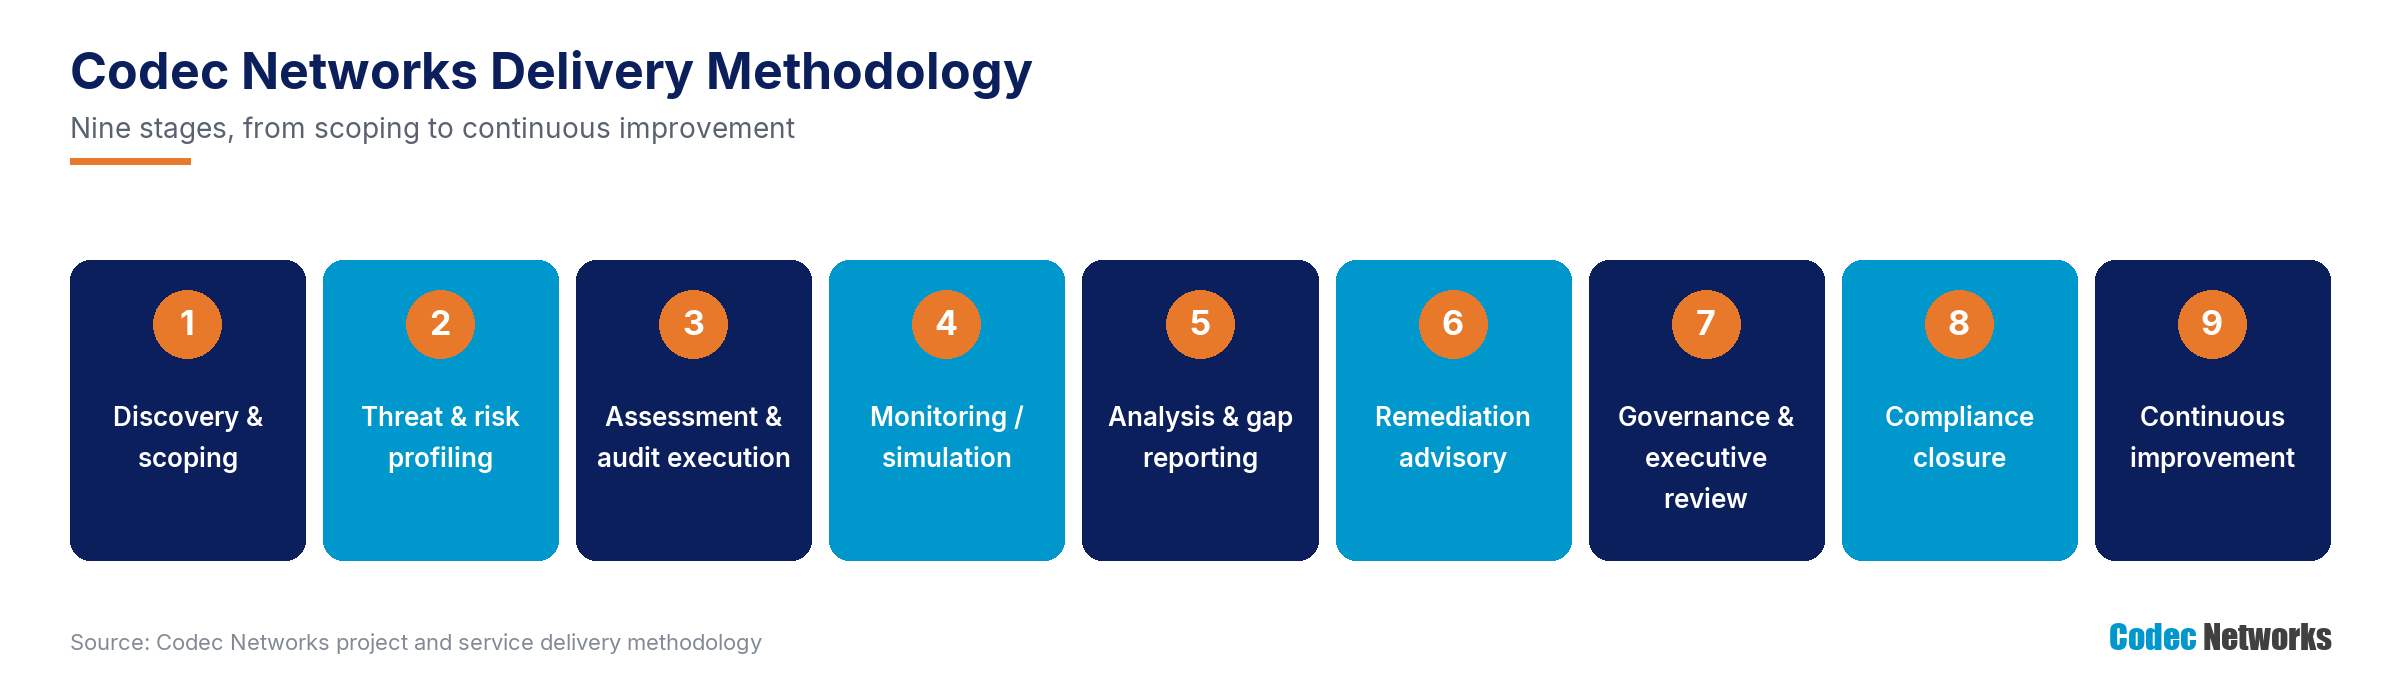
Figure 7: The Codec Networks delivery methodology.
Typical deliverables include infrastructure, network and external attack-surface assessment reports with retests, website, mobile app and API security audit reports with retest certificates before hosting, data centre and MeitY cloud configuration reviews, audit reports against CERT-In's guidelines for government entities and its 2025 audit policy with gap matrices and closure trackers, NCIIPC-aligned and OT assessment reports, a DPDP gap assessment with data map and vendor contract review, ISO 27001 readiness reports, cyber crisis management plans, vendor audit reports, forensic and root-cause reports with CERT-In reporting support, exercise reports and managed SOC reporting.
10. Why Codec Networks
- CERT-In empanelled for information security auditing services, and empanelled with NICSI for application audit and compliance services (start-up category).
- Certified to ISO 9001:2015, ISO/IEC 27001:2022 and ISO/IEC 20000-1:2018.
- Full stack: VAPT, regulatory audit, managed SOC, forensics, privacy and Board advisory from one partner, so findings, monitoring and closure stay connected.
- Public-sector depth: ministry, state, PSU, data-centre and platform environments assessed against CERT-In's guidelines for government entities, its Directions and 2025 audit policy, NCIIPC controls, GIGW 3.0, MeitY cloud terms, DPDP and ISO/IEC 27001, with reports written for officials, auditors and tender evaluation; Codec Networks serves central ministries, state governments and public-sector undertakings.
- Recognised frameworks and tools: OWASP ASVS/MASVS and API Top 10, MITRE ATT&CK, NIST CSF, ISO 27001 and PCI DSS; tools such as Burp Suite, Nessus, Metasploit, Prowler and leading SIEM/EDR platforms.
- Certified people: CEH, OSCP, CPENT, CISA, ISO 27001 LA/LI, CHFI, CTIA and ECIH professionals.
Annex: Indicative commercial ranges
For internal sales reference only—remove this annex before sharing externally. Ranges are taken from the Codec Networks Bundled Service Models and are subject to scoping, asset counts, frequency and service levels.
|
Bundle |
Package examples and indicative ranges |
|
B1 VAPT Assurance |
Essential ₹1.5–5 lakh; Professional ₹5–15 lakh; Enterprise ₹15–40 lakh; Annual retainer ₹25 lakh–₹1.5 crore |
|
B2 AppSec & DevSecOps |
API Quick Check ₹2–6 lakh; AppSec Professional ₹8–20 lakh; DevSecOps Maturity ₹12–35 lakh; Secure SDLC retainer ₹3–15 lakh/month |
|
B3 Cloud & Zero Trust |
Cloud Essential ₹3–8 lakh; Professional ₹8–25 lakh; Enterprise ₹25–75 lakh; Continuous assurance ₹2–10 lakh/month |
|
B4 Regulatory Audit |
Gap review ₹5–15 lakh; Full regulatory audit ₹15–50 lakh; Multi-framework audit ₹30 lakh–₹1.25 crore; Annual retainer ₹3–20 lakh/month |
|
B5 GRC, ISO, SOC 2 |
ISO readiness ₹5–15 lakh; ISO implementation ₹15–45 lakh; SOC 2 readiness ₹15–60 lakh; GRC retainer ₹2–12 lakh/month |
|
B6 Privacy & DPDPA |
Quick assessment ₹3–10 lakh; Implementation ₹10–40 lakh; DPO-as-a-Service ₹2–8 lakh/month; Privacy retainer ₹3–15 lakh/month |
|
B7 Managed SOC |
Starter ₹2–5 lakh/month; Professional ₹5–15 lakh/month; Enterprise ₹15–50 lakh/month; co-managed per FTE/shift |
|
B8 Forensics & IR |
Triage ₹3–15 lakh; Full investigation ₹15–75 lakh; Ransomware response ₹25 lakh–₹1.5 crore; IR retainer ₹5–50 lakh/year |
|
B9 TPRM |
₹25,000–₹2 lakh per vendor; batch pricing for 50–500 vendors; retainer ₹3–25 lakh/month |
|
B10 Simulation & Tabletop |
Awareness ₹1–5 lakh; Phishing simulation ₹2–10 lakh; Tabletop ₹5–20 lakh; Cyber war-game ₹15–75 lakh; Annual retainer ₹10 lakh–₹1 crore/year |
|
B11 Emerging Tech |
AI/LLM risk review ₹5–25 lakh; Smart contract audit ₹5–50 lakh; Emerging tech retainer ₹5–25 lakh/month |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: Service scope, deliverables, monitoring coverage and service levels are confirmed during engagement scoping. Services support risk reduction and assurance but do not guarantee prevention of all cyber incidents or regulatory compliance. Regulatory references are summaries; confirm against the official instruments applicable to each entity.