

Resources Categories
INDUSTRY FACT FILE · RAILWAYS, METRO & SURFACE TRANSPORT
Applicable Cybersecurity Services and Codec Networks Bundles for Rail and Surface Transport
How Codec Networks services and bundled service models help Indian Railways units, railway PSUs, metro corporations, state transport, tolling and transit technology companies resolve their threats and meet CERT-In, NCIIPC, safety-regulator, payment, SEBI and DPDP expectations.
|
In this document 1. Our approach 2. Mapping threats to services 3. Codec Networks service catalogue for the sector 4. Codec Networks bundles for the sector 5. Sector programmes built from the bundles 6. Packages: Foundation, Assurance and Continuous Resilience 7. Regulatory requirement-to-bundle mapping 8. Threat-to-bundle coverage matrix 9. Delivery methodology and deliverables 10. Why Codec Networks 11. Annex: indicative commercial ranges |
1. Our approach
Transport needs assurance that respects safety cases and public scale. Codec Networks works on four principles:
- Safety first: plan OT work with signalling, operations and safety teams; passive first, active only by agreement and never on live safety systems.
- Strong boundaries: IT/OT, station and supplier separation, brokered OEM access.
- Assume outage: map critical suppliers, keep offline fallbacks and rehearse degraded-mode operation and recovery.
- Prove it at scale: ticketing, fare and toll platforms tested for bots, fraud and abuse at launch-day volumes, mapped to PCI DSS, IEC 62443, ISO/IEC 27001 and CERT-In expectations.
2. Mapping threats to services
The table maps the 18 threats identified in Document 4 of this set to the Codec Networks services that help mitigate them.
|
Threat / challenge |
Applicable Codec Networks services |
Intended outcome |
|
Ransomware halting operations |
Segmentation, backup and restore testing, EDR validation |
Services that keep running and recover fast |
|
Signalling and control intrusion |
OT architecture assessment, segmentation, OEM access controls |
Protected safety layer |
|
Supplier and OEM remote access |
Remote access brokering, vendor assessments |
Controlled vendor access |
|
Supplier-hosted app outages |
Supplier criticality mapping, contractual recovery objectives, fallbacks |
Operations that continue without the vendor |
|
Ticketing bots and scalping |
Bot resistance testing, rate limiting, device attestation |
Fair, available booking |
|
API and app vulnerabilities |
API and mobile security testing, secure SDLC |
Hardened platforms |
|
Payment and tokenisation attacks |
Payment flow testing, PCI DSS readiness |
Protected payment flows |
|
Passenger data breaches |
DPDP programme, data mapping, access controls |
Protected passenger data |
|
False passenger information |
Communications security review, content and override controls |
Trustworthy displays and PA |
|
Radio, GPS and telecom interference |
Radio and telecom security review, monitoring |
Resilient communications |
|
Phishing |
Phishing simulation, MFA, awareness |
Fewer compromised accounts |
|
BEC |
Payment and master-data controls, BEC simulation |
Reduced fraud |
|
Flat IT/OT and station networks |
Zone-and-conduit design, station DMZ |
Contained networks |
|
Legacy signalling and SCADA |
Compensating controls, segmentation, monitoring |
Reduced exposure |
|
Fleet telematics and IoT exposure |
Fleet IoT and depot assessment |
Secured fleets |
|
Hacktivism and sabotage |
DDoS readiness, threat hunting, hardening |
Resilient public services |
|
Insider misuse |
Access reviews, activity monitoring, offboarding |
Accountable access |
|
Weak detection and recovery |
IT/OT SOC, playbooks, recovery drills |
Reliable 6-hour reporting |
3. Codec Networks service catalogue for the sector
|
Service line |
Sector-relevant services |
|
Security Vulnerability Assessment & Penetration Testing |
IT, station, depot and OCC assessments; signalling, Kavach, CBTC and SCADA reviews using safety-aware methods; ticketing, AFC and toll platform testing |
|
Application, API & mobile security |
PRS, UTS, IRCTC-style booking, AFC, NCMC, FASTag and bus ticketing apps and APIs; bot and fraud resistance; secure SDLC for transit technology providers |
|
Industrial & infrastructure security |
IT/OT architecture, zone-and-conduit segmentation, station DMZ, OEM remote access and IEC 62443-aligned gap assessments |
|
Communications security |
Train radio, telecom, passenger information, PA, CCTV and station Wi-Fi reviews |
|
Recovery & resilience |
Backup and restore testing; supplier criticality mapping; degraded-mode and recovery playbooks |
|
Information security audit & compliance |
CERT-In-aligned IT/OT audits, NCIIPC protected-system controls, ISO/IEC 27001, PCI DSS, SEBI disclosure support |
|
Third-party risk management |
OEM, integrator, app vendor, contractor and concession partner assessments; access governance |
|
Data privacy & protection |
DPDP programmes for passenger, commuter and employee data across apps, cards and CCTV |
|
24/7 Managed SOC & threat monitoring |
Stations, OCCs, enterprise IT and ticketing platforms monitored; supplier session monitoring; fraud analytics; threat hunting |
|
Cyber forensics, incident response & simulation |
Operational incident investigations, 6-hour reporting support, ransomware, signalling and crowd tabletops, joint exercises with suppliers |
4. Codec Networks bundles for the sector
Eleven of the twelve bundles in the Codec Networks Bundled Service Models apply directly to rail, metro and surface transport organisations; the Global Cyber Back-Office SPV Program (Bundle 12) is offered separately for international clients.
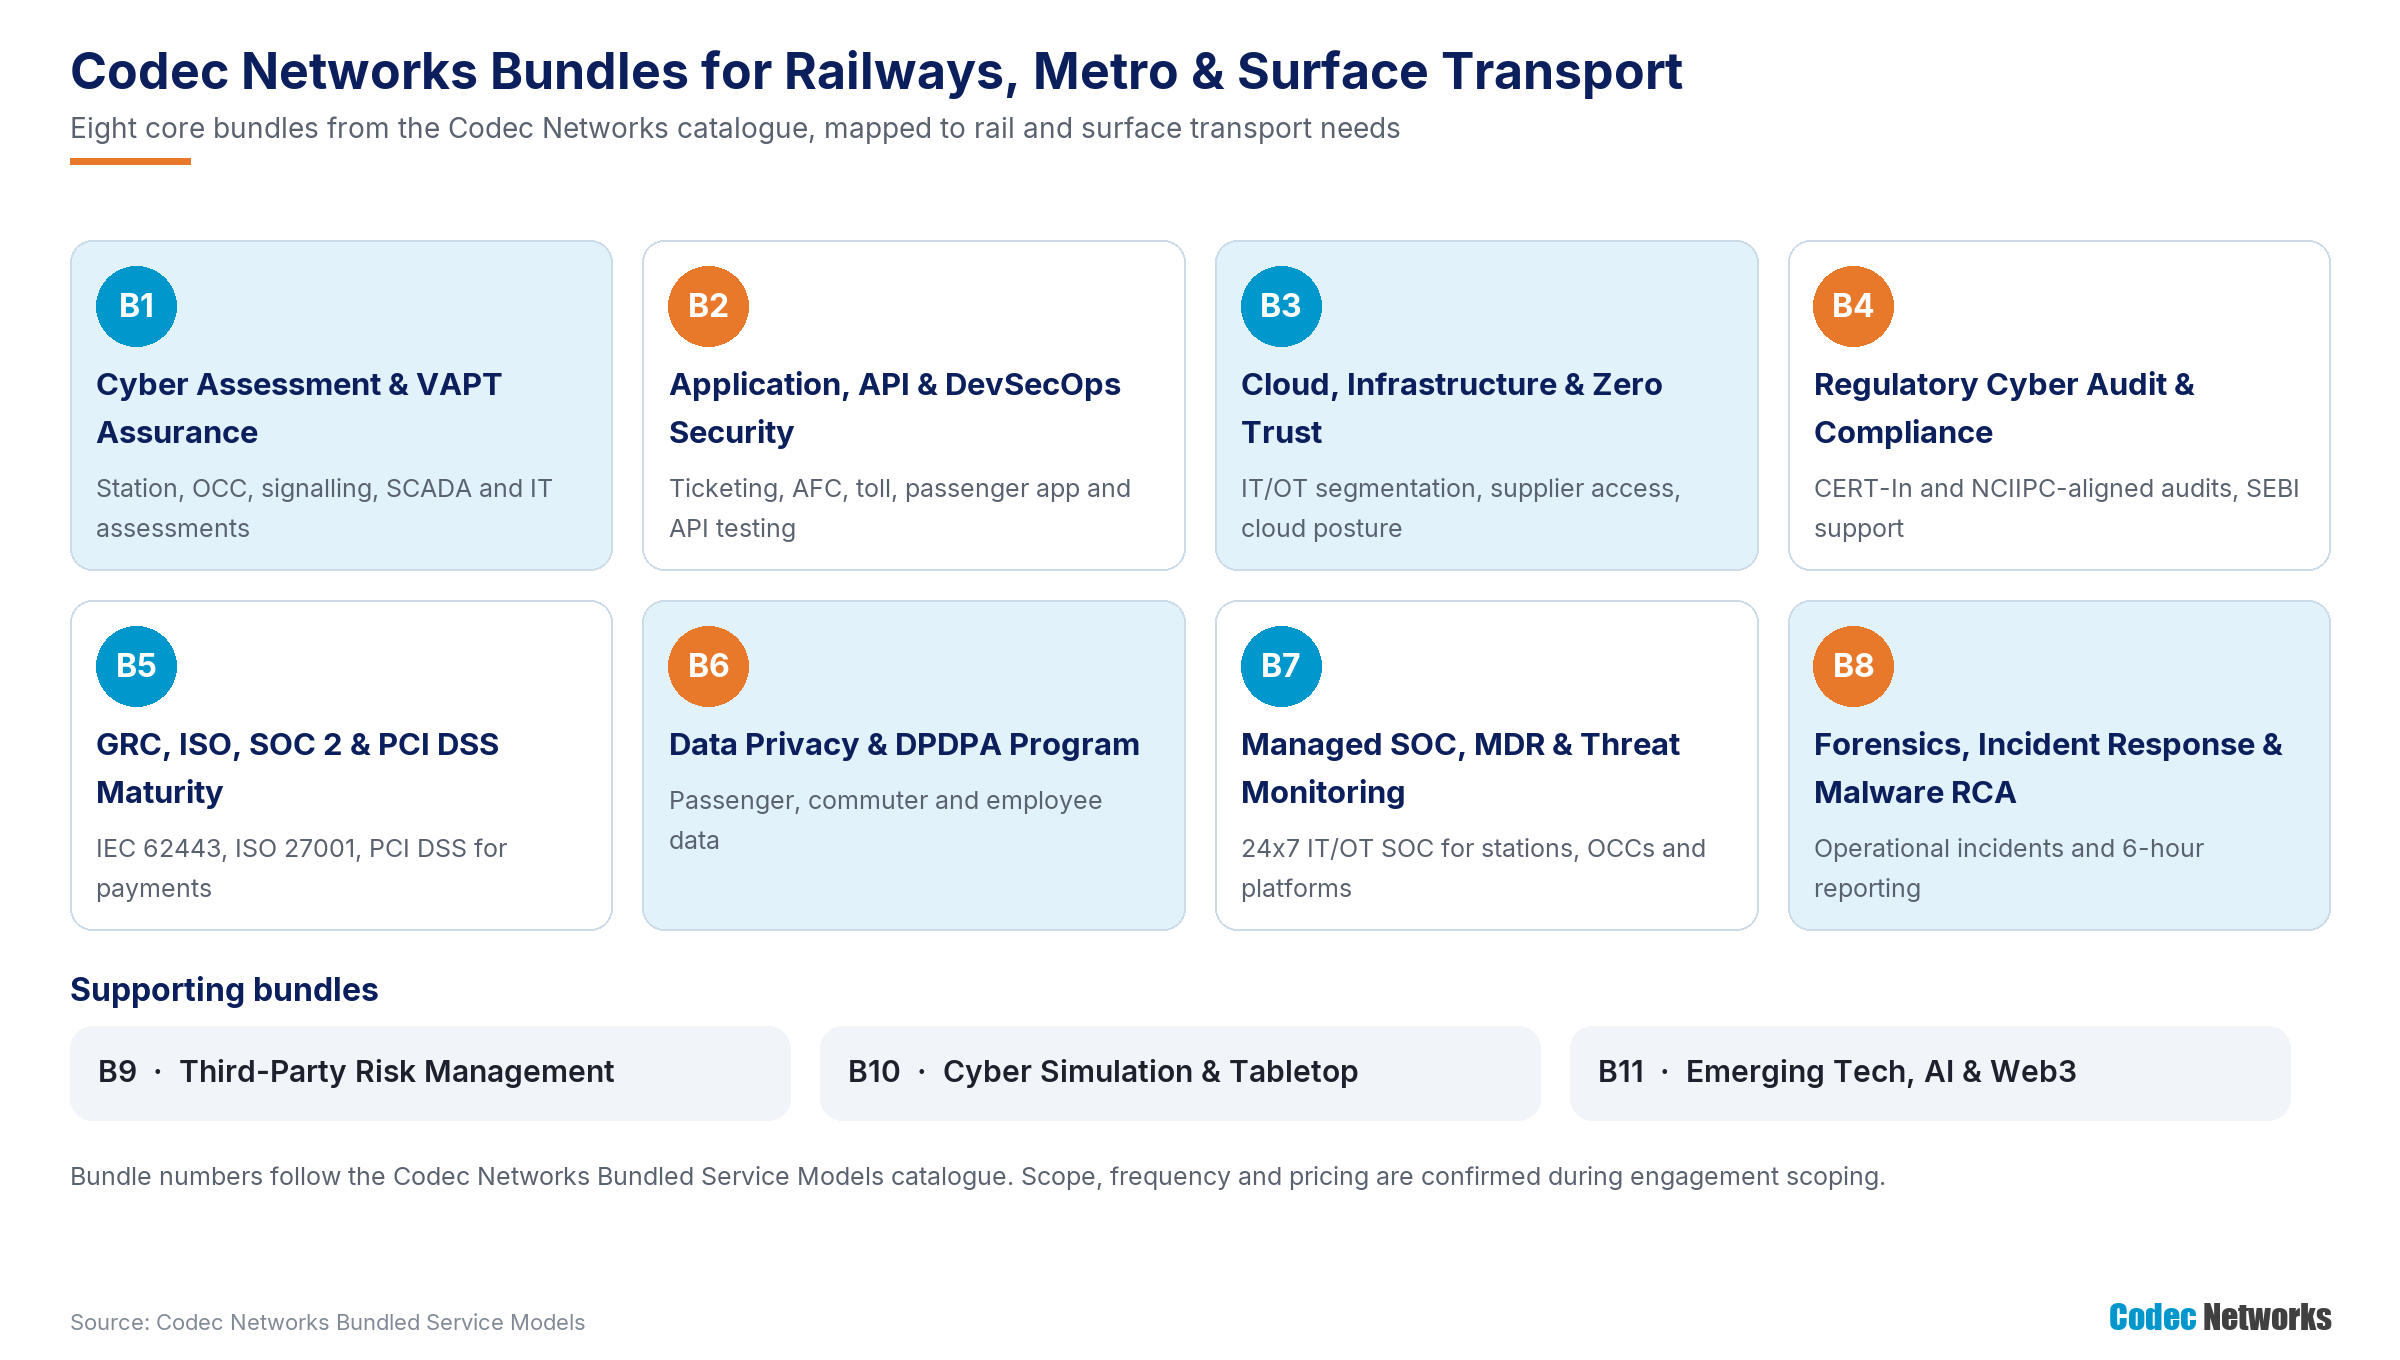
Figure 6: Codec Networks bundles applied to the sector.
|
Bundle |
Name |
Sector-relevant scope |
Best suited for |
Key deliverables |
|
B1 |
Cyber Assessment & VAPT Assurance Program |
IT, station, OCC, signalling, SCADA and ticketing assessments |
All operators |
Assessment reports, retests and closure tracker |
|
B2 |
Application, API & DevSecOps Security Program |
Ticketing, AFC, NCMC, toll and passenger app and API testing |
Railways, PSUs, metros, tolling and transit tech |
Application and API risk reports |
|
B3 |
Cloud, Infrastructure & Zero Trust Security Program |
IT/OT segmentation, station DMZ, OEM remote access, cloud posture |
All operators |
Architecture review and remediation roadmap |
|
B4 |
Regulatory Cybersecurity Audit & Compliance Assurance Program |
CERT-In and NCIIPC-aligned audits, SEBI support |
Indian Railways units, PSUs, corporations |
Audit report, gap matrix, evidence tracker |
|
B5 |
GRC, ISO, SOC 2 & Cyber Maturity Program |
IEC 62443, ISO 27001 and PCI DSS readiness |
Operators formalising OT and payment security |
Maturity scorecard, policies, evidence packs |
|
B6 |
Data Privacy, DPDPA & Data Protection Program |
Passenger, commuter and employee data protection |
PSUs, metros, platforms ahead of May 2027 |
Privacy gap assessment and roadmap |
|
B7 |
Managed SOC, MDR & Continuous Threat Monitoring Program |
24x7 IT/OT SOC with fraud analytics and threat hunting |
Multi-site operators and platforms |
SOC reports, MTTD/MTTR |
|
B8 |
Digital Forensics, Incident Response & Malware RCA Program |
Operational incident response and reporting |
Any operator facing an incident |
Forensic report, RCA, reporting support |
|
B9 |
Third-Party Risk Management & Supply Chain Cyber Risk Program |
OEM, integrator, app vendor and contractor assessments |
All operators |
Vendor risk register and assessments |
|
B10 |
Cyber Simulation, Awareness, Tabletop & Crisis Readiness Program |
Ransomware, signalling and crowd exercises and recovery drills |
Leadership, operations, suppliers |
Exercise reports and playbooks |
|
B11 |
Emerging Technology, AI, Web3 & Future Security Program |
AI-driven operations, analytics and digital twin security |
Operators adopting new technology programmes |
Risk assessment |
5. Sector programmes built from the bundles
Codec Networks packages the catalogue bundles into six rail and surface transport programmes.
|
Programme |
Built from bundles |
Challenges addressed |
|
Signalling & OT Security Programme |
B1, B3 |
Interlocking, Kavach, CBTC, OCC, segmentation and OEM access |
|
Ticketing & Payments Assurance |
B2, B5, B7 |
Bots, fraud, API flaws, PCI DSS and monitoring |
|
Communications & Station Security |
B1, B3 |
Radio, telecom, displays, PA, CCTV and station networks |
|
Supplier Resilience |
B9, B10, B3 |
Critical supplier mapping, access governance and joint exercises |
|
Passenger Data Protection |
B6, B2 |
DPDP across apps, cards and CCTV |
|
IT/OT SOC & Response |
B7, B8 |
Detection, response and 6-hour reporting |
6. Packages: Foundation, Assurance and Continuous Resilience
|
Package element |
Foundation |
Assurance |
Continuous Resilience |
|
Typical organisation |
State transport undertakings, concessionaires and transit tech start-ups |
Metro corporations, railway PSUs and tolling operators |
Indian Railways units, CII owners and multi-city operators |
|
Testing |
B1 + B2: ticketing and app assessment, IT and depot review |
B1 + B2: OT and signalling assessment, AFC and payment testing |
B1 + B2 + B10: continuous testing and red teaming |
|
Audit and GRC |
B5: policy, awareness and crisis plan pack |
B4: annual independent audit + B5 |
B4 + B5 + B9: audit, NCIIPC controls and supplier programme |
|
Cloud and privacy |
B3: backup and recovery review |
B3 + B6: segmentation and DPDP |
B3 + B6 + B11: segmentation, DPDP and new-technology security |
|
Monitoring and response |
IR retainer (B8) |
B7: IT/OT SOC + B8 |
B7: SOC with threat hunting + B8 |
|
Reporting |
Compliance checklist and partner evidence |
CISO and management reporting |
Board, regulator and NCIIPC reporting |
7. Regulatory requirement-to-bundle mapping
|
Requirement (source) |
How Codec Networks helps |
Bundle |
|
Cyber incidents to CERT-In within six hours; 180-day logs (CERT-In Directions) |
IT/OT SOC, IR retainer and reporting support |
B7, B8 |
|
Risk-based independent cyber audits including OT/ICS (CERT-In audit guidelines, 2025) |
Independent IT/OT audits |
B4, B1 |
|
Protection of notified protected systems and CII (NCIIPC, IT Act s.70A) |
CII-aligned assessments and controls |
B4, B3 |
|
Safety certification of signalling and control (Railways Act, CRS; Metro Railways Act, CMRS) |
Signalling and OT security reviews, cyber in safety management |
B1, B5 |
|
Public service vehicle tracking and emergency buttons (MoRTH, AIS 140) |
Fleet IoT and monitoring centre security |
B1, B3 |
|
Card tokenisation, NETC and NCMC scheme rules, PCI DSS (RBI, NPCI) |
Payment flow testing and PCI DSS readiness |
B2, B5 |
|
Quarterly cyber incident disclosure by listed PSUs (SEBI LODR) |
Incident records and disclosure support |
B4, B8 |
|
Passenger, commuter and employee personal data (DPDP) |
DPDPA programme |
B6 |
|
Operator and partner contracts (IRCTC partners, concessions, OEMs) |
Questionnaire readiness, evidence packs, supplier assessments |
B5, B9 |
|
Auditor eligibility and independence Where a regulator, standard or contract requires CERT-In empanelled or independent auditors, Codec Networks—CERT-In empanelled for information security auditing services—confirms eligibility and independence in each proposal. |
8. Threat-to-bundle coverage matrix
|
Threat / challenge |
Primary bundle |
Supporting bundles |
|
Ransomware halting operations |
B3 |
B7, B10, B8 |
|
Signalling and control intrusion |
B1 |
B3, B7 |
|
Supplier and OEM access |
B9 |
B3, B7 |
|
Supplier-hosted app outages |
B9 |
B10, B3 |
|
Ticketing bots and scalping |
B2 |
B7 |
|
API and app vulnerabilities |
B2 |
B1 |
|
Payment and tokenisation attacks |
B2 |
B5, B7 |
|
Passenger data breaches |
B6 |
B2, B3 |
|
False passenger information |
B3 |
B1, B10 |
|
Radio, GPS and telecom interference |
B1 |
B7 |
|
Phishing |
B10 |
B7 |
|
BEC |
B10 |
B2, B7 |
|
Flat IT/OT and station networks |
B3 |
B1 |
|
Legacy signalling and SCADA |
B3 |
B1, B7 |
|
Fleet telematics and IoT exposure |
B1 |
B3, B11 |
|
Hacktivism and sabotage |
B7 |
B3 |
|
Insider misuse |
B7 |
B3 |
|
Weak detection and recovery |
B7 |
B8, B10 |
“Primary” and “supporting” indicate suggested combinations, not guaranteed mitigation or complete coverage.
9. Delivery methodology and deliverables
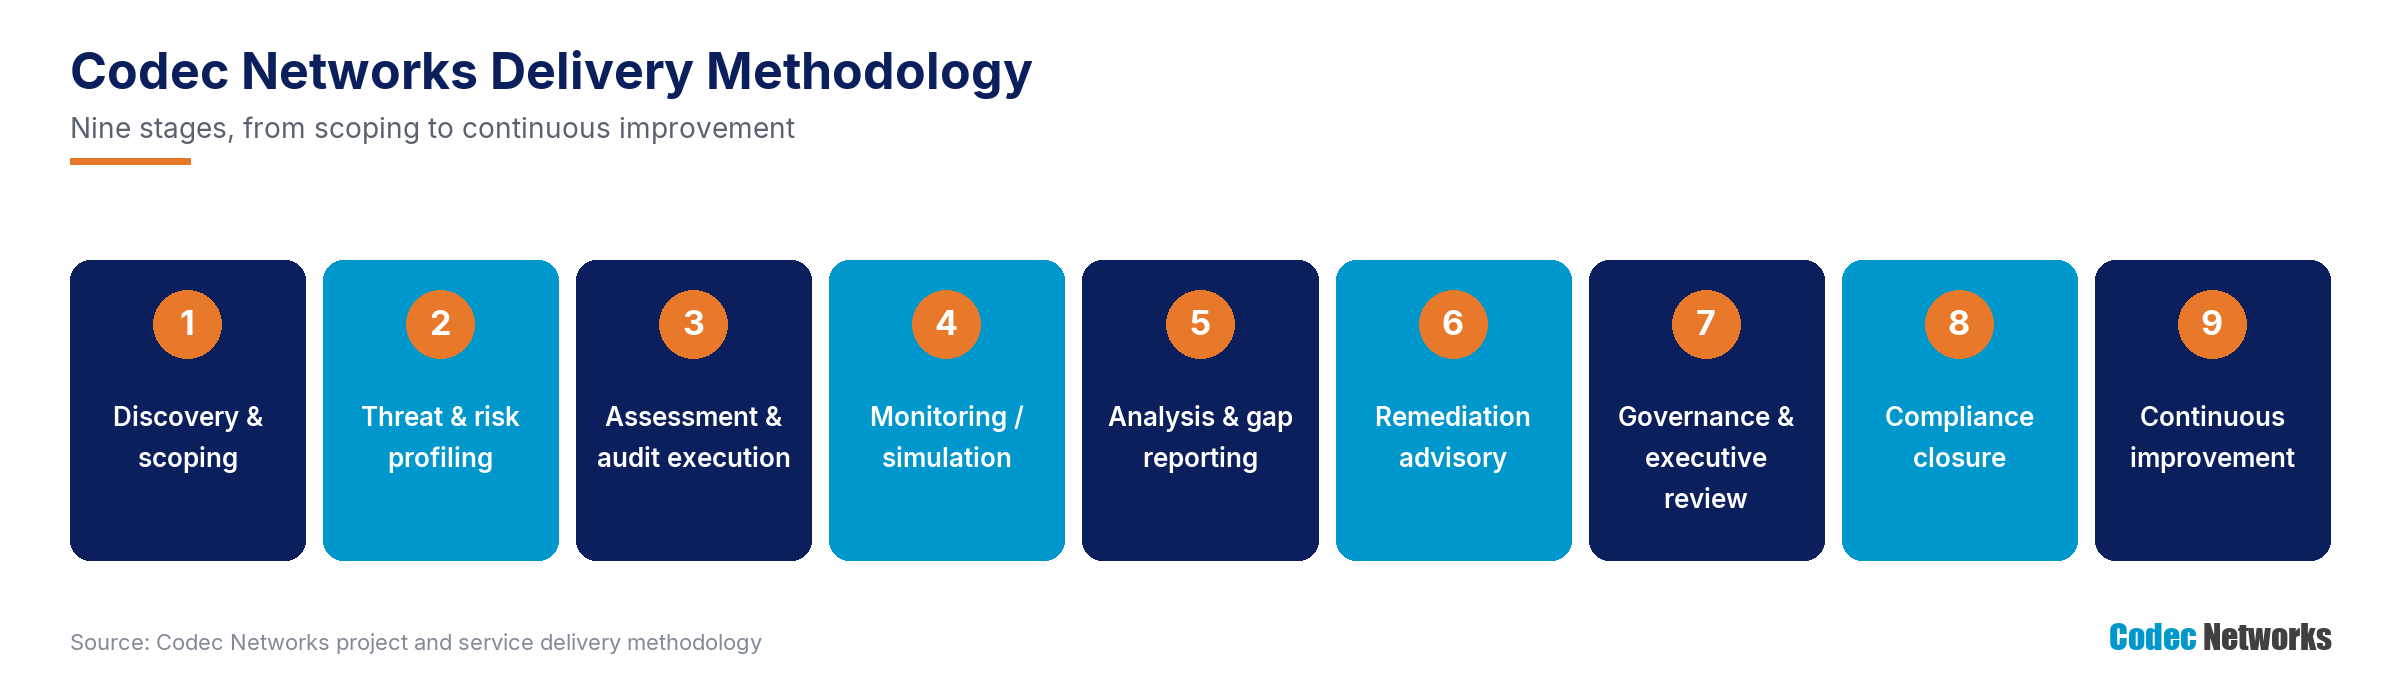
Figure 7: The Codec Networks delivery methodology.
Typical deliverables include IT/OT and IEC 62443 assessment reports with retests, a zone-and-conduit segmentation design for stations and control centres, ticketing, AFC and toll platform and API test reports with bot and fraud findings, a communications and station network review, a supplier criticality map and third-party programme, backup and degraded-mode recovery reviews, a CERT-In-aligned audit report, NCIIPC protected-system evidence, a DPDP gap assessment, exercise reports and playbooks, and IT/OT SOC reporting.
10. Why Codec Networks
- CERT-In empanelled for information security auditing services, and empanelled with NICSI for application audit and compliance services (start-up category).
- Certified to ISO 9001:2015, ISO/IEC 27001:2022 and ISO/IEC 20000-1:2018.
- Full stack: VAPT, regulatory audit, managed SOC, forensics, privacy and Board advisory from one partner, so findings, monitoring and closure stay connected.
- Transport depth: signalling, Kavach, CBTC, OCCs, station networks, ticketing, AFC and toll platforms assessed with safety-aware methods and mapped to IEC 62443, PCI DSS and CERT-In expectations.
- Recognised frameworks and tools: OWASP ASVS/MASVS and API Top 10, MITRE ATT&CK, NIST CSF, ISO 27001 and PCI DSS; tools such as Burp Suite, Nessus, Metasploit, Prowler and leading SIEM/EDR platforms.
- Certified people: CEH, OSCP, CPENT, CISA, ISO 27001 LA/LI, CHFI, CTIA and ECIH professionals.
Annex: Indicative commercial ranges
For internal sales reference only—remove this annex before sharing externally. Ranges are taken from the Codec Networks Bundled Service Models and are subject to scoping, asset counts, frequency and service levels.
|
Bundle |
Package examples and indicative ranges |
|
B1 VAPT Assurance |
Essential ₹1.5–5 lakh; Professional ₹5–15 lakh; Enterprise ₹15–40 lakh; Annual retainer ₹25 lakh–₹1.5 crore |
|
B2 AppSec & DevSecOps |
API Quick Check ₹2–6 lakh; AppSec Professional ₹8–20 lakh; DevSecOps Maturity ₹12–35 lakh; Secure SDLC retainer ₹3–15 lakh/month |
|
B3 Cloud & Zero Trust |
Cloud Essential ₹3–8 lakh; Professional ₹8–25 lakh; Enterprise ₹25–75 lakh; Continuous assurance ₹2–10 lakh/month |
|
B4 Regulatory Audit |
Gap review ₹5–15 lakh; Full regulatory audit ₹15–50 lakh; Multi-framework audit ₹30 lakh–₹1.25 crore; Annual retainer ₹3–20 lakh/month |
|
B5 GRC, ISO, SOC 2 |
ISO readiness ₹5–15 lakh; ISO implementation ₹15–45 lakh; SOC 2 readiness ₹15–60 lakh; GRC retainer ₹2–12 lakh/month |
|
B6 Privacy & DPDPA |
Quick assessment ₹3–10 lakh; Implementation ₹10–40 lakh; DPO-as-a-Service ₹2–8 lakh/month; Privacy retainer ₹3–15 lakh/month |
|
B7 Managed SOC |
Starter ₹2–5 lakh/month; Professional ₹5–15 lakh/month; Enterprise ₹15–50 lakh/month; co-managed per FTE/shift |
|
B8 Forensics & IR |
Triage ₹3–15 lakh; Full investigation ₹15–75 lakh; Ransomware response ₹25 lakh–₹1.5 crore; IR retainer ₹5–50 lakh/year |
|
B9 TPRM |
₹25,000–₹2 lakh per vendor; batch pricing for 50–500 vendors; retainer ₹3–25 lakh/month |
|
B10 Simulation & Tabletop |
Awareness ₹1–5 lakh; Phishing simulation ₹2–10 lakh; Tabletop ₹5–20 lakh; Cyber war-game ₹15–75 lakh; Annual retainer ₹10 lakh–₹1 crore/year |
|
B11 Emerging Tech |
AI/LLM risk review ₹5–25 lakh; Smart contract audit ₹5–50 lakh; Emerging tech retainer ₹5–25 lakh/month |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: Service scope, deliverables, monitoring coverage and service levels are confirmed during engagement scoping. Services support risk reduction and assurance but do not guarantee prevention of all cyber incidents or regulatory compliance. Regulatory references are summaries; confirm against the official instruments applicable to each entity.