

Resources Categories
INDUSTRY FACT FILE · RENEWABLE ENERGY & ENERGY STORAGE
Market Landscape and the Drivers of Cybersecurity Demand in Renewables
The business, technology, regulatory, legal and statutory forces that create cybersecurity, audit and assurance work for renewable, storage and metering operators.
|
In this document 1. Market landscape 2. Business drivers 3. Technology drivers 4. Regulatory drivers: CEA Regulations 2026, CERT-In and DPDP 5. Legal and statutory drivers 6. How the drivers differ by player type 7. What this means for buyers and for Codec Networks |
1. Market landscape
India's renewable sector is led by large independent power producers, public-sector companies and developers building solar, wind, hybrid and storage capacity, supported by O&M firms, asset managers and smart metering providers. Growth depends on global OEM equipment and remote operations—and from April 2027, portfolios of 50 MW and above face binding CEA cyber regulations, as reported.
|
50 MW CEA threshold for generators and storage (as reported) |
1 Apr 2027 CEA Regulations in force |
6 hours Incident reporting (as reported) |
May 2027 Most DPDP obligations take effect |
|
Market segment |
Landscape and buying behaviour |
Cybersecurity opportunity |
|
Large IPPs and PSUs |
Gigawatt portfolios, many OEMs |
Programme-level OT security, SOC, audits |
|
Developers and mid-sized operators |
Fast-growing portfolios |
CEA gap assessments, vendor access, monitoring |
|
Storage operators |
New, safety-critical assets |
EMS/BMS testing, OT monitoring |
|
AMISPs and O&M firms |
Service providers to many owners |
Platform, head-end and access security |
2. Business drivers
|
Business driver |
Buying trigger |
Relevant services |
|
Regulatory compliance |
CEA Regulations from April 2027 |
Gap assessments, policies, audits |
|
Availability and PPAs |
Curtailment and outages cost revenue |
Monitoring and resilience |
|
Lender and investor diligence |
Cyber risk in financing reviews |
Independent assurance |
|
Insurance |
Insurers ask about OT controls |
Control validation |
|
Acquisitions |
Portfolio consolidation |
Post-acquisition security reviews |
3. Technology drivers
|
Technology driver |
Exposure created |
Codec Networks opportunity |
|
Inverters and controllers |
Firmware flaws and default credentials |
Device testing and hardening |
|
OEM clouds |
Fleet-wide remote control |
Vendor cloud reviews |
|
Battery systems |
Safety-impacting manipulation |
EMS/BMS testing |
|
Remote connectivity |
Disruption and exposure |
Connectivity resilience reviews |
|
Smart meters |
Head-end and update attacks |
AMI testing |
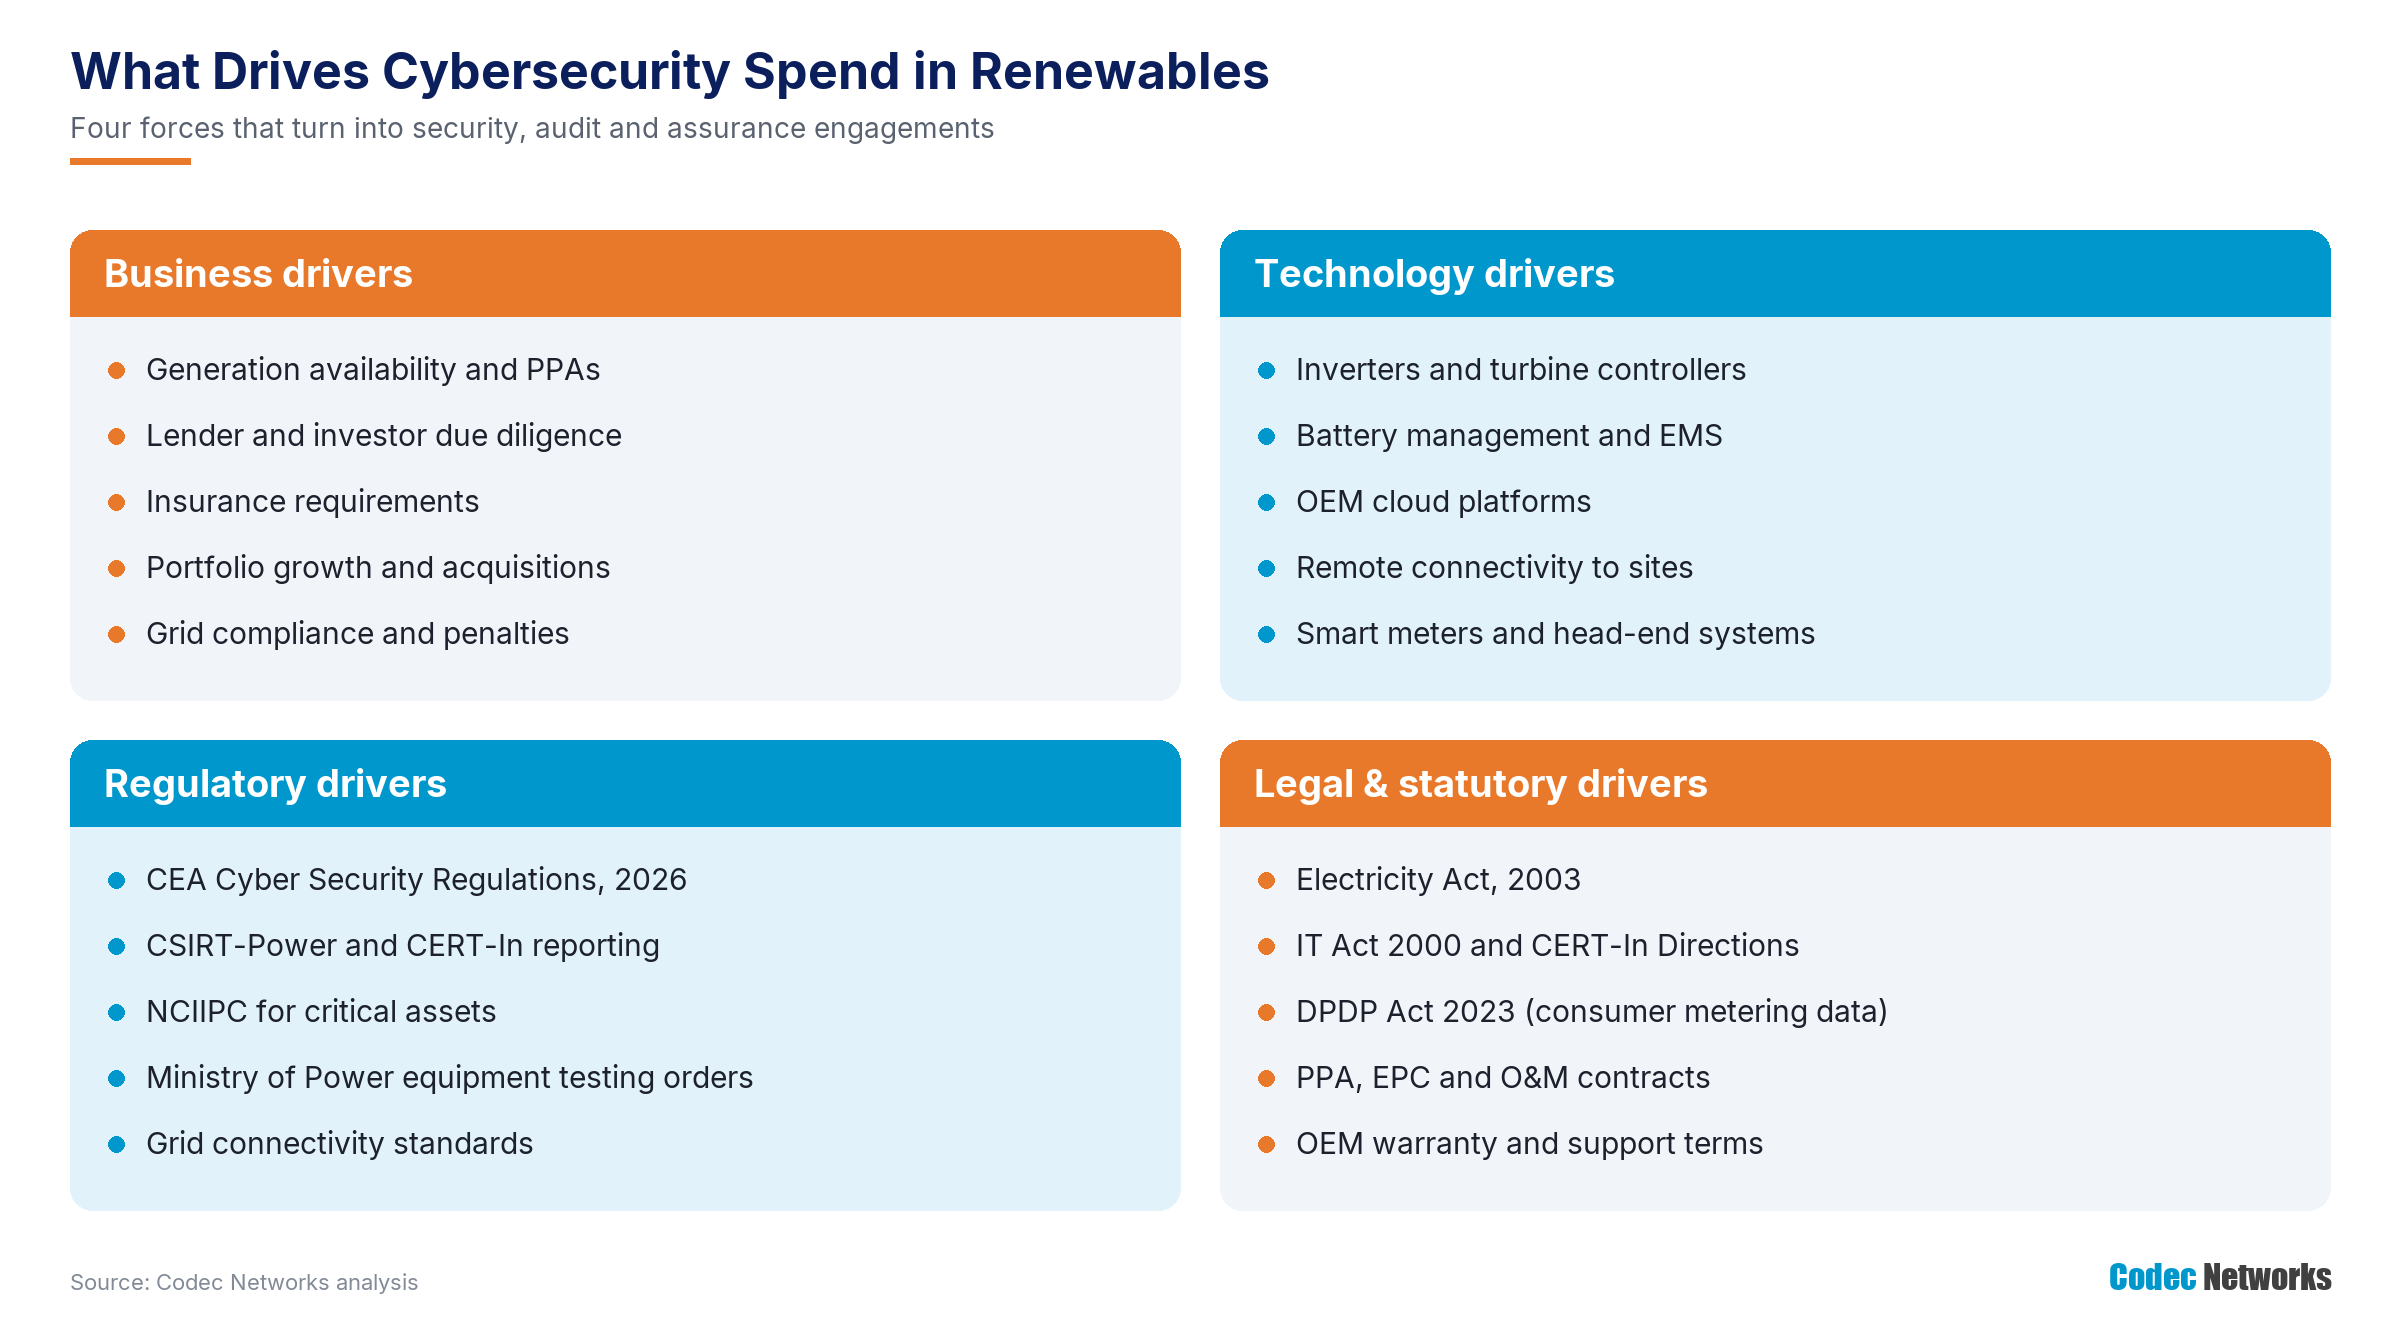
Figure 3: The four groups of drivers behind cybersecurity spending in renewables.
4. Regulatory drivers: CEA Regulations 2026, CERT-In and DPDP
|
Instrument |
Key requirements |
|
CEA (Cyber Security in Power Sector) Regulations, 2026 |
Notified 31 July 2026; in force 1 April 2027; cover generators, captive plants and storage of 50 MW and above (as reported) |
|
Governance and assurance |
CISO, 24-hour ISD, policy, crisis plan with annual drill, annual audit, OT separation, vendor accountability (as reported) |
|
Incident reporting |
CSIRT-Power and CERT-In within six hours (as reported) |
|
CERT-In Directions (2022) |
Six-hour reporting and 180-day logs for all body corporates |
|
DPDP Act 2023 and Rules 2025 |
Consumer metering and service data; most obligations from May 2027 |
|
Confirm against the gazette Thresholds and requirements are summarised from public reporting; confirm against the official gazette notification. |
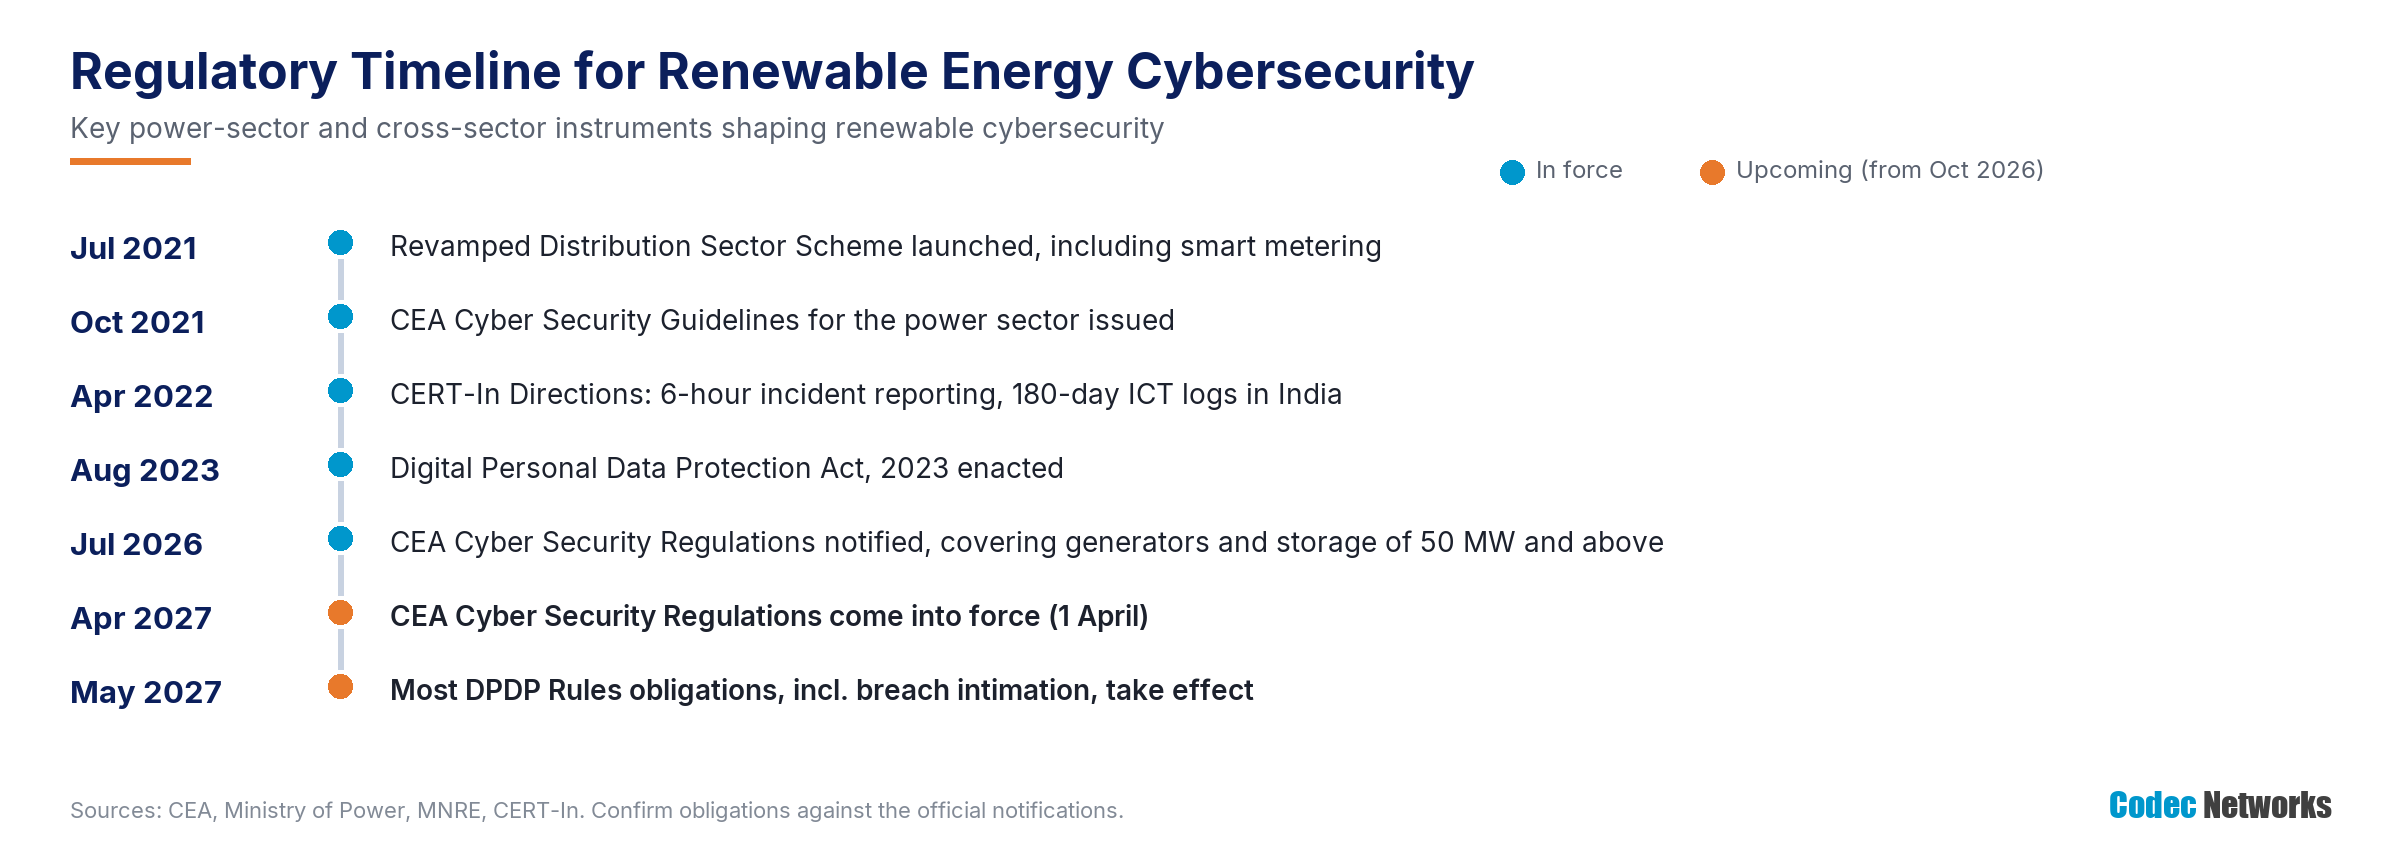
Figure 4: Regulatory timeline for renewable energy cybersecurity, as of October 2026.
5. Legal and statutory drivers
|
Law or obligation |
Relevance |
Demand created |
|
Electricity Act, 2003 |
Generation, storage and grid connection |
Compliance with CEA regulations |
|
IT Act, 2000 and CERT-In Directions |
Incident reporting and logs |
SOC and logging |
|
DPDP Act, 2023 and Rules, 2025 |
Consumer metering data |
Privacy programmes for AMISPs |
|
Grid connectivity and scheduling rules |
Operational obligations |
Data integrity and resilience |
|
Contracts |
PPA, EPC, O&M, OEM and AMISP agreements |
Security obligations and evidence |
6. How the drivers differ by player type
|
Player type |
Dominant business drivers |
Dominant technology drivers |
Principal regulatory drivers |
|
Solar and wind operators |
Availability, lender confidence |
Inverters, controllers, OEM clouds |
CEA Regulations, CERT-In |
|
Storage operators |
Safety, availability |
EMS, BMS |
CEA Regulations, CERT-In |
|
Asset managers and O&M |
Client trust |
Portfolio platforms, remote access |
Contracts, CERT-In |
|
Smart meter providers |
DISCOM contracts, reliability |
Head-end, updates |
DISCOM contracts, DPDP, CERT-In |
7. What this means for buyers and for Codec Networks
|
Customer buying need |
Recommended offering |
Natural recurring engagement |
|
“Are we covered by the CEA Regulations?” |
Applicability and gap assessment |
Annual audits |
|
“Who can control our fleet remotely?” |
Vendor access and cloud review |
Quarterly recertification |
|
“What is inside our new inverters?” |
Equipment inspection |
Per-procurement inspection |
|
“We need 24x7 fleet monitoring.” |
OT and cloud monitoring |
Continuous monitoring |
|
“Lenders want cyber assurance.” |
Independent assurance report |
Annual reporting |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: This document is general industry guidance based on public information available as of October 2026. CEA (Cyber Security in Power Sector) Regulations, 2026 details are summarised from public reporting; confirm obligations against the official gazette notification and MNRE, CEA and CERT-In instruments.